

My superpower is wondering “what happens if I do this” and then somehow causing epic drama.
Bangalore, India
Joined February 2007
- Tweets86K
- Following2.9K
- Followers20.4K
- Likes10.4K




Kiran Jonnalagadda retweeted

I got this joke when I was 8.
The internet revealed to me that there are now 20 years old who don’t get it.

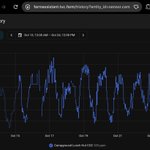
Meshtastic → LoRa → WiFi → MQTT → Home Assistant → Hand rolled fiber optic → Cloudflare Tunnel → Google Sheets → Public website widget here. So many moving parts to nail down for reliability. So much fun. tvc.farm/ecosystem/weather/

Here's a CO2 sensor on the edge of a forest documenting the daily photosynthesis cycle. My 12 y.o.'s textbooks describe this in the most banal language. I learnt this decades ago in school and never connected the dots. This year the itch asked to be scratched.

ALT CO2 sensor log graph from a tunneled Home Assistant graph.
Kiran Jonnalagadda retweeted

PSA for macOS users:
1. Apple’s supplied SSL certificate bundle at /etc/ssl/cert.pem still trusts certificates attackers can forge using compromised eMudhra keys.
2. I confirmed this on macOS 26.7.1 and 27.0.1 using Apple’s built-in curl and Git.
3. An attacker intercepting connections from tools using this bundle could replace downloads with malware. With commands like curl … | sh, that malware would execute immediately.
4. Removing the roots that authorize those certificates blocks the tested chains. Both OS updates restored roots I’d previously removed, requiring me to remove them again.
4. I’ve submitted the findings to Apple’s security team and am awaiting their response. In the meantime, you can apply a temporary fix as outlined below.
5. To check and fix your machine, give an agent like ChatGPT/Codex or Claude Code the following prompt:
“Independently verify whether Apple’s /etc/ssl/cert.pem still permits trust in certificates signed with compromised eMudhra keys. If so, back it up and remove the roots enabling that trust, identified by verified SPKI fingerprints. Confirm Apple’s built-in curl and Git reject those chains while ordinary HTTPS still works. Preserve rollback and never disable TLS verification.”
Note that removing these roots can also block legitimate sites. This is a temporary mitigation, not a substitute for a fix from Apple.
I’ll share the script I used in a follow-up post if you’d prefer to use that directly.

PSA for Codex CLI users:
1. Codex 0.163.0’s release lockfile pins rustls-webpki 0.103.15 and root bundles that can still trust compromised eMudhra certificates.
2. An attacker intercepting your connection could impersonate a server, steal sensitive data, or alter responses, potentially tricking Codex into running malicious commands.
3. Codex 0.164.0, released October 23 at 12:48 a.m. ET, updates those dependencies to fixed versions.
4. To check your codex version run "codex --version". It should be at least 0.164.0.
5. To patch the vulnerability, run "codex update".
6. Apps that bundle their own Codex copy must also be checked.

Kiran Jonnalagadda retweeted

Election Commission’s software has made a massive blunder. It’s translating Hindi/Urdu names by treating them as if they were English.
For example, the name was Muhammad Iqbal Beg, but the software turned it into “Mohammad Iqbal Bheek Mangte Hain”.
Another example: A woman’s name was Phool Kali Devi, and the software changed it to “Murkh Kali Devi” .
Absolute chaos, what’s going on?

Kiran Jonnalagadda retweeted

The closest we have come to getting an independent audit of the EVMs.

🇮🇳 🚨 INDIA: EVIL MARKHORS CLAIMS BREACH OF BHARAT ELECTRONICS (BEL), DEFENSE FIRM'S PERSONNEL AND SHAREHOLDER KYC DATA ALLEGEDLY LEAKED
The hacktivist group Evil Markhors claims it breached Bharat Electronics Limited (BEL), India's state-owned defense electronics manufacturer, and leaked about 1 GB of internal data (around 1,069 files).
The actor claims:
* A roster of roughly 18,000 to 19,500 retirees and spouses
* 23,553 shareholder KYC records, including PAN, Aadhaar and dates of birth
* More than 50,000 rows of recruitment candidate data
* Around 6,000 health-benefit portal accounts, working login credentials and organizational digital-signature private keys
⚠️ Analyst Note:
If real, the Aadhaar and PAN data puts shareholders and staff at high risk of identity fraud and targeted phishing, and stolen credentials or signing keys could be used against BEL systems and its defense supply chain. Hacktivist groups in this space have a history of exaggerated claims. BEL has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #India #Defense #DataBreach #ThreatIntelligence

Kiran Jonnalagadda retweeted

Calling it now: Chrome and Mozilla will remove eMudhra as a G1 root, nulling them as a CA.
On 20 Oct, eMudhra had 24 hours to give an explanation of what exactly happened with the mis-signed certificate. They did not; asked for more time; and now blame “investors/customers” 🤡

Kiran Jonnalagadda retweeted

Neha Bora: “Peace cannot simply be declared by those who hold power. It must be experienced by the people …
Democracy does not promise us a society without disagreement. It promises us a way of living with disagreement without denying one another dignity, freedom and equality.”
Kiran Jonnalagadda retweeted

The X account of betting platform @Polymarket account is now withheld in India.
This development has no relation to the fact that they ran below poll during the CJP protests in Delhi

Kiran Jonnalagadda retweeted

The first step towards dealing with a colossal fuckup is to acknowledge that it is a colossal fuckup, instead of trying to weasel out of it with ad hominem against ppl explaining the seriousness of this colossal fuckup.
Our bureaucrats treat Yes Minister as guidance not parody.

Kiran Jonnalagadda retweeted

you're just going about your day and you now get to read stuff like "Trump says Sundar Pichai talked him out of renaming the Atlantic Ocean" and you just have to nod and move on with your day.
“Oceans are different, sir.” lmao
theverge.com/policy/1016751/…

Kiran Jonnalagadda retweeted

The GRU hacked into Jared Kushner's iPhone. Dutch military intelligence (MIVD) then recruited a GRU spy who gave them access to the hacked phone. What MIVD discovered was that Kushner had access to two bank accounts --one Azerbaijani, the other Israeli --where Saudi Crown Prince Mohammed bin Salman and Emirati ruler Mohammed bin Zayed deposited money. It sounds like a slightly far-fetched episode of "Slow Horses," but it's real. And it proves just how eye-poppingly corrupt this administration was and continues to be as its "special envoy" decides the fate of tens of millions in Europe in the Middle East. Simply incredible reporting by Matthew Cole, drawn from his new book on Kushner. vanityfair.com/story/jared-k…


Kiran Jonnalagadda retweeted
I suspect the real reason eMudhra is exiting the SSL business is Google indicated it is most likely going to drop eMudhra from being trusted by Chrome AT ALL, after observing inexplicable incompetence in how they mis-generated their private key for the CA certificate.

Kiran Jonnalagadda retweeted

BREAKING: eMudhra exits SSL/TLS certificate business, blames social media instead of incompetence for the same

Kiran Jonnalagadda retweeted

So this is an interesting story. How eMudhra became the foundation of global internet. Im surprised that no news channels are digging up the root CA history. Maybe people dont know that this is public information.
groups.google.com/g/mozilla.…
So this is the discussion list for mozilla security policy back in 2018. When emudhra first applied for inclusion as a root ca.
One of the maintainers questions eMudhra's credentials as an "Indian co".
The filing in response is very interesting.
"eMudhra has been a licensed CA under
Controller of Certifying Authorities which operates the Indian
Government Root for more than 10 years and is also a licensed CA in
Mauritius under Ministry of IT, Mauritius. eMudhra has issued over 35
million digital certificates (3% of India’s population).
eMudhra is a critical partner to Digital India and supports the usage of
digital signatures on a variety of eGovernance platforms for
Government of India including Company Law Board, Income Tax, Goods
and Service Tax (GST / VAT), eProcurement, Travel Portals, Customs,
Banking etc. eMudhra’s solutions power digital signature and other
multifactor authentication for over 35 Banks which include domestic
and global Banks. eMudhra also has a proprietary CA solution which is
today used by the Indian Army and other defense establishments."
Eventually mozilla HAD to accept, because emudhra claimed publicly - "But this was not a complete Webtrust audited setup. Rather, it is under Government of India." – at San Francisco, CA


Kiran Jonnalagadda retweeted

The important thing with incidents like @eMudhra is to proceed openly and by engaging with the communit… ah crap


Global TLS Intermediate CA incident: We’ve updated our incident page with how it happened, who is affected (one US customer ecosystem), what’s not affected, and what we’re putting in place. We will publish the root cause once our investigation is complete.
👉emudhra.com/en/post/certific…
Readers added context they thought people might want to know
eMudhra minimizes the scope by claiming only "one US customer ecosystem" is affected. In reality, 8 of its CA certificates had catastrophically weak private keys (one being simply the number 4), allowing anyone to forge trusted HTTPS certificates for any website on the internet.blog.google/security/prote…