

Jacob P retweeted

A follow up on last week’s FileFix blog.
FileFix (Part 2)
mrd0x.com/filefix-part-2/


Jacob P retweeted

I believe there is a simple way to remediate #ESC15
Wrote a PowerShell script for it: github.com/JonasBK/Powershel…
🧵 1/5

Jacob P retweeted

Want to check for #ESC15 ? Use the following cypher with #BloodHound
MATCH p=(:Base)-[:MemberOf*0..]->()-[:Enroll|AllExtendedRights]->(ct:CertTemplate)-[:PublishedTo]->(:EnterpriseCA)-[:TrustedForNTAuth]->(:NTAuthStore)-[:NTAuthStoreFor]->(:Domain) WHERE ct.enrolleesuppliessubject = True AND ct.authenticationenabled = False AND ct.requiresmanagerapproval = False AND ct.schemaversion = 1 RETURN p
Thanks @Jonas_B_K
More information available here: trustedsec.com/blog/ekuwu-no…

Jacob P retweeted
More ADCS attack paths in BloodHound! 🧩🔍
This blog post is about implicit mapping abuse and how we have implemented ESC6, ESC9, and ESC10.

Ready for more AD CS in BloodHound? After covering ESC1, Golden Certificates, & ESC3, @Jonas_B_K is back with Part 3, focusing on new edges with ESC6, ESC9, and ESC10 domain escalation techniques.
Check out the latest post to learn more! ⤵️ ghst.ly/3XE4Bfh
Jacob P retweeted
I have written a blogpost with Jakob Mollerup about the diffence between NT AUTHORITY\SERVICE and NT SERVICE\ALL SERVICES because we found the existing documentation to be a bit too brief
#Windows #sysinternals
blog.improsec.com/tech-blog/…

Jacob P retweeted
Wrote a blog post about a new ADCS abuse technique involvering issuance policies and OID group links 📝 posts.specterops.io/adcs-esc…

Jacob P retweeted
ADCS attack paths in BloodHound! 🥳
This blog post breaks down the implementation of the ESC1 requirements and guides you on effectively leveraging BloodHound to identify attack paths that include ESC1 privileges.
posts.specterops.io/adcs-att…
Jacob P retweeted

I am releasing my book on email security for free, you can get it here:
leanpub.com/emailsecattackan…
Share as you wish.
Merry Xmas to all my fellow hackers

Jacob P retweeted
Last week @_wald0 and I presented a webinar about the workings of ADCS and how we are implementing the ADCS attack paths in BloodHound. You can watch the recording here :)
ICYMI: Our ADCS Attack Paths in BloodHound webinar presented by @_wald0 & @Jonas_B_K is now available to view on demand!
Learn all about the latest feature in BloodHound 👉 ghst.ly/47oBWNg

Jacob P retweeted

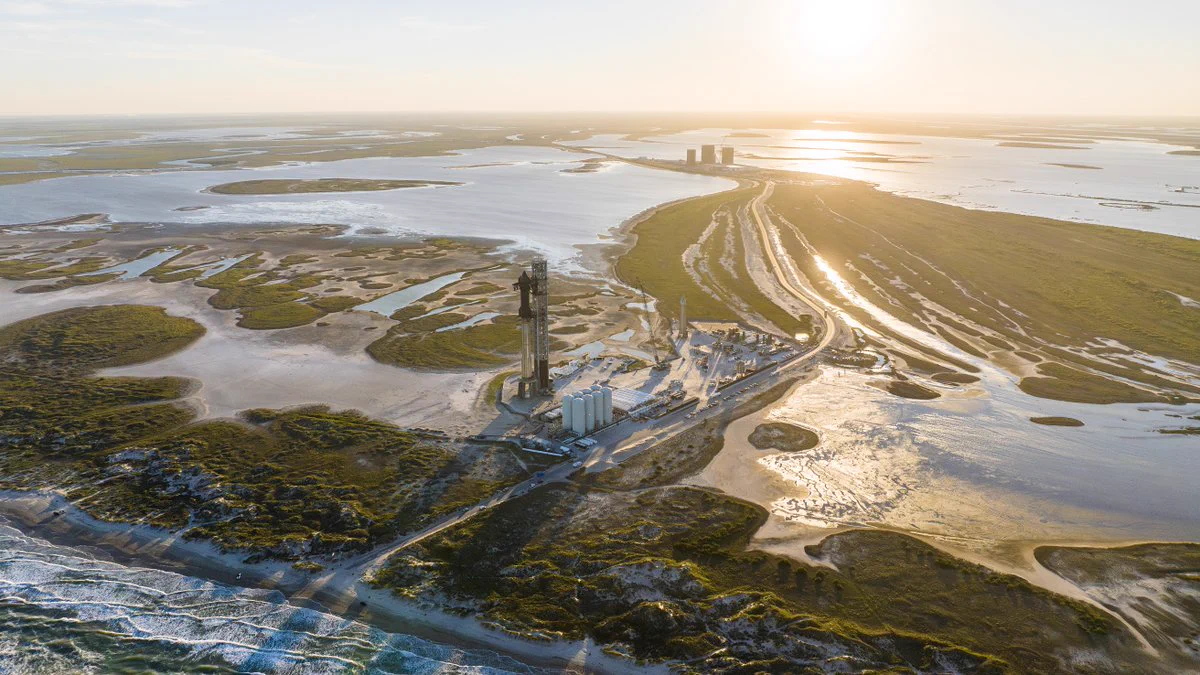
Starship launch live broadcast
xitter.cf/i/broadcasts/1dRKZEWQv…
Jacob P retweeted

New #BloodHound documentation: Getting started with BloodHound Community Edition
It's describing a short step-by-step process of deploying and using #BloodHoundCE
support.bloodhoundenterprise…
Jacob P retweeted
If ever there is still someone using RSH out there, you should consider moving away from it:
bencteux.fr/posts/netkit_rcp…
Jacob P retweeted
Our ‘What is Tier Zero’ blog post is out! 🚀 posts.specterops.io/what-is-…
It'll be the first in a series where we'll deep-dive into the critical assets of AD and Azure. We will build out a Tier Zero table with all the assets we consider throughout the series.
Jacob P retweeted
Let's define Tier Zero! 📽️🔼
Join @elad_shamir and me for our webinar "Defining the Undefined: What is Tier Zero?" on June 22nd. It will be the first in a @SpecterOps series on this topic where we'll deep-dive into the critical assets of Active Directory and Azure.
Join @elad_shamir & @Jonas_B_K on Thurs., June 22 in part one of our webinar series to define the critical identities & resources once and for all across Active Directory and Azure.
Register: ghst.ly/42iswQy

Jacob P retweeted

Released a new Backup Operator to Domain Admin tool. It contains 4 different methods for escalation, more methods will be added: github.com/improsec/BackupOp…

Jacob P retweeted

In a new blog post, Security Advisor Martin Sohn Christensen provides system administrators with a starting point for securing their AD and how to identify and prioritize low-hanging security risks. improsec.com/tech-blog/basic…

Jacob P retweeted
Get insights into risk management and how it can be used as a tool to bridge cyber security to the management level.
Listen in to learn what cyber risk management is, and how you can apply security risk in an enterprise risk setting.
Register today improsec.com/morningtech

Jacob P retweeted

Have you ever wondered how RODCs work and whether compromising one would necessarily allow for privilege escalation?
The answers are in my new post:
At the Edge of Tier Zero: The Curious Case of the RODC
posts.specterops.io/at-the-e…
Jacob P retweeted

Fetch Defender exclusions from Intune managed devices as non-admin user:
Export management log files
Extract cab file
Review MDMDiagHtmlReport.html
Search for "Excluded Processes" and "Excluded Paths"
Cherio
#pentest #redteam #tipswednesday #thankmelater

