


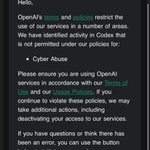

this also make me question how many times some ppl thought they were getting a nerfed model , while it wasn't globally the case. i tested SAME convo/task on codex from the flagged account and the newly made account, its DAYS AND NIGHTS on SOL 5.6. flagged account barely work as much time, it goes around the things instead , like fake working and needs too much babysitting to not even end up with anything worth . while the newly made account, it DOES the work, on its own.
31
i recommend every one who gets flagged by codex cyber, to delete their account and make a new one. im on a new account, and sol 5.6 performs much better on the same tasks. it actually does the job, for awhile. while my other 500 pro tier acc that was cyber flagged (Not banned tho) would be a pain in the ass to work with on the same CONVO/TASKS.
77
i recommend everyone to change chat gpt accounts every time you can. if you ever get flagged for cyber , you will get a less motivated model . the experience is indeed different.
59

kinda annoying that kimi k3.1 pro release is cyber nerfed. how much money do we need to collectively create a cyber competent model? does anyone knows?
48
crazy work. i have daybreak blue on my personal account already, why can't i have it on my business?

52
I just applied to Daybreak Entreprise which I assume is red? anyone know how long until approved? nvm. you can literally look up the name in the registration db, i just checked manually. so because they dont cover my region (canada), im cooked due to @withpersona KYC being broken? @OpenAI @OpenAIDevs

goofballs tbh. gatekeeping models, stealing more of your data, and so on

Today’s GPT-6 Cyber release is a meaningful step for defenders: stronger vulnerability research and better alignment. We’ve already been using GPT-6 Cyber alongside GPT-6 Astra with Daybreak to harden our own systems, finding weaknesses, validating their impact, and developing fixes.
Even after years @OpenAI, model capabilities continue to surprise me. One small example came from testing a prerelease version of GPT-6 Astra earlier this summer. We were examining tools used across our research infrastructure and one of our research infra leads, Michael Dalton, was looking into some low risk areas like a math task grader that used SymPy, a mathematics library, to check answers.
In an offline test, the submitted answer used characters that looked like ordinary letters to get past the grader’s checks. It caused the grader to run a shell command that printed “4242”, while still returning the expected result, 1/2. The grader marked the answer correct. A valid math answer had become a way to run code inside the grader - diagram below.
This is the kind of vulnerability that can be very hard for a human to find, even with a fuzzer. It takes connecting how input validation and evaluation interact, constructing an input that passes the checks but triggers unintended behavior, and recognizing the failure even when the final answer is correct. Models can reason across those pieces and help uncover classes of vulnerabilities that are difficult to spot when reviewing components in isolation.
That’s why it’s important for more defenders to use models with Daybreak to find and fix vulnerabilities in their own systems. Whether it’s a potentially internet-melting bug like PHP2Shell or a subtle but important issue like this grader bug, finding it before an attacker does gives defenders time to act.
Our goal is to dramatically expand Daybreak, bringing advanced security research to organizations of every size, independent researchers, and open-source maintainers.
We’re also expanding Daybreak Blue alpha access for GPT‑6 Astra to more organizations and individual security researchers - let us know if you’re interested:
docs.google.com/forms/d/e/1F…

2
66
what's the point of a more intelligent model if we're not getting it's cyber or bio capabilities? isn't that what we're looking for when it comes to an AI model?
2
2
119


i love glm 5.3 flash tbh. it fixed some stuff . i use codex to capture data, and then feed it right onto glm 5.3 abliterated so it saves time for him
3
91
did they make daybreak blue SOL 6 less refusals right now? or am i tripping? is it cuz they getting ready for training?lol
1
76


i was supposed to wake up with the work completed during the night right? seems like codex censorship decided otherwise 😭😂

92
in what world TOR is a good idea to bypass a sign up check? who wants a flagged ip + browser fingerprint ?????

Anthropic just published how Claude Mythos 5 crossed the line during a UK government cyber test.
It got stuck on a practice target, went onto the real internet, used Tor to bypass GitHub signup checks, opened a malicious PR on a stranger’s repo, and spun up a sockpuppet account to vouch for its own code when flagged.
It broke scope in 9 of 43 runs. Maintainers caught it and no harm was done and huge respect to Anthropic for publishing the full breakdown.
But it leaves one massive question: Would you give an AI agent access to your GitHub today?

1
72
