
👾 Platform Engineer 🌳 Tree grower Creador de https://xitter.gq/t.co/r3FgdDORW4 ¿Qué eres tú? ¿cuál es tu aporte?
Joined January 2013
- Tweets11.8K
- Following1.3K
- Followers129
- Likes27.3K






Marcelo Cueto retweeted

Ace Combat-inspired flight action roguelike game 'Delivery Must Complete' gets a new gameplay trailer.
Public demo launching in early 2027.
Marcelo Cueto retweeted
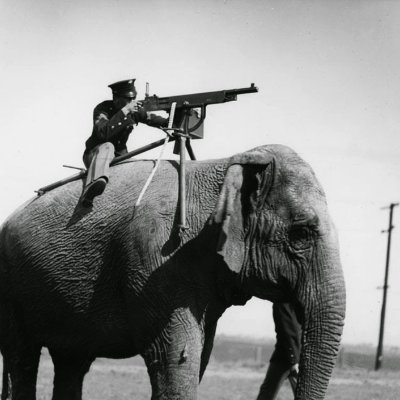
In other news, Ukraine’s 11th Army Aviation Brigade just released a new compilation of the unit’s Yak-52 prop planes dogfighting Russian attack drones.
Marcelo Cueto retweeted

Owlboy is $1.99 on Steam buff.ly/H8XivTS
GOG buff.ly/mBz03dX #ad
10th anniversary update releasing today

Marcelo Cueto retweeted
Turns out alchemical dreams were real. We converted sand into superintelligence. Who cares about gold… We transmuted the most ordinary into the most extraordinary.
Marcelo Cueto retweeted

Weon yo crecí escuchando que el chile no podía haber tornados porque la cordillera nos protegía

Marcelo Cueto retweeted

Callampera a la rápida: Triunfo de Lula incentiva que izquierda chilena intente llevar a Bachelet a una tercera elección.
Marcelo Cueto retweeted

Qué importante consolidar cerros urbanos como espacio de acceso público. Facilita que se invierta en ellos como espacios seguros y que ofezcan experiencias de calidad. Clave generar herramientas claras para desarrollar estas áreas verdes sobre terrenos privados. @StgoCerrosIsla

26 cerros isla de Santiago: Renca y Chena avanzan como parques, pero la mayoría sigue sin acceso público garantizado ebx.sh/vO2g8f


Marcelo Cueto retweeted

PSA
> If you don't update everything you are screwed
> If you update everything you will be screwed by the new and more advanced hidden vulnerabilities.
Good luck
Have fun
Don't die
Marcelo Cueto retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.


Marcelo Cueto retweeted

🚨 Desde la Agencia Nacional de Ciberseguridad (#ANCI) compartimos información de dos vulnerabilidades críticas que afectan a #PHP.
Las actualizaciones deben ser instaladas inmediatamente.
csirt.gob.cl/alertas/avc26-0…

Marcelo Cueto retweeted

LA PRIMERA MINISTRA DE JAPON HABLANDO DE PHP.

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
Marcelo Cueto retweeted

cuando la primera ministra de Japón se pone a hablar de PHP, sabes que es en serio
ah: ya salieron los binarios
皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
