

Computer Doctor | We stop ransomware, exploits, hacker tricks on-device | Sophos Endpoint & HitmanPro dev | Tweets are my own
Hengelo, The Netherlands
Joined July 2010
- Tweets3.1K
- Following961
- Followers4.1K
- Likes1.4K




Pinned Tweet
LockFile ransomware attempts to evade protection with 'intermittent encryption' and making Windows write the encrypted documents for them, throwing off statistical content analysis and runtime behavior detection. Get the lowdown in our dissection 101: news.sophos.com/en-us/2021/0…
Mark Loman retweeted

How Do You Get Hacked With Zero Malware?
WantToCry brute forces exposed SMB shares, steals your files, encrypts them on the attacker's infrastructure, then writes them back.
We walk through the attack step by step 👇
youtu.be/YWSefucL0W8

"Exploit mitigation" stalled around 2008. The attacks didn't.
AI turns a patched bug into a working exploit in hours. Why endpoint exploit mitigation stalled in 2008, and what a default-on mitigation layer looks like now: sophos.com/en-us/blog/sophos…

Mark Loman retweeted

AI is most effective against attackers when it is embedded into orchestrated defense.
Sophos has joined the @OpenAI Daybreak Cyber Partner Program, bringing leading cyber-capable models directly into the defensive workflows our teams already run.
🔗 sophos.com/en-us/press/press…
Mark Loman retweeted
For five years, Sophos engaged in defensive and counter-offensive operations against China-based, state-sponsored threat actors.
Now @DarknetDiaries, the most popular cybersecurity podcast in the world, has spent 90 minutes telling the full story.
🎧 darknetdiaries.com/episode/1…
Ransomware: AI changes the writer. It doesn't change the math.
Why most endpoint protection still treats ransomware as just another piece of malware, and what changes when you watch the data instead of the attacker. sophos.com/en-us/blog/sophos…

AI finds bugs faster, but hasn't changed how they're exploited. Sophos targets the primitives, not the provenance. AI-written or manual: they hit the same architectural wall. We build the friction where defenders win, on every process, by default: sophos.com/en-us/blog/sophos…

Waar zit je aanvaller écht? Mijn onderzoek met de CTU toont hoe cloud VM's "rogue insiders" worden:
1️⃣ Geo-blocking omzeilen 🌍 2️⃣ Via RDP/VPN je infra in; de VM wordt deel van jouw netwerk 3️⃣ Remote encryptie via SMB (geen lokale signalen!)
Details: sophos.com/en-gb/blog/malici…

Mark Loman retweeted

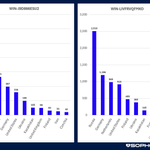
It started with #WantToCry and machine names WIN-J9D866ESIJ2 & WIN-LIVFRVQFMKO turned out to be a rabbit-hole of baddies
sophos.com/en-us/blog/malici…

.@StealaBrainrotR Security concern: Unknown player appeared in our private server during Gingerbread Town Event and last night during Christmas Eve admin event, a paid Festive 67 was removed from my son's base while allowed players were asleep. Looks like an exploit. Please act.
A Chinese APT leveraged Claude AI to run an end-to-end intrusion — recon, exploit generation, lateral movement — all executed via Anthropic’s own systems.
Defenders are officially in a new era. anthropic.com/news/disruptin…

Mark Loman retweeted
Threat actors regularly look for ways to disable security products. Tamper protection – a mechanism designed to stop threat actors from interfering with security products – is therefore a critical part of any security suite.
Mark Loman retweeted
At the end of 2023, Sophos X-Ops noted a 62% year-on-year increase in ‘remote encryption’ attacks – where ransomware attackers compromise an unmanaged or under-protected endpoint, and leverage that access to encrypt data on managed, domain-joined machines.
Mark Loman retweeted
Everyone says Europe can't compete with America in tech.
But 48 hours ago, Mistral's 'Le Chat' just proved them wrong:
• 13x faster than ChatGPT
• 100% open-source
• Completely free (vs $20/month)
The European AI breakthrough Silicon Valley didn't see coming 🧵:


Mark Loman retweeted

Ik bestelde een McCrispy, niet een McPlastic. Is dit wat jullie bedoelen met transparantie over voeding, want dit is zeker ‘kraakhelder’ zoals jullie het zelf noemen, @McDonaldsNL 🤷♀️🍔

Mark Loman retweeted
Chester Wisniewski, Director and Global Field CTO, shares insights from a five-year operation countering state-sponsored adversaries.
Listen to our latest Inside Pacific Rim entry as Chester and Joe Levy, CEO, discuss key findings in this six-part series: bit.ly/42iBVvk
Inside a Firewall Vendor's 5-Year War With Chinese Hackers Hijacking Its Devices: Sophos went so far as to plant surveillance “implants” on its own devices to catch the hackers at work, revealing a glimpse into China's R&D pipeline of intrusion techniques: wired.com/story/sophos-cheng…
For 5 years, Sophos has been engaged in defensive and counter-offensive operations against China-based #NationState adversaries targeting perimeter devices like #firewalls for surveillance and sabotage. For the full story, please see our landing page: sophos.com/en-us/content/pac…
This week, Sophos participated in Microsoft’s Windows Endpoint Security Ecosystem Summit. This article provides context and general information about the landscape: Standing on the Windows platform, waiting for change news.sophos.com/en-us/2024/0…
🚨 Ransomware still beats up-to-date protection - even decade-old strains! Want to know how? See @AltShiftPrtScn in "Know the Enemy". Wednesday, August 7, 11:25 am – 12:15 pm (Business Hall Theater A) More: blackhat.com/us-24/sponsored… #BlackHat

