
detection engineering, malware analysis, IR, threat hunting #DailyThreatHunt, threat intel, blue team, Qradar, Author of now archived @PhishKitTracker project
United States
Joined June 2009
- Tweets10.3K
- Following312
- Followers3.3K
- Likes12.3K



Pinned Tweet
3 months of threat hunt ideas , hopefully enough to get a new team started , or to give an existing team a few new ideas. Go #blueteam ! #DailyThreatHunt #threathunt

Day #1: Today starts the #DailyThreatHunt challenge! Post your unique #threathunt ideas to the world. Help the #blueteam fight the good fight by helping those orgs that don’t know where to start. Make threat hunting the new norm.
neonprimetime.blogspot.com/2…
Hunt 🧐 Ideas below 👇
neonprimetime retweeted

🚨 Reports of NetScaler Incidents After Latest Patch Raise Concerns Over Continued Exploitation
Multiple Citrix administrators are reporting suspicious activity affecting NetScaler appliances even after updating to version 14.1-73.37.
The reports surfaced on Reddit, where one administrator said multiple customers experienced incidents that caused externally accessible NetScaler appliances to repeatedly reboot.
Other administrators reported similar behavior on newly rebuilt appliances, including systems where Enhanced ISN Generation had already been enabled. Several affected organizations said they collected forensic data and opened cases with Citrix.
It is currently unclear whether the activity represents successful exploitation of a new or existing vulnerability, residual compromise, vulnerability scanning, or an issue with the updated firmware.
The reports come days after Citrix disclosed active exploitation of CVE-2026-88771 and CVE-2026-88772, two critical vulnerabilities affecting NetScaler ADC and NetScaler Gateway.
The latest post-patch activity has not yet been confirmed by Citrix as exploitation.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing


neonprimetime retweeted

pdf-converkit[.]com
dish-desk[.]com
kitchen-canvas[.]com
these also are getting winrar at the time of this post. Similar looking advertisers and pages. I suspect these are just being staged and really just downloading Winrar or Okular until an official campaign launch. Maybe?

neonprimetime retweeted

Just tagged and upload related samples
👇
bazaar.abuse.ch/browse/tag/1…
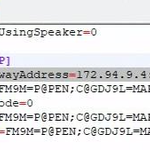
Client32.ini
MD5 0a2d1917facd568775ee744d180de1a9
#netsupport #rat
GatewayAddress=172.94.9.]4:443
cc @skocherhan @500mk500


#ClickFix => #DonutLoader => #NetSupportRAT active right now 3/11/2026
step by step
1 - legit website loading malicious content
2 - shows ClickFix popup
3 - copy & paste powershell cmd & run it
... continued ...
1 of X (thread)

We started with #ClickFix putting #DonutLoader into memory and end with #NetSupportRAT
12 - #NetSupportRAT connects to it's C2 located in #Iran
172[.94[.9[.4
Hope this is helpful to the community!
7 of 7 (end of thread)


neonprimetime retweeted

> check virustotal
> uploaded 23 mins ago
> AMOS stealer
ah ok, so if you installed this skill it would just silently steal all your passwords and banking information and stuff. no big deal
virustotal.com/gui/file/3c9d…
neonprimetime retweeted

Microsoft Defender researchers observed attackers using yet another evasion approach to the ClickFix technique: Asking targets to run a command that executes a custom DNS lookup and parses the `Name:` response to receive the next-stage payload for execution.

neonprimetime retweeted
In the latest DNS-based staging using ClickFix, the initial command runs through cmd.exe and performs a DNS lookup against a hard-coded external DNS server, rather than the system’s default resolver. The output is filtered to extract the `Name:` DNS response, which is executed as the second-stage payload.
This technique uses DNS as a lightweight staging or signaling channel, allowing the attacker to:
- Reach attacker-controlled infrastructure
- Gate or validate execution of the second-stage payload
Using DNS in this way reduces dependency on traditional web requests and can help blend malicious activity into normal network traffic.

ALT DNS lookup against a hard-coded external DNS server, rather than the system\u2019s default resolver. The output is filtered to extract the `Name:` DNS response, which is executed as the second-stage payload.
neonprimetime retweeted

"aiBrowser Setup" software - no noted malicious behavior but callback domain registration + parent company domain registration appears sketchy.
Thumbprint: 257A074A90E6243B65EF49C092AE9CCE61EBEE19
SHA-256: 3c72eedf299c584ec7c38e5ba004c12248706a8c92adc555a2fd2ddeb800d816
neonprimetime retweeted

User reports indicate problems with GitHub since 9:22 AM EST.
How is it affecting you? #GithubDown
downdetector.com/status/gith…

neonprimetime retweeted

Github is reportedly down for hundreds of users right now. Are you one of them? #github #githubdown community.designtaxi.com/top…

neonprimetime retweeted

AWS Outage (US-EAST-1): Explained Simply
1️⃣ Started with a DNS issue - AWS services couldn’t talk to each other.
2️⃣ This broke DynamoDB, which many other services depend on.
3️⃣ EC2 launches & Lambda jobs started failing due to the chain effect.
4️⃣ AWS fixed the DNS issue, but some services are still catching up.
It’s a reminder of how one small issue can impact half the internet. ⚙️
Full read: health.aws.amazon.com/health…