

cipher security labs https://xitter.gq/t.co/IZByfO2Dr4
🇪🇺🇮🇱
Joined October 2016
- Tweets8.5K
- Following697
- Followers1.1K
- Likes4.2K




Polymarket users were drained again on October 29. Nothing public points to a smart contract bug. This was a client-side supply-chain attack through a third-party script.
The vector
A DebugBear Real User Monitoring (RUM) script, loaded on Polymarket's international site for page-performance metrics, carried wallet-draining code written specifically against Polymarket's frontend (Hudson Rock). The script was served from DebugBear's CDN, a host Polymarket's CSP allowed (WhoGetsMyData scan, cited by Hudson Rock). CSP trusts a hostname, not bytes: once the bytes behind that host changed, the payload ran with full page privilege inside authenticated sessions.
DebugBear, 18:00 UTC: "We're impacted by an ongoing security incident. If you use our RUM product, please remove the embed code from your website." Polymarket referred only to a "3rd party provider". DebugBear was named by a source to CNBC and in Polymarket's build metadata.
Payload (Hudson Rock capture)
cdn.debugbear[.]com/C7xcKKrjUnXK.js
15,187 bytes
SHA-256: 0755e767504d8103f6c27b9e765a1026507a17c04513242adb503df7777879e5
Hard-coded fallback recipient: 0x3F99139F1C5854bb628c2e576Aaf638e99dFfc18 (remote config could select another)
Stage 1: session reuse, not key theft
The script reads polymarket.auth.params, polymarket.auth.proxyWallet and poly_clob_api_key_map from localStorage and branches on eoa vs magic wallets. No seed phrase is needed. It reuses the authority already living in the page.
Stage 2: hijack the app, not the RPC
It walks React internals (component props and hook state) for an object exposing postOrder and createOrder or createMarketOrder, then attempts to drive it together with its signer. This is purpose-built tooling against Polymarket's client, not a generic drainer.
Stage 3: liquidate, then sweep
Per Hudson Rock's static analysis: SELL orders at increasingly aggressive prices, or an ERC-1155 batch transfer of position tokens. Then EIP-712 DepositWallet batches, signed through the page's own signer and submitted to Polymarket's relayer. Then swaps.
On-chain
The payout address received USDC.e to POL swaps via Relay (Arkham, per Decrypt) and peaked at about 28.64M POL (roughly $2.6M) around 18:10 UTC. Between 18:28 and 18:38 UTC it moved about 28.6M POL out in three transfers. Signed DepositWallet batches are a normal Polymarket flow, so on-chain the drains can look user-authorized. The $2.6M figure is the wallet's peak balance, not a confirmed total loss.
Timeline, Oct 29 (UTC)
17:10 first POL reaches the payout address
17:59 Polymarket build removing DebugBear RUM (#15337)
18:00 DebugBear discloses
18:05 cancel-only mode, relayer paused
18:33 Polymarket: provider compromised, law enforcement contacted, impacted users "will be made whole"
19:00 trading fully back online
Per CNBC, the US platform was not compromised and the case went to UK law enforcement. Open questions: victim count, exposure window, and how DebugBear itself was breached.
Pattern
June: same class, a compromised vendor script, about $3M from fewer than 15 accounts. May: a different layer, a compromised key on an internal top-up wallet, about $700k.
The contracts were not the way in. The browser was.
1
1
267
By Cipher Security Labs @UrielKosayev

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability

1
1
331
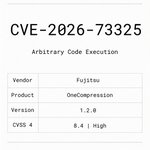
New vulnerability disclosure from Cipher Security Labs.
CVE-2026-73325 affects Fujitsu OneCompression 1.2.0 and can lead to arbitrary code execution.
Severity: CVSS 4.0 - 8.4 High
Looking for security research that goes beyond standard testing? We help organizations uncover high-impact vulnerabilities before attackers do.
Track our CVEs: ciphersecuritylabs.com/CVE-T…

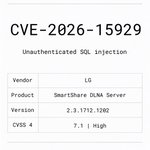
New CVE from Cipher Security Labs: CVE-2026-15929, an unauthenticated SQL injection in LG SmartShare DLNA Server v2.3.1712.1202. CVSS v4.0: 7.1 (High).
Track our CVEs: ciphersecuritylabs.com/CVE-T…

Respect @MaorShlomo

TLDR: I’ve started a small fund from my Base44 money that’s focused on cancer research and breakthrough therapies.
I’ve invested in 7 incredible companies in the past 4 months and plan to do more as my liquidity allows. Listing my investment thesis below
I welcome anyone like me who has been blessed financially to join me and find ways to finally manage or even end this disease.
Longer -
I honestly believe cancer is humanity's worst enemy.
~40% will be diagnosed with it, and out of which a ~third won’t make it. And numbers are currently not getting dramatically better.
For many it might sound like a statistic
But for some of us who have been there ourselves or had to go through it with a person we love, it’s one of the worst things you can imagine.
I had to go through it with my mom - who passed away 4 months ago and whom I miss and think about every single day since.
This field needs a dramatic push.
The current wave of technology and AI is doing a lot of good in the world,
But cancer therapy is one of those things that are not moving nearly fast enough.
And there’s no good reason for that - AI is creating so much opportunity right now.
Here's my thesis on how things will play out:
For drug development, the bottleneck will shift to
1. Manufacturing
2. Real world testing
"In silico" is going to accelerate incredibly fast. AI is identifying new target proteins and designing new molecules, drastically shortening timelines.
AI will create an abundance / inflation of ideas. It will help design molecules faster than anything historically possible.
This is already happening.
Play with Claude Science or Codex and you'll be surprised at how far you can get with just a few prompts.
We need a better way to *manufacture and test* the 1000s of ideas coming from AI models spitting out potential drug candidates
1. Manufacturing: i.e. how fast can we synthesize a potential drug
Not too far into the future, companies with manufacturing excellence will win over companies with the smartest scientists.
Being able to synthesize a drug candidate fast - together with efficient methods to test efficacy (more on that below), basically means you get more shots at a target hence more chances at succeeding.
This is the same exact lesson the software industry learned about the importance of fast iterations.
Companies like Starget Pharma are leveraging AI heavily to iterate on drug candidates + figured out in-house manufacturing in a way that lets them iterate on drugs almost as fast as if they were a software company iterating on features.
2. Real world testing: i.e. how fast can we get a call on a drug's efficacy.
We need better real-world indicators for drug efficacy than mouse / animal models.
The success rate of animal models -> human clinical trials is less than 8%.
Breaking down this bottleneck will change the entire industry.
Developing an oncology drug and taking it through all clinical trials usually cost >> $ 100m
Thus taking the wrong bet is devastating (but still, happens a lot).
Giving drug development companies the ability to better understand the efficacy and mechanisms of their drugs will change a lot. Esp in the age of abundant drug candidates.
Furthermore - and once those methods proved efficient - Joining forces with regulators to shorten (or even skip) some clinical trials altogether will cut years from the process and save many lives by bringing new drugs to market faster.
CuResponse is pioneering functional testing - taking real cancer biopsies and showing drug efficacy with very high precision. Can be used for precision oncology as well as testing new drugs.
Cellint is providing a fully automated cell-culture R&D platform for companies and researchers.
----
I’d love to see a future where there are “cloud services” for drug development companies.
A company should eventually be able to submit a drug candidate programmatically and receive:
1. The synthesized drug.
2. Testing across cells, tissues, organoids, and tumoroids.
3. Structured results showing what worked, what failed, and why.
4. A recommended next iteration derived from the biological reactions.
I’ve invested in all of the above companies and am searching for additional companies to bring this “cloud services for drug dev” vision to life.
----
Alongside it, I am also investing in direct therapeutic moonshots.
I invested in Baccine, which is developing a bacteria-based cancer immunotherapy platform and deserves an entire separate post.
I’m also a proud LP in Even One Ventures - @sytses ’s fund to fight cancer. Sid and Jacob Stern are an inspiration to me as I’m making my first steps in the field, and I bet their companies will make a massive impact.
And 3 other incredible companies focused on how therapies are delivered - where I’ll elaborate in future posts.
----
I’m still obviously spending most of my time on Base44. Which is a plus for the companies - as we’re able to support them with tools, software, AI agents, etc.
I’m looking for people to join me - invest side by side or help one of the companies.
I don’t have a name for the fund yet, nor an email or a website
I will get to it this weekend and will post it in the comments.
318
Redis CVE-2026-23479 is not just a Stream issue.
At Cipher Security Labs, we reconstructed the unblockClientOnKey() UAF and measured additional trigger surfaces.
Key finding: stream-only ACL hardening is incomplete.
Full research:
ciphersecuritylabs.com/resea…
New research from Cipher Security Labs.
WordPress Plugin Profile Builder <= 3.16.1
Unauthenticated Media Upload
We responsibly disclosed the issue to Cozmoslabs, and it was fixed in Profile Builder 3.16.2.
Write-up:
ciphersecuritylabs.com/resea…
PoC:
youtube.com/watch?v=fTGOfsUo…
1
135
idanmalihi.com/tracking-nort…
Cipher Security Labs researcher @Idan_Malihi published an excellent analysis of Kimsuky APT infrastructure.
Parsers are always worth testing.
We researched BBEdit’s language modules and found two DoS bugs: Java stack exhaustion + Lasso tokenizer infinite loop.
Fixed in BBEdit 16.0.
ciphersecuritylabs.com/resea…
Great insights from cipher security labs researcher @Idan_Malihi
ciphersecuritylabs.com

After conducting a Threat Hunting operation targeting infrastructure associated with the Brute Ratel C4 framework.
The research identified several active servers and domains that, according to the findings, were used in attack campaigns across different regions worldwide.
Shodan:
http.headers_hash:144518609 http.html_hash:1305614831
The identified infrastructure:
· 77.88.193[.]134
· 91.84.111[.]104
· 157.230.132[.]195
· 178.63.172[.]13
· 62.192.173[.]249
· 167.99.165[.]34
· 91.203.132[.]57
· 155.117.20[.]166
· 178.16.55[.]52
· 178.16.55[.]226
· 158.160.15[.]41
· 13.202.120[.]94
· 161.35.73[.]220
· 193.23.118[.]155
· 63.178.135[.]144
· 5.183.219[.]132
· 68.64.178[.]130
· 78.128.114[.]22
Associated domains observed during the hunt:
· phactory[.]art
· mail.ukeysign[.]com
· redteamer.co[.]in
· shopgolic[.]ru
· puffvape[.]ru
· yastatic-prx[.]ru
· businessanimation[.]online
· brute.bzh[.]ovh
· nocta-fans[.]com
· teams.microsoft-365[.]app
· artoriasnova[.]store
182
Just ran the access code from the Polymarket ad and… yep, it actually worked.
Got full access. Enjoy.
@Polymarket

1
199

Great talk by @MalFuzzer 👏🏻

Just uploaded my last talk about Red Team and supply chain attacks. Enjoy! 🔥💣
youtu.be/P2uQ__YXs4c

3
1

My Top Books to Learn Malware Analysis and Reverse Engineering by @fr0gger_ link.medium.com/tW33t26Kyob
My article “Five Steps to Addressing Supply Chain Vulnerabilities” is published! Thank you @Hakin9

We just published our newest issue - Car Hacking! Check it out and learn new vehicle hacking techniques, tools, exploitation and more! hakin9.org/product/car-hacki…
#hacking #automotive #automotivesecurity #cybersecurity #carhacking #automotivehacking #pentesting #infosec

1
4
Either of these endpoint solutions need to learn a lot about detections, it's better to humbly learn from each other to grow than disrespectfully go down like this with official statements. Bad move @cybereason

Well-designed #EDR platforms are supposed to help analysts focus on the things that matter most by eliminating false positives - the architecture of @SentinelOne’s sensor technology, however... cybr.ly/3bSxXxN #security #incidentresponse
