

Co-Founder & CTO @Centrifuge Labs, building the open protocol for onchain asset management. Co-author of the ERC-7540 tokenized vault standard.
Joined December 2009
- Tweets326
- Following373
- Followers1.4K
- Likes133




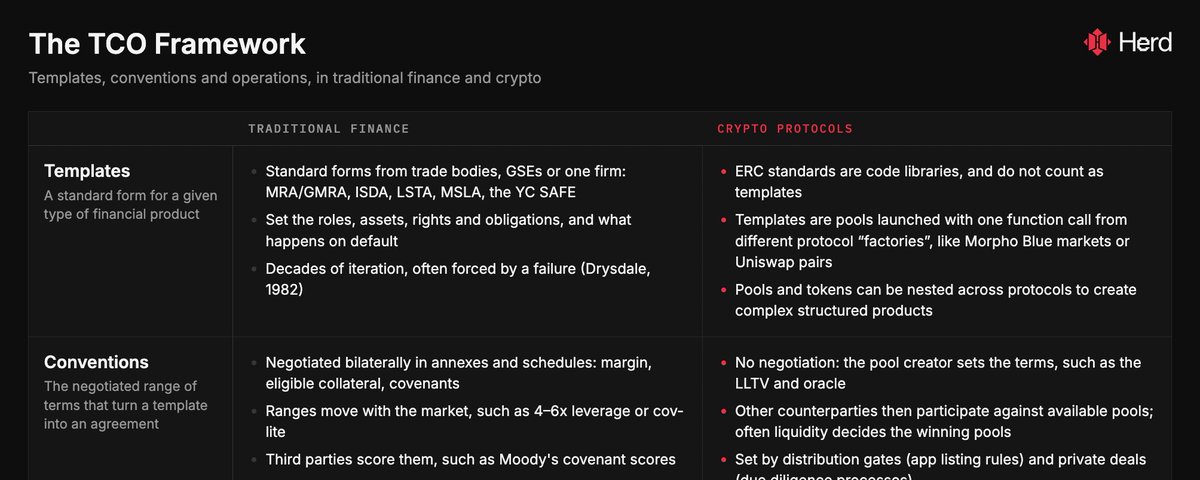
Centrifuge started almost 10 years ago with the vision of tokenizing individual assets, securitizing these and offering diversified products to investors. Bringing the entire lifecycle of credit products onchain.
This vision was too early then, but is quickly becoming reality now.
Excited to build with this.


Jeroen retweeted

Happy to share this one. I formally verified the Centrifuge core with @Certora Prover: 19 verification scenes, and every rule is backed by a mutation to prove the specs catch real bugs.
Thanks to the Centrifuge team for a great collaboration. Glad to see FV becoming part of their ongoing security process.

Audits try to find ways code can break.
Formal verification asks whether critical properties of the code can be proven to always hold.
For the first time, we've formally verified the Centrifuge core using @Certora Prover. The initial work covered 1,589 properties across accounting, holdings, share issuance, the Hub and Spoke, messaging and other core components.
It's another layer in a security process built around continuous review rather than a single pre-deployment checkpoint.

Lots of good discussion on this already, and it's an important one. The comment I'd zoom in on is where Paul puts every vault that deploys cross-chain into the discretionary bucket.
For most cross-chain vaults today that's fair. Bridging liquidity, updating NAV per chain, and reconciling accounting across chains all put more weight on the manager's judgment.
But that reliance comes from the architecture, not from being multi-chain. At Centrifuge a pool is one balance sheet deployed across many chains from a single point of control:
- The mandate sits in an Onchain Execution Policy that classifies every manager action, with timelocks and sentinels that can cancel a pending change, similar to Morpho Vaults. One policy covers every chain.
- Cross-chain messages are verified against several independent interop providers, so a pool depends on no single provider
- NAV and double-entry accounting are computed in one place rather than produced per chain and reconciled
That gets you to a vault that operates across many chains and is still noncustodial, with real investor protections.
Jeroen retweeted
love brian but ATPs are not an apples-to-apples comparison to vaults. while its good rage bait, it is just making everyone more confused
everything in defi comes down to "strategy" and "custody". a strategy is a managed set of allocations across contracts, and custody sits both above and below the strategy (how do you "hold" a position in the strategy, and how does the strategy "hold" positions across other contracts).
The primary ATP strategy today (an ETF) is safer than a variety of strategies run by vaults. My mental comparison of glider today is against my metamask or coinbase account, not against some steakhouse vault. When glider gets to openly creating and managing strategies that ATPs can allocated into, then we are getting closer to an apples comparison. I believe the complexity of contracts/oracles is unavoidable, you can abstract it with an API sure but it is still there and institutions will still want to audit down through every layer (they aren't going to just sign off on your api). It's not a problem you can just run away from.
I also know I tweet large token graphs often, but more contracts != more risk always. For example, centrifuge has like 30+ contracts just to manage bridging of an asset because they want fallbacks/gates/agreement across different bridges (chainlink, layerzero, and axelar). And if you want to allow different strategies, you have to segment what operations are allowed by what operators (this is the bulk of contracts for any protocol/vault). Privy wallets give glider full authorization to do anything they want on behalf of the user, but eventually that will have to become more segmented like a policied weiroll solution which a few other teams are close to launching (like makinax).
I'm seeing enough confusion on the timeline that it's probably worth me writing an article about the layers of strategy, custody, and operations in defi today.

We've been cooking up some vaults.

I've been deep in @centrifuge's new vault stack for a while now, and I'm more of a fan every day. It's the closest thing to a complete vault I've read. It has very modular architecture, I think every RWA protocol would want to build on it.
It runs one pool balance sheet with N share classes as claims on it, async requests with pluggable settlement policies, and a NAV with a double-entry ledger.
It'll be a real game changer in the space once it is launched.
Most vaults nowadays encode rules for allocations either through smart contracts or merkle trees.
What many miss is encoding rules for everything else. There is often one or more ops wallets that controls price, can change the rules (merkle tree root hash), mint tokens, etc. This is often scattered across many different smart contract entrypoints, making it hard to audit and secure.
Moreover, vault frameworks generally define a specific structure (allocation framework, specific set of roles and their capabilities, ...), limiting flexibility and what can be built on top.
We've been building a new approach with the Onchain Execution Policy, where:
- All sensitive actions go through a single entrypoint and single smart contract (the policy)
- The policy and any timelocked actions can be easily reviewed and audited by anyone
- Changing the rules (updating policy) has a significantly longer timelock
This increases flexibility (you can experiment with any approach, whether that is smart contracts or workflows encoded in merkle tree leaves), while enforcing the policy across the system.
And best of all, this will be fully multi-chain native: the policy will be enforced on the vault's hub chain, and any authorized timelocked actions will be sent cross-chain to all spokes.
A mandate is the set of objectives and constraints a manager operates within. It has historically been a document, and a document is not enforced where the action happens.
The manager's onchain permissions can be wider than the mandate they agreed to. A depositor cannot verify what the manager may do, and nothing stops an action that falls outside it.
The Onchain Execution Policy encodes the mandate, delays actions that carry material risk, and lets sentinels cancel them while they wait.
Discretion is what makes active management work, and it is also the thing a depositor has always had to take on trust. Issuance, pricing, allocation, and settlement already run in contracts. Now the bounds on the manager do too, and a depositor can read them before putting money in.

Jeroen retweeted

Once Centrifuge's new vault stack is public, I'll drop a banger on Centrifuge's stack vs Veda Lab's BoringVault, compared on every parameter of the Complete Vault.
Complete Vault's parameters: xitter.cf/0xjayeshyadav/status/2…
Drafting it now. Stay tuned.
I've had the chance to start working with the @centrifuge team on the next iteration of their vault design, rebuilding my CPPI vault on top of it to help pressure-test the approach. Grateful to @offerijns for the opportunity.
Without getting ahead of what's theirs to announce, the thing worth saying is that the direction lines up closely with where I argued vaults were heading in this piece: modular behavior around an immutable core, async liquidity, and cross-chain accounting treated as native.
Vaults are genuinely moving in the right direction.
We will announce Centrifuge v3.3 soon, but are already working on Centrifuge v3.4 in parallel. Teaser on what's to come below.
Moving fast to bring tokenization and vaults to everyone.
ERC-8161 is now finalised, enabling secondary markets for vault redemptions orders. Co-authored with @cainosullivan.
Excited to see how this will extend the composability of new vaults coming to market. At @centrifuge we certainly have some unique new use cases in the pipeline!
Asynchronous vaults solved a real problem. Assets that don't settle instantly, like tokenized funds with NAV cycles, couldn't fit the synchronous vault model.
But a pending deposit or redeem couldn't move. Once submitted, a request sat locked in the queue until fulfillment. For long-dated private credit, where redemption can take weeks or months, that meant a frozen position.
EIP-8161, co-authored by @offerijns, Co-Founder & CTO at Centrifuge Labs, is now finalized as an official Ethereum standard.
Pending requests can now transfer to another address. Markets can form around redemption requests still in the queue, letting holders exit before settlement and pulling long-dated assets like private credit deeper into DeFi.


Now: AAA CLOs backing USDe
Soon: new Ethena + Centrifuge products launched together

Ethena is partnering with @Centrifuge as a strategic tokenization partner, with the integration of JAAA, Janus Henderson's AAA CLO strategy, into USDe's backing.
This is the first non-T-Bill RWA collateral in USDe's backing, approved by the Ethena Risk Committee following independent due diligence.
Every RWA is evaluated against four strict criteria: liquidity, credit quality, drawdown profile, and pricing transparency.
AAA RWA returns are driven by factors independent of crypto markets. Diversifying USDe's backing into these assets strengthens its resilience across market cycles.

Jeroen retweeted
Out of 8,100+ proposed ERCs, @OpenZeppelin has only implemented a tiny handful of token standards:
ERC-20, ERC-721, ERC-1155, ERC-4626, ERC-6909
ERC-7540 is joining that list: the async vault standard is now part of the toolkit most of DeFi runs on.

Tokenized treasuries, private credit, and regulated funds often settle over days, a timeline synchronous onchain vaults weren't designed for.
We've merged an implementation of ERC-7540 with support from @tokenizedvault members @centrifuge and @superformxyz to solve this.


