

Developer #PHP #Laravel #WordPress #JS #React Dev on https://xitter.gq/t.co/9m2UCbzSZC Hobbie: https://xitter.gq/t.co/UPJuygK3uh 🥷👨💻
Salta, Argentina
Joined December 2017
- Tweets771
- Following707
- Followers58
- Likes2.9K





Palinejs 🇦🇷 retweeted

‼️ #phpAfterShell EXPLAINED: A critical PHP flaw (CVSS 9.2) could let attackers turn corrupted session files into remote code execution.
The October #PHP2Shell patches didn't fix the underlying issue.
How does the attack work, who's affected, and what's the fix?
Learn here → thehackernews.com/2026/11/ph…


Palinejs 🇦🇷 retweeted

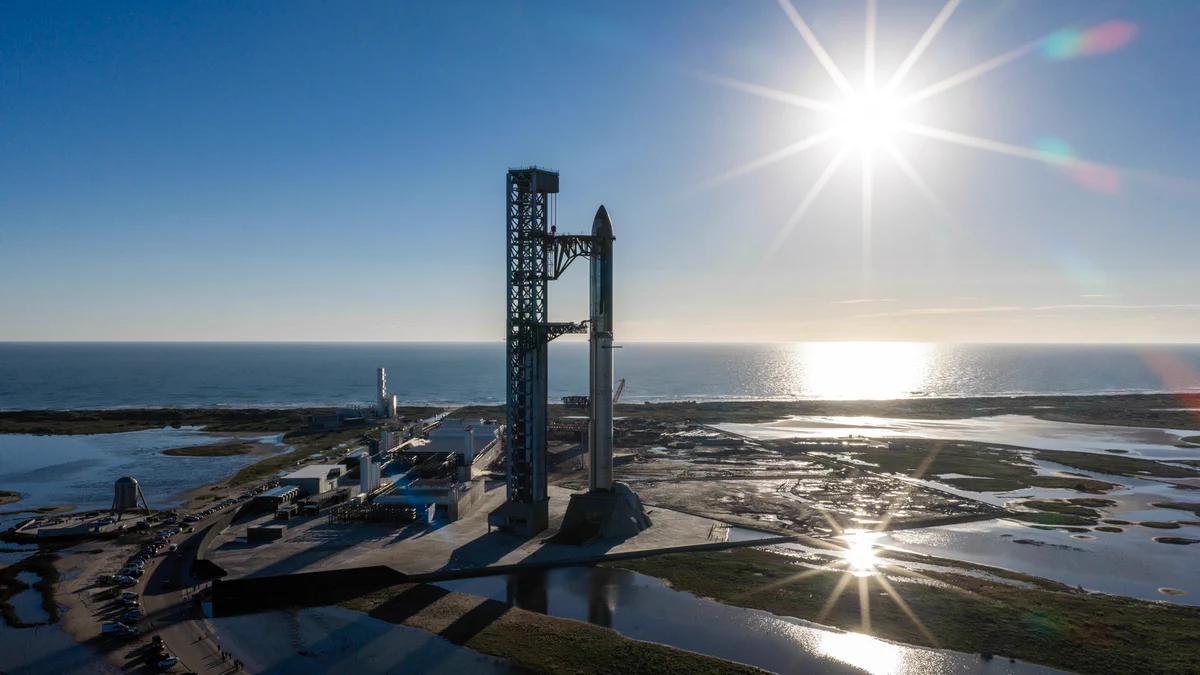
SPACEX HAS JUST CAUGHT STARSHIP!
This is the first-ever catch of an orbital-class upper stage spacecraft that has gone to orbit, survived reentry, and returned for recovery by the tower’s chopsticks.
CONGRATS @SpaceX!!! 🚀🚀



Palinejs 🇦🇷 retweeted

REGRESO DEL BOOSTER EN EL MAR CERCA DE STARBASE @FronteraSpacial
Palinejs 🇦🇷 retweeted
Live webcast of Starship's 15th flight test starts now → xitter.gq/i/broadcasts/2brajgZlO…
Palinejs 🇦🇷 retweeted

Hermes Whiteboard: an agentic whiteboard powered by @NousResearch Hermes Agent.
Say what you're planning and Hermes lays it out as a route. Then run the route: agents work every stop, attach results with sources, and hand you a brief.
Hermes suggests. You decide.


Palinejs 🇦🇷 retweeted

🚨 Fallo crítico en el kernel de Linux: se puede atacar por red, sin login y sin necesidad de ninguna acción por parte del usuario.
CVE-2026-98432
➡️ CVSS 9.8 (crítico)
➡️ Afecta a la gestión de conexiones TCP/IPv4, el código que atiende cualquier conexión a tu servidor.
➡️ Ubuntu marca vulnerables desde la 16.04 hasta la 26.10, también los kernels de AWS, Azure, Google Cloud y Oracle.
➡️ La corrección todavía está «en preparación» en casi todas.
Si tienes un servidor o un VPS con Linux, sigue los avisos de tu distribución y actualiza el kernel (y reinicia) en cuanto salga el parche.
ubuntu.com/security/CVE-2026…

Palinejs 🇦🇷 retweeted

PHP Remote Code Execution (CVE-2026-109618 & CVE-2026-109619)
Information about two new remote code execution (RCE) vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS v3.1 10 / 10), has leaked ahead of their coordinated disclosure, and security firm Watchtowr Labs confirmed that the flaws are real. Both vulnerabilities are due to be disclosed on Thursday, October 22, alongside patches. Until those advisories land, no fix is available, which leaves the flaws as zero-days in PHP installations everywhere.There is currently a scheduled release of an advisement and possible patch on Wednesday, October 21 2026 at 14:00 UTC.
Below is a video of a researcher, maybe the original researcher, showcasing the exploits.
#CTI #BlueTeam #ThreatIntel #CVE-2026-109618 #CVE-2026-109619
Palinejs 🇦🇷 retweeted

Orca’s Chat UI now preserves image positions in your message, just like terminal agents.
Many of our users switch between Chat UI and terminal view all the time.
We want both to perform equally well: same first-party agent harness underneath, same context going in.
Palinejs 🇦🇷 retweeted
We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate

Palinejs 🇦🇷 retweeted

Oh-My-Hermes 3.0.2 Released! SkillEx & FenceGuard
OMH: github.com/rlaope/oh-my-herm…
Oh-My-Hermes turns Hermes Agent into a team: ready-made skills, a router that picks the right one for every message, long-term memory, and sandboxed parallel coding agents across GPT, Claude, DeepSeek, Kimi and GLM.
SkillEx: skills that work more carefully
- Quoting is safe. Pasting a message that mentions a workflow no longer starts that workflow.
- Plans point out what is still untested before any code is written.
- Debugging stops after three failed fixes and looks at the bigger design instead of guessing again.
- Long-running loops agree on a clear finish line and the files they must not touch before they start.
- A new test has to catch a real bug before it counts.
- Small in-scope decisions are made and written down without stopping to ask you, and review rounds are capped.
- "Yes" means what you said yes to. Agreeing to an idea doesn't approve the whole plan.
- Debugging a past session is read-only.
- Backend work keeps one source of truth for each API contract.
FenceGuard: parallel agents stay in their sandbox
- Parallel coding agents never run outside their sandbox unless you allow it.
- Inside the sandbox they get no credentials and no network.
- An agent can't plant settings that later run on your machine.
- A run that never started is reported as a failure, not a success.
- Codex now runs inside the macOS sandbox.
MemoryEx, continued
- Memories are saved as facts, not as orders. "You must…" style notes are rejected and rewritten as observations.
- Vague dates like "two weeks ago" or "last Monday" are flagged instead of saved as-is.
- Memory search now handles French accents.
Also in 3.0.2
- Several open terminals share work instead of repeating it, so the status bar uses less CPU.
- Model setup works on machines with custom providers.
#hermes #ohmyhermes
Palinejs 🇦🇷 retweeted

OPENARG ULTIMA ACTUALIZACION
Hoy lanzamos el MCP de OpenArg. Hace unos meses lanzamos openarg.org que es la base de datos abiertos no-estatal más grande de LATAM.
Hasta acá nuestra IA en Openarg cuando le preguntabas al chat de IA por datos de Argentina, muchas veces te contestaba de memoria, con números viejos o directamente inventados. Con esto le enchufás directo los datos oficiales a tu propia IA: INDEC, BCRA, ministerios, provincias. Más de 33.000 datasets de todos los portales de datos abiertos del país.
Conectarlo es muy fácil. Pasale este link mcp.openarg.org a tu chat de ia y pedile que te conecte. Te va a guiar paso a paso. Se configura solo.
Por ahora anda en Claude Code, Codex, Claude Desktop, Cursor y VS Code.
Es gratis y abierto. Lo armamos a pulmón.
Sus comentarios nos ayudan a mejorar las herramientas cada día
