

learning, breaking🔁 | bug bounty hunter in my free time
void
Joined March 2010
- Tweets33.1K
- Following1.6K
- Followers2.3K
- Likes2.5K





Pinned Tweet
I'm going to explain how I found two OS command injection vulnerabilities a few days ago.
The vulnerabilities were quite easy to exploit once the injection points were identified.


Some PDFs that were not mine ended up in my account.
A short writeup from a bug bounty finding I got rewarded for this year.
saurinn.github.io/blog/every…


People that talk like this either have tested their stuff in a vm using wep or are watching too many Hollywood movies.
I mean I know there are some holes in modern protocols but hacking a wifi net externally without phishing it's hard

wifi hacking shouldn’t be this vulnerable in this era, aircrack, wireshark, kismet are sitting right there in kali linux bypassing with free will
251
Everyone serious about bb hunting and even beginners, this talk is A MUST!
This quoted post is unavailable.
1
296
manuel valdez⛩️ retweeted

Many of the CVEs you see coming out these days are actually not very weaponizable against real production systems, for one reason or another
Example: Anthropic’s recently reported Linux network RCE, which takes almost an hour to run, causes a kernel panic on any system that has even the default level Linux Firewall, in our testing
Often, the reason why you have even of these these bugs is because firms put them in the throwaway conference-talk category
Important to keep this in mind
manuel valdez⛩️ retweeted
good morning slop enjoyers, ready to post non-functional php2shell exploits and good morning everyone who tries to steal the spotlight of those who deserve the credit


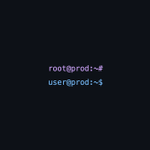
I pressed a test button and got two shells: ~#, ~$.
The connectivity check was handing my input to curl inside a shell, and so was a second feature. One was graded Exceptional at got a max payout for it,
via @intigriti.


manuel valdez⛩️ retweeted

Do you know that SSRF might cause local file/cache download and can harm as much as arbitrary write/RCE just from one URL? Making this research just now. Can't wait to share.

As a hacker, I understand perfectly well how difficult this path is. And I’ve almost always given people a chance to improve. Sometimes I even offered advice on their reports as a program manager. It was very rare for me to mark a report as "N/A" for a researcher. And it was certainly almost never the case that I, as program manager, marked a report as spam. But times are changing.
Right now, the level of audacity shown by some "researchers" is simply staggering. Not only have some "researchers" stopped looking for issues and writing reports, but they’ve also stopped answering questions. Even the answer to the question is just polished, generated MD text.
Because of these “heroes” who rely on AI and churn out useless MD reports, real researchers are running into problems. The level of bias is increasing.

3
722
This should've been a crit, if the risk is too big to prove further impact then pay the max, what a shitty move by the PM

Found an auth issue that exposed PII, and while reviewing the JS, I also discovered a destructive PUT method that could have overwritten the database.
I asked for a go-ahead rather than risking production data. They said no—and awarded a bonus for handling it responsibly. 🫡

1
2
394
