



Made a better Wrapper for Mimikatz with delayed execution
github.com/mobdk/WinTimer


Humm… don’t trust what your vendor says, remember to hardening your endpoint, this running Mimikatz
github.com/mobdk/CoreClass

Execute shellcode with syscalls and not using any native API calls like NtProtectVirtuelMemory, the compiled version has Mimikatz embedded github.com/mobdk/Upsilon

This is a new technique to dump user hash from LSASS, no call to API MiniDumpWriteDump or dll proxy stuff, very simple, try process hacker and dump the cloned process LSASS and run it against Mimikatz ! github.com/mobdk/CloneProces…


Embed binary payload in .bat and execute tasks.dll from C:\Windows\System32\Tasks. venus.bat contains tasks.dll in binary in the beginning of venus.bat
Still undetected on VT.


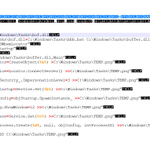
Embed binary in .bat file and bypass AVs, make sure CRLF is inserted, as showned in image.
This example execute reverse shell.
Take your payload.dll (csharp) payload, remove MZ from beginnng of file.
copy /B payload.dll+yourscript.bat bbb.bat
run bbb.bat

What to buy, budget $7500, I want the best moon telescope, also tracking and camera mount, any suggestions?
#moon #telescope #astronomy

