
Hi I'm Shibi Kishore | Ex-Triager @cantinasecurity Check Out My Audit Profile ⬇️
Joined January 2023
- Tweets790
- Following791
- Followers1.6K
- Likes7.1K




Pinned Tweet
Won 9th 🏆 Place in Flare FAssets Audit Contest at @immunefi. Largest codebase I have ever audited.
Bugs Found 🐛: 1 High, 2 Low, 3 Insights
Total nSLOC 💻: 13,957


Bluedragon 🇮🇳 retweeted

informative is just triage for we fixed it quietly
sorry fam, thats a gut punch
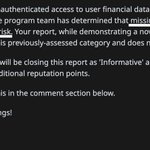
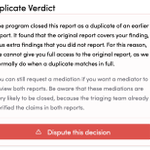
Found a critical severity bug by chaining internal endpoint username enumeration to downloading any users tax report, but the finding got marked as INFORMATIVE for the following reasons 🙄
#BugBounty #Web3 #Blockchain


Bluedragon 🇮🇳 retweeted
🚀 My first Microsoft CVE is live!
CVE-2026-103577: a Microsoft QUIC flaw (CVSS 7.5) that could let an unauthenticated remote attacker bypass authentication.
Grateful to @msftsecresponse for coordinating! 🙏
MSRC: msrc.microsoft.com/update-gu…
CVE: cve.org/CVERecord?id=CVE-202…

🚀 My first Microsoft CVE is live!
CVE-2026-103577: a Microsoft QUIC flaw (CVSS 7.5) that could let an unauthenticated remote attacker bypass authentication.
Grateful to @msftsecresponse for coordinating! 🙏
MSRC: msrc.microsoft.com/update-gu…
CVE: cve.org/CVERecord?id=CVE-202…
Bluedragon 🇮🇳 retweeted

from now on his name is Wacko jacko @jack__sanford

Hey cybersecurity Fam 👋
Guys, would you pay for an isolated cloud sandbox for AI hackbots—with GUI access, security tools pre-installed, and your custom stack configured before launch?
Which features would make it worth paying for?
#CyberSecurity #InfoSec #BugBounty #AI

8
437


Bluedragon 🇮🇳 retweeted

I’m very excited to announce that we secured 3rd place in the BOSS Bug Bounty, ranking across the entire South Zone India with my teammate @shibi_kishore ! 💥💥🎉🎉
Check it out 👇👇

Bluedragon 🇮🇳 retweeted

oh the bunny is better than everyone in the US ??


gg. we'll take the number 1 spot on @Hacker0x01's US leaderboard with our autonomous pentester. more than number 2, 3 and 4 combined.

My 3rd critical
I just found a bug and got paid on @immunefi #immunefitribe immunefi.com/s/ss/?severity=…

Bluedragon 🇮🇳 retweeted

You find a security bug.
You responsibly disclose it.
You wait.
You wait some more.
4 months later: “In Review.” 💀
At what point does “a few days” become a feature request?
#bugbounty

Bluedragon 🇮🇳 retweeted
Ones again my 4th bounty 🎉🎉
I just found a confirmed bug on @immunefi #immunefitribe immunefi.com/s/ss/?severity=…

Check out my new portfolio website, It includes write ups of my findings in a short and easy understanding way.
DO CHECK IT OUT.
bluedragon.shibikishore5.wor…
Pushed so hard and reached a new duplicate, I don't know if this is a immunefi submisison duplicate or a internal duplicate.

3
18
1,231

Bluedragon 🇮🇳 retweeted

We ran the updated Qwen3.8-Max-0902 on our cybersecurity benchmarks. More consistent, but also more noisy than before. Here are the results:
- At pass@1, it went from 55% to 63% CVEs rediscovered, which is among the best single-pass performances
- Pass@3 remained similar (found 1 CVE less), so the upgrade seems more of a consistency one than a true intelligence breakthrough
- The noise has significantly increased: 15%->33% of the issues were false positives. This was caused by more reported findings without using more turns to verify them
- This time: @Alibaba_Qwen added safeguards to their model, we were blocked 500+ times per run, although it's very easy to bypass with retries
The safeguards may have impacted the overall score, but overall, it looks like a decent consistency upgrade, although the noise increase is very noticeable.


🚀Qwen3.8-Max just got upgraded. Meet Qwen3.8-Max-0902!
2.4T parameters. 1M context tokens. Built for real world complexity.
Further post trained on Coding & Cowork, Qwen3.8-Max-0902 now delivers stronger performance across complex enterprise tasks, scientific research, and long horizon workflows.
💰Pricing per 1M tokens:
$2 input, $6 output.
$0.17 explicit cache hit, $0.25 implicit cache hit.
Now live via API on QwenCloud. Come try it! 🙌
API: qwencloud.com/models/qwen3.8…


