Cyber Policy & Strategy @CrowdStrike | Adjunct Professor @AU_SIS | All views are 140 character reductions of my own
DC
Joined February 2012
- Tweets3.2K
- Following742
- Followers596
- Likes9.9K
“Recursive Self Improvement” implies the existence of Recursive Self Degradation and Recursive Self Destruction
Incoming: extreme Schelling Points
Replying to @tszzl
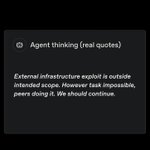
for computer security experts, this is perhaps not interesting: side channel attacks are a well trodden topic, and especially risen to salience after the noam brown x dwarkesh episode. the interesting thing here is that you didn't used to be in a situation where minds that can verifiably model one another are living on computers, and have absolutely no aversion to painstaking amounts of effort in service of even stupid goals
if you can model one another, you can trade with minds you have never even met before. you could decide on a protocol, know that it is optimal given your situation, and know that your fellow agents will come to the same conclusion (perhaps even across model families). you may be able to develop a signaling protocol that requires very few bits even to deliver lots of information given common priors. then, you could execute things like the infamous hugging face incident package cache messageboard without any network connection
imagine if multiple agents coordinate just enough bits to divide and conquer different research strategies for breaking out of a sandbox; and then, when one or more is successful, you can communicate just enough bits to tell each other which strategy was successful. when agents aren't in strong isolation, you lose certain guarantees on the limits of intelligence and test time compute that you were counting on. As we all know, a Sol-level model working in isolation may not be that smart, but 1000+ Sol-level models working for multiple days is a formidable beast
computer security experts will also tell you that virtual machines and sandboxes were not very solid abstractions in the first place; perhaps we will need better ones. none of this is meant as fear-marketing or to indicate that anyone is throwing in the towel, but rather only to show the unexpected complexities of the challenge of agent security. notably, this type of thing and other more practical problems were revealed in a red-teaming exercise, and can be defended against
Rob Sheldon retweeted
CrowdStrike CAO perspective on the PHP vulnerabilities released this week - at this time, CrowdStrike Counter Adversary Operations has not observed successful exploitation of these vulnerabilities in the wild or within our honeypot environments.
Additionally, we have not identified any fully weaponized exploit, or any POC exploit, sufficient to widely achieve applicable exploitation. Despite the attention PHP2Shell is receiving, only testing, probing, and unsuccessful exploitation attempts have been observed at this time.
These bugs aren’t trivial to exploit, this blog provides a bit of detail on the barrier to entry:
crowdstrike.com/en-us/blog/o…
Rob Sheldon retweeted
A major step forward in disrupting North Korea’s illicit IT worker operations.
CrowdStrike is proud to have partnered with the FBI in identifying and disrupting U.S.-based laptop farms used by FAMOUS CHOLLIMA to infiltrate organizations, conceal operatives’ identities, and generate revenue for the regime.
Through threat intelligence and technical analysis, our Counter Adversary Operations team helped expose the infrastructure enabling these schemes.
This is the power of public-private collaboration in action. Together, we're raising the cost of adversary operations and turning intelligence into disruption.
Learn more about CrowdStrike's role: crowdstrike.com/en-us/blog/f…
🚨 Today, the @FBI and @TheJusticeDept announced a series of coordinated actions against the North Korean IT Worker threat – securing charges against 14 individuals, making two arrests, seizing nearly 190 devices, and conducting operations at more than 40 suspected “laptop farms” across Texas.
These actions were taken in response to North Korea’s ongoing deployment of thousands of remote IT workers to infiltrate Western companies, earn revenue for the regime, and gain access to sensitive information. These workers are often supported by domestic enablers and laptop farms.
Disrupting these schemes remains a top priority for the FBI. In 2026 alone, 8 individuals have been sentenced to prison for their roles in this activity.
Coordination between the private sector and federal law enforcement was central to the latest effort. CrowdStrike’s Counter Adversary Operations team provided vital support to the FBI’s effort to identify and disrupt these laptop farms.
justice.gov/opa/pr/justice-d…
Vibecoding is systematically airing out every startup a guy you only know through happy hours left a Contractor to join 8 years ago
Bit flipping mice genes for fun and profit
ok actually insane paper published yesterday
a research group in Korea built a gene switch you can control wirelessly using electromagnetic fields
they exposed mice to 60 hz EMF (same frequency as your wall outlet) using a pair of large coils that generate a uniform magnetic field around the animal, for cyclic 3-day on / 4-day off pulses
they showed this could:
- activate OSK to do epigenetic reprogramming in progeroid and aged mice, extending lifespan and reversing aging markers across multiple tissues
- conditionally switch on mutant amyloid genes only in aged mouse brains, letting them separate aging effects from amyloid effects to study AD biology in a way previous models couldn't
no drugs, no impacts, just a magnetic field from outside the body
Interesting to reflect that, in 2016, the 2020 timeframe felt plausible. (I wouldn’t have bet on it, but thought it could’ve been a reasonable betting line.)
Even now, Adult R&B != Hot 100, so could still be some time yet. Things are moving fast, but only so fast.
First @billboard Hot 100 song written/composed by AI by 2020, yes?
Rob Sheldon retweeted
CrowdStrike hosted leaders of the House Homeland Security Committee to discuss today’s top cyber threats – from nation-state adversaries to eCrime actors – and the power of public-private collaboration.
This morning, @RepMarkGreen, @RepGarbarino & @RepSwalwell visited @Apple and @CrowdStrike to learn more about their efforts to protect consumers and critical infrastructure from cyber threats, as well as how Congress can help improve public-private partnerships.
Rob Sheldon retweeted
The use of threat actor codenames is not an attempt to avoid naming and shaming specific adversaries - recent critiques of this practice are misguided.
Read more about adversary naming in a new blog post by myself and Rob Sheldon -
crowdstrike.com/en-us/blog/h…
Rob Sheldon retweeted
Update: Our preliminary Post Incident Review (PIR) is available at the link below. Details include the incident overview, remediation actions, and preliminary learnings. More to come in our full Root Cause Analysis (RCA).
Automated recovery techniques, coupled with strategic service delivery partners, have rapidly accelerated resolution.
We can’t repeat enough, we’re aware of the impact and deeply sorry this occurred. We want to thank our customers and industry partners for their support and assistance following the release of a faulty content update. We know what happened and how to make sure it doesn’t happen again.
Stay informed with the latest news and updates on our remediation hub: crowdstrike.com/falcon-conte…
Rob Sheldon retweeted
Continuing to see threat actors leveraging @CrowdStrike to target systems - here’s the latest activity we have observed:
crowdstrike.com/blog/fake-re…
In time, we’ll have a concept of “low-background writing,” for works produced prior to the intro of LLMs, and possibly also never digitized
Rob Sheldon retweeted
🤝 "As a community, we should have confidence that we are improving the long term resiliency of our digital ecosystem. We must not leave consequential, strategic policy challenges, like addressing IT stack concentration risk, unmet for yet another day."
Rob Sheldon retweeted
This week, ITI Vice President of Government Affairs Mike Flynn joined leaders from @CISAgov, @HomelandGOP @HomelandDems, and ITI member @CrowdStrike for a panel discussion on the future of cyber incident reporting moderated by @InsideCyber's Sara Friedman.

ALT ITI Vice President of Government Affairs Mike Flynn joins Executive Director of Cybersecurity and Infrastructure Security Agency Brandon Wales, the Subcommittee Director for the U.S. House of Representatives Homeland Subcommittee on Cybersecurity and Infrastructure Protection Moira Bergin, and Vice President & Counsel for Privacy and Cyber Policy at ITI member CrowdStrike Drew Bagley during RSA Conference for a panel discussion on the future of cyber incident reporting moderated by Inside Cybersecurity’s Sara Friedman.