
Threat Research at WIZ
Israel
Joined March 2016
- Tweets130
- Following224
- Followers171
- Likes1K



This seems to have serious repercussions on containers running without sandboxing. We knew container is not a great security boundary but this is another level.

🔥 A thousand fewer paths to root
My @OpenAI colleague @ky1ebot built an autonomous vulnerability discovery, exploitation, and patching pipeline.
In one run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation (LPE) vulnerabilities in Linux at an API cost of $1.2 million.
Each LPE lets an unprivileged local user gain root access.
To the best of our knowledge, the agents in this pipeline discovered and used at least 10 novel Linux exploitation techniques.
We wrote a blog about:
- How the pipeline works
- The cost of each stage
- Our findings and learnings
openai.com/index/a-thousand-…
Shay Berkovich retweeted

It's been such a tough October for AI Developer Platforms ... that two more disclosed incidents while we were writing up this blog: wiz.io/blog/black-october-fo…
Check it out for details on what we're seeing attacks do with compromised credentials from the recent incidents

Kudos to @github on moving the needle, but this vulnerability class isn't gone.
This quoted post is unavailable.
Isn't it silly to call every RCE vuln "smt2shell"? That's the definition of RCE pretty much - giving shell.
Shay Berkovich retweeted
🫂"hugs from TeamPCP."
We're now 47 days and three rounds deep into the Checkmarx incident -- and this time TeamPCP left a message for victims in `~/hugs_from_teamPCP.txt`
Things appear mitigated, but waiting to see if rotation was a bit more atomic this time 🤞

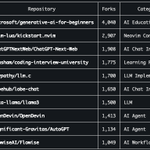
List of most popular/active public repos on GitHub - April edition:
- @openclaw hype is over?
- @Microsoft GenAI tutorials are back to the first place
- April normalized to AI models and established learning
resources

Shay Berkovich retweeted

Preliminary exploit detections for Copy Fail (CVE-2026-31431) based on our tests (these work best in combination):
1. "NET: Registered PF_ALG protocol family" in kern.log & syslog
2. curl for "copy[.]fail/exp" (if attacker is lazy)
3. su record without invoking user in auth.log
Did somebody manage to use it as a container escape from a non-priv container?

Patch your Linux boxes!
Copy.Fail is a trivially exploitable logic bug in Linux, reachable on all major distros released in the last 9 years. A small, portable python script gets root on all platforms.
Found by the teams at @theori_io and @xint_official
More details below
xint.io/blog/copy-fail-linux…

Shay Berkovich retweeted
Fork commits keep showing up in supply chain attacks (tj-actions, reviewdog, TeamPCP).
But, I keep seeing incorrect explanations in incident threads/blogs
So I built a microsite to cut through the confusion
🔗in🧵

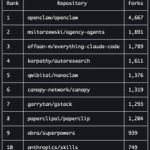
Monthly list of most popular/active public repos on GitHub:
- @openclaw keeps the first place (although its half pace comparing to February)
- Rise of the personal claude skills and harnesses over official anthropics/skills
- karpathy/autoresearch - fast-breaker

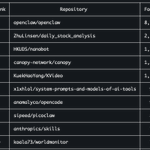
Turns out # of forks is a great metric of repo popularity. Here is the most popular/forked repos of Feb 2026. Of course, #OpenClaw is leading the pack:

Shay Berkovich retweeted

UPDATE: Shai-Hulud 2.0 has a long tail, and it may have led to $7M in crypto theft.
Earlier today, our update laid out how sha1-hulud may have caused the Trust Wallet incident.
Trust Wallet just announced the same conclusion 📷Read our analysis >> wiz.io/blog/snipping-the-lon…

With #shaihulud2 refuses to die with the long tale of infections (117 new compromised machines in the last 72 hours, most of them form @Cursor IDE), all @github has to do is disable the gho_ tokens of the super-spreaders (last 2 active spreaders are Cpreet and moh-abed).


Or extend their PAT revocation API to cover other token types: docs.github.com/en/rest/cred…

Shay Berkovich retweeted
🪱sharing more on sha1-hulud w/@sshaybbc
* 2 packages == ~60% of infections
* 400k unique secrets in truffleSecrets.jsons, only 2.5% verified, & the majority of those short lived JWTs for GitHub Actions!
* 3/4 of impacted workloads were CI/CD, 1/4 were users
🔗below

Second part of our research on secret leaks In AI.

🤖 65% of Forbes AI 50 companies leaked secrets on GitHub. @sshaybbc revealed how AI speed without security = leaks waiting to happen.
Full Wiz Research report 👉
wiz.io/blog/forbes-ai-50-lea…

Re- #Shai_Hulud attack - its disturbing to see the evolution of the attacker. Comparing to #s1ngularity attack, new elements added:
- Worm-able nature of the exploit
- Better automation of the secret scan
- Bundling of the secrets for exfiltration with tojson(secrets)
Shay Berkovich retweeted
More from me on s1ngularity, the Nx supply chain attack.
We @wiz_io took advantage of the break in attacker activity to break down:
* overall impact
* efficacy of the AI usage (not great!)
* TTPs and investigation breadcrumbs we've seen to date
* our work to notify victims
