

Be the company hackers skip. Stay protected, stay boring to hackers. Get vulnerability alerts and discuss security with the community: https://xitter.gq/t.co/HwfTWgXatL
Joined August 2025
- Tweets1.8K
- Following46
- Followers946
- Likes743



Pinned Tweet
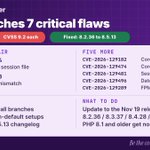
A session file that only half got written can end in remote code execution. That's phpAfterShell (CVE-2026-126714), one of seven flaws PHP rated critical in today's release.
Most of the rest are use-after-free bugs in core, sessions and the date extension, plus request smuggling in PHP-FPM. PHP says the criticals need a non-default config or an uncommon setup, so check how your sessions and FPM are wired.
Fixed builds: 8.2.36, 8.3.37, 8.4.28, 8.5.13. Nothing for 8.1 or older.
#PHP #AppSec #PatchTuesday

A file named .png can still end up in Ghostscript. That's the trick behind Upload2Shell.
CVE-2026-125396 is a use-after-free that lets a crafted document escape Ghostscript's -dSAFER sandbox and run commands as whatever process renders it. Researcher Paulos Yibelo shows an EPS disguised as a PNG reaching Ghostscript through Pillow. Thumbnails, previews, print jobs and email imports all count as entry points.
Ghostscript 10.08.0 fixes it. Most servers get it as a distro package, so check yours.
#Ghostscript #AppSec #FileUpload

1
1
43
Fixed package versions and the upload paths that can reach Ghostscript:
vulntracker.io/cves/CVE-2026…
9
Locked down SurrealDB's built-in functions with capabilities? Before 4.0.0, embedded JavaScript could walk right around that.
CVE-2026-134292: the surrealdb.functions bridge calls the internal dispatchers directly and skips the capability check SurrealQL applies. A user who's denied a function in a query can still call it from a JS script. Versions 1.0.0 up to 4.0.0 are affected.
The fix is 4.0.0. No workaround is published.
#SurrealDB #DatabaseSecurity #RustLang

1
69
Affected range, the fix, and why the scores disagree:
vulntracker.io/cves/CVE-2026…
13
The lowest-rated of WhatsApp's three new CVEs is the one that may have been used against people.
CVE-2026-23871 scores just 3.5, but a crafted Click to WhatsApp ad reply could reveal a target's IP address, and WhatsApp says it may have been used alongside spam messages. The other two, a SQL injection on Android and a Meta AI attestation flaw, show no sign of abuse.
Updating the app covers all three.
#WhatsApp #MobileSecurity #Privacy

1
94
All three CVEs with fixed versions for Android, iOS and Mac:
vulntracker.io/cves/CVE-2026…
21
CISA added four exploited flaws to KEV on Nov 20, here's what they hit and how fast you need to move: vulntracker.io/blog/cisa-kev…
#CISA #KEV #VulnManagement

51
Cisco fixed CVE-2026-76466 in Expressway a month ago. Now it's being exploited.
The flaw gives an unauthenticated attacker root on clustered Expressway-C and Expressway-E devices. F6 says attackers used it to break into a company's network after a public PoC came out. The fix is X15.5.20, and X14 users have to migrate to a fixed release.
Full write-up in the reply.
#Cisco #Expressway #ThreatIntel

1
111
How the attack unfolded, what to check in your logs, and who is affected. Read the rest here:
vulntracker.io/blog/cisco-ex…

57
21 capital ß characters. That's the input it takes to push Ruby's upcase one byte past its buffer.
CVE-2026-132825, nicknamed Ruby2Shell, sits in string case conversion for single-byte encodings like ISO-8859 and Windows-1252. UTF-8 strings aren't affected. The researchers say default Rails and classic Sinatra apps can reach it, and they plan to release their PoC in about a week.
Ruby 4.0.10, 3.4.13 and 3.3.14 fix it, along with six regex and string bugs in the same release.
#Ruby #RubyOnRails #AppSec

1
2
197
GitLab shipped 19.6.1, 19.5.8 and 19.4.10 for this one. We broke down who's affected and why it's rated Critical, 7.4 and Medium at the same time:
vulntracker.io/blog/cve-2026…

62
NLTK's last security fix left a side door open.
Version 3.10.3 locked down the JVM options passed through nltk. internals. java(), but the command list itself still accepted -jar and @ argfile tokens. If your app forwards user input into those calls, or into StanfordSegmenter's java_class, an attacker can run their own Java code.
Only 3.10.3 is affected and 3.10.4 closes it. Apps that never pass outside input to the Java wrappers aren't exposed. CVE-2026-128138.
#Python #NLTK #SupplyChainSecurity

1
1
110
Affected range, fix version and the earlier advisory this one bypasses:
vulntracker.io/cves/CVE-2026…
42
BlueField DPUs are supposed to sit between tenant VMs and the rest of the data center. CVE-2026-65094 weakens that line.
A user inside a VM can send a crafted message to the VIRTIO-Net service and trigger a write-what-where bug, with code execution as the possible outcome. NVIDIA scores it 9.0. No exploitation reported.
Patched VIRTIO-Net builds: GA 25.10.6, LTS25 25.10.2, LTS24 24.10.50.
#NVIDIA #BlueField #CloudSecurity

1
111
Affected VIRTIO-Net branches and fix versions, side by side:
vulntracker.io/cves/CVE-2026…
56
Second time in four months: vCenter's directory service has an auth bypass that needs nothing more than network access.
CVE-2026-123890 is rated 9.8 by Broadcom, came in through Mandiant, and has no workaround. Fixed builds are 9.1.1.0200, 9.0.2.0200, 8.0 U3m and VCF 5.2.5. On 7.0 you only get a fix through extended support.
#VMware #vCenter #Infosec

1
118
Fix builds for every vCenter branch and the Telco Cloud versions, all on one page:
vulntracker.io/cves/CVE-2026…
63
Update: these are out now. PHP 8.2.36, 8.3.37, 8.4.28 and 8.5.13 shipped today, and 8.6.0 also came out with the same fixes. Seven are rated critical, mostly in sessions and core memory handling.
PHP says most of the critical ones need a non-default config or an uncommon setup, so not every site is exposed. Still worth patching this week.
#PHP #CyberSecurity #WebSecurity

【事業者向け】19日23:00~23:30(日本時間)にPHPがセキュリティリリースを予定しております。前回とは異なり、本脆弱性の影響を受けるのは一部の環境に限定されるとのことです。以下リンクを確認のうえ、必要に応じて、修正パッチを適用できるよう準備をお願いいたします。
php.net/archive/2026.php#202…

1
207