

No longer posting to this account. You can follow my ramblings @juli3tt3cho
Local pub
Joined June 2009
- Tweets3.6K
- Following431
- Followers395
- Likes291




Pinned Tweet
No longer posting to this account. You can follow my ramblings @Juli3tt3cho
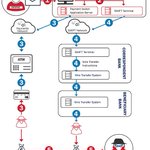
FASTCash 2.0: North Korea's BeagleBoyz Robbing Banks | CISA us-cert.cisa.gov/ncas/alerts… #cybercrime #cybersecurity

US Department of Justice (DoJ) Aims to Seize 280 Cryptocurrency Accounts Used by Hackers | Threatpost #cybercrime #cybersecurity threatpost.com/doj-aims-to-s…

Malicious Attachments Remain a Cybercriminal Threat Vector Favorite | Threatpost #cybersecurity threatpost.com/malicious-att…
Ransomware Has Gone Corporate—and Gotten More Cruel wired.com/story/ransomware-g… #cybersecurity #cybercrime

Medical Data Leaked on GitHub Due to Developer Errors | Threatpost #cybersecurity #securehumanOS threatpost.com/medical-data-…
Top exploits used by ransomware gangs are VPN bugs, but RDP still reigns supreme zdnet.com/article/top-exploi… #cybersecurity #cybercrime

Cyber is a business risk like any other | News | SCHILLINGS schillingspartners.com/news-… #cyberrisk #cybersecurity

Researchers Sound Alarm Over Malicious AWS Community AMIs | Threatpost #cybersecurity threatpost.com/malicious-aws…
Working from home causes surge in security breaches, staff 'oblivious' to best practices | ZDNet #cybersecurity zdnet.com/article/working-fr…

CISA warns of BLINDINGCAN, a new strain of North Korean malware #cybersecurity #cyberespionage zdnet.com/article/cisa-warns…
“Death from Above: Lateral Movement from Azure to On-Prem AD” “Death from Above: Lateral Movement from Azure to On-Prem AD” by Andy Robbins #cybersecurity posts.specterops.io/death-fr…
Decrypted: Hackers show off their exploits as Black Hat goes virtual #cybersecurity #securityexploit techcrunch.com/2020/08/15/de…
Talos Blog || Cisco Talos Intelligence Group - Comprehensive Threat Intelligence: Attribution: A Puzzle #cybersecurity #threatintelligence blog.talosintelligence.com/2…

The NSA and FBI Expose Fancy Bear's Sneaky Hacking Tool | WIRED #cybersecurity #cyberespionage wired.com/story/nsa-russian-…

NSA, FBI Warn of Linux Malware Used in Espionage Attacks | Threatpost #cybersecurity #cyberespionage threatpost.com/nsa-fbi-warn-…
Case Study: Catching a Human-Operated Maze Ransomware Attack In Action - SentinelLabs #cybersecurity #cybercrime labs.sentinelone.com/case-st…

FBI and NSA expose new Linux malware Drovorub, used by Russian state hackers #cybersecurity zdnet.com/article/fbi-and-ns…
Black Hat 2020: Web cache poisoning offers fresh ways to smash through the web stack #cybersecurity portswigger.net/daily-swig/b…

When TLS hacks you: Security friend becomes a foe | The Daily Swig #cybersecurity portswigger.net/daily-swig/w…
