

InfoSec for zero carbon living. Back in🇬🇧 after 🇮🇹 🇦🇪 🇪🇸 and 🇨🇳 Former egg-chaser 🏉 Views own.
Various
Joined September 2014
- Tweets830
- Following356
- Followers164
- Likes495





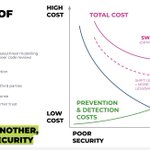

Software security as a system control problem - Coach CISO coachciso.com/posts/software…
The ability to destroy a planet, or even a whole system, is insignificant next to the power of the Force.

ALT Picture of a sunset.

Somebody who works in security should probably have a word with Fortinet’s event marketing team. No irony detected.

Thoroughly enjoyable panel at the European CISO Community event in Cascais, Portugal sharing the stage with the ever erudite @philvenables discussing the relationship between org culture and tech (and cyber) industrialisation.
Such an important concept that a lot of public reporting misses

I’m speaking at eCrime tomorrow at 9am. Will be talking about experimenting with user story mapping for security. Where my hecklers at*?
*no trolling please

Simon Goldsmith retweeted

SaaS vendors: if your core business is not as an identity SaaS SSO provider, but you charge almost twice per seat to enable SSO access to your product, making using your product easier, more secure & offload work/risk from you, you are ripping ppl off. SSO != Enterprise feature.


Today is the day! 📢 If you're at @RSAConference this week don't miss @mgm_cybersec and @CyberGoldsmith today at ⏰ 14:20 local time ⏰ at Moscone West 2006, for their talk on the rise of bots and what to do about it. More: netacea.blog/3NQjOC8 #RSAC2022 #CyberSecurity #bots

Very best of luck to @mgm_cybersec at #RSAC 2022 tomorrow. COVID has got in the way of me ‘helping’ but attacker automation is a fascinating topic which MGM excels at explaining. Also a shout out for fledgling open-source @BladeFramework community. #botmenace

Simon Goldsmith retweeted

Less than 2 weeks until we land at
@RSAConference in San Francisco! #RSAC2022
Don't miss @mgm_cybersec and @CyberGoldsmith @OVOEnergy at their speaker session on the rise of bots and what to do about it.
🤖 Mon 6th June
🤖 2.20PM PDT
🤖 Moscone Center
See you there! 👋 – at San Francisco, CA

More of this please (sharing near misses not the phishing). Less victim blaming, more collective learning on how to trigger the security centre in all our brains. Thank you @kelseyhightower!
This Post is from an account that no longer exists. Learn more
Simon Goldsmith retweeted

What is very clear to me, at least, from this Conti leak is that we need to seriously stop with Active Directory now. We pretend we know how to do it but the fact is, it continues to be that pig with lipstick on that no one can secure and attackers find so easy to own
Simon Goldsmith retweeted

If you are in the US/UK/ANZ at a small co-op/muni & need ICS cybersecurity support (Dragos Platform technology, managed service, and incident response) please feel free to message me directly. Dragos is going to make our capabilities free for the smaller members of our community
@CISAgov @CISAJen making moves. What say you @NCSC @Lindy_Cameron? dhs.gov/news/2022/02/03/dhs-…
Security is *just* an outcome. It’s not your worth. A New Year has arrived, the popular thing to do is to write down what we aim to do, what goals we are going to smash. But the starting point of an information security team should be who we aim to be. linkedin.com/pulse/security-…

Given we’re in prediction season, has anyone seen any well explained analysis (@swardley map-esque) on the evolution of criminal value chains from bespoke TTPs to product/service? Also, anyone else had enough black box threat predictions?
Dear Twitter, I present to you the perfect Information Security sporting analogy.
