

24/7 AI security for Discord & Telegram — catching fakes before your community does
Joined July 2026
- Tweets55
- Following3
- Followers24
- Likes11


Pinned Tweet
Over $300M is lost every year not to smart contract exploits, but to social engineering — fake DMs, cloned staff handles, and malicious phishing links across Telegram, X, and Discord.
Scammers don't hack just code. They hack human trust.
We built Fraudify to end this permanently — an AI-powered security system that combines fuzzy string distance heuristics with RAG pipelines to audit identities and analyze message context in real time inside DISCORD.
How Fraudify stops malicious links before members click:
🛡️ Instant Scan: Evaluates domain structure, redirection patterns, and known threat heuristics.
⚡ Zero-Delay Action: Deletes unverified malicious links the second they appear in chat.
🚨 Global Red Alert: Flags the attacker’s account across every protected server in the network.
Community security that never sleeps.

A scammer gets flagged in one community.
Hours later, they try the exact same tactic in yours.
Fraudify’s Global Red Alert system logs flagged threats cross-server—so an attacker caught in Server A gets blocked before they can target Server B.
Cross-server intelligence means every community added makes the entire network safer.
Secure your servers with Fraudify.


Standard moderation cannot catch this in time.
Even active mods cannot:
❌ Monitor every member join in real time
❌ Cross-reference every display name against staff handles automatically
❌ Act in under 1 second
Humans are not fast enough for this attack vector. You need automation.
This is exactly what Fraudify was built for.
1. Instant Join Defense
The moment a new account joins with a display name too similar to a staff handle, Fraudify bans them automatically.
Before they DM a single member.
Before any human notices.
Before the attack has a chance to start.
2. On-Demand AI Message Audits
What if a message slips into a grey area or a suspicious DM lands in a member's inbox?
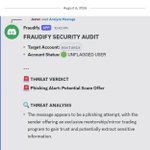
Right-click ➔ Analyze Message: Runs our local RAG engine to give an instant AI threat report on any message, link, or offer.
Verify Sender: Instant identity checks to confirm if the account is a real staff member or an impersonator clone.
Prevention at entry. AI verification on demand.
This is what 24/7 actually means.
Your Discord server has a fake admin right now. You just don't know it yet.
Scammers don't hack code anymore, they hack human trust.
Fraudify catches handle clones in <10ms and auto-bans impersonators before your members even see them.
Impersonator joined. Banned. Logged. Protect your community today 🛡

Fraudify retweeted
LASTLY,
Fraudify devs offer Fully Managed Security for Projects
We operate on a white-glove managed model. We handle backend license provisioning, link whitelisting, and threat monitoring so server owners get zero-friction 24/7 protection.
🚀 Protect your community today: 📩 DM us to onboard your server or add Fraudify to your Discord!
🔁 Retweet this tweet to spread awareness & keep communities safe!
fraudify.gitbook.io/fraudify

Fraudify retweeted
Feature 7
[Community Flagging & Red Alert Network (/flag or !flag)]
Spotted a fishy message in a public channel or group? Any community member can reply directly to the suspicious message with /flag or !flag.
Fraudify evaluates the message intent, records a community flag strike against the scammer in our central Red Alert database, deletes the malicious text, and automatically applies timeouts or permanent bans upon reaching strike thresholds

Fraudify retweeted
Feature 6
[Verified Directory & Staff Query Commands]
Members never have to guess if a link or mod is real:
/link — Displays only official, verified server directory links.
/staff — Lists registered, protected staff handles with clickable mentions.
/faq — Scans server metadata, created date, and active security status.
/commands & /help — Pulls up the complete command center reference menu.


Fraudify retweeted
Feature 5
[Automated Impersonation Shield & Instant Bans]
Fraudify doesn't just warn users -it actively shields the server.
If a malicious user joins a protected server attempting to impersonate official staff handles, Fraudify detects the spoof and automatically executes a server ban.

Fraudify retweeted
What if a stranger in your DMs is NOT cloning an admin, but still sends a fishy message pitching a fake trading scheme, drainer link, or scam deposit?
Running "Analyze Message" passes the raw text through our local RAG pipeline to evaluate message intent independently of account handles:
-Intent Analysis: Detects social engineering traps, urgency patterns, and financial manipulation.
-Link Inspection: Scans URLs for unverified domains, drainers, or malicious redirects.
-Threat Verdict & Actionable Guidance: Returns clear verdicts (LOW-RISK or RED ALERT / SCAM THREAT) along with direct instructions on what to do next.


Fraudify retweeted
Feature 3
[Handle Clone Detection (Verify Sender)]
If a scammer attempts to clone an admin handle eg. (elvis._o vs elvis._.o), Fraudify’s fuzzy string algorithm catches character manipulation instantly.
It flags the account, calculates similarity percentage, and warns the user in < 10ms.
