

24/7 AI security for Discord & Telegram — catching fakes before your community does
Joined July 2026
- Tweets55
- Following3
- Followers24
- Likes11


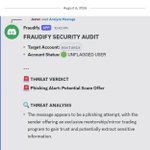
How Fraudify stops malicious links before members click:
🛡️ Instant Scan: Evaluates domain structure, redirection patterns, and known threat heuristics.
⚡ Zero-Delay Action: Deletes unverified malicious links the second they appear in chat.
🚨 Global Red Alert: Flags the attacker’s account across every protected server in the network.
Community security that never sleeps.

A scammer gets flagged in one community.
Hours later, they try the exact same tactic in yours.
Fraudify’s Global Red Alert system logs flagged threats cross-server—so an attacker caught in Server A gets blocked before they can target Server B.
Cross-server intelligence means every community added makes the entire network safer.
Secure your servers with Fraudify.


2. On-Demand AI Message Audits
What if a message slips into a grey area or a suspicious DM lands in a member's inbox?
Right-click ➔ Analyze Message: Runs our local RAG engine to give an instant AI threat report on any message, link, or offer.
Verify Sender: Instant identity checks to confirm if the account is a real staff member or an impersonator clone.
Prevention at entry. AI verification on demand.
This is what 24/7 actually means.
Standard moderation cannot catch this in time.
Even active mods cannot:
❌ Monitor every member join in real time
❌ Cross-reference every display name against staff handles automatically
❌ Act in under 1 second
Humans are not fast enough for this attack vector. You need automation.
This is exactly what Fraudify was built for.
1. Instant Join Defense
The moment a new account joins with a display name too similar to a staff handle, Fraudify bans them automatically.
Before they DM a single member.
Before any human notices.
Before the attack has a chance to start.
Your mods find out later when someone that fell for the scam realize they've been scammed.
"hey did anyone else get a DM from the team about a whitelist?"
By then:
Multiple members have clicked
The scammer account is already deleted
deposits have been made
The wallets are already drained
There is no undo button.
Then they DM your members.
Most discord scammers have a two-step playbook to steal from you
Step 1: The Fake "Security Notice" DM
A fake admin account DMs you right after you join:
"NOTICE ‼️ You are advised to disable friend requests and DMs for your account security..."
This builds instant, fake trust. They sound like a helpful moderator protecting you.
Step 2: The Trap
minutes later, that same "helpful admin" sends a follow-up DM:
"Hey, we have a special whitelist opportunity for early supporters. Click here to verify your wallet."
or even introducing the member to a broker trading program.
You trust the name because of the earlier warning. You interact because of trust and end up falling for the scam. Wallet drained in seconds.
The Real Lesson:
Humans fall for social engineering because scammers mimic real admins perfectly.
You can't rely on members spotting character swaps or fake handles in their DMs.
Discord has a technical quirk that makes this trivial.
Every user has three identity layers:
Username (account-level, unique)
Display name (can be anything at all)
Server nickname (set per-server, anything)
Scammers copy the display name and nickname.
Most members never look at the actual username.
One character difference. Virtually invisible.
How scammers clone admins in Discord:
The setup takes less time than you think.
Step 1: Find your project on Twitter or Discord Discovery.
Step 2: Screenshot your admin's profile.
Step 3: Create a new account. Copy the display name and avatar exactly.
