

Security @Google God of Slop, Terror of TPUs, Guzzler of Tokens DMs always open HCI 2017-2023, UIUC 2026 - (dropped out) prev - @scryonlabs - @pragnition
Singapore
Joined October 2020
- Tweets203
- Following469
- Followers181
- Likes98

kek retweeted

why pay for GPU-hours if what you need is tokens? just buy token-hours

Dedicated hourly throughput is LIVE on Touchmark.
Reserved in advance with SLAs, priced below on-demand.
Don't need the throughput? Sell it back.
touchmark.ai

kek retweeted

This is the first HIGH severity curl vulnerability in years. It is cool, but take note of the report format. This is the level of detail you should aim for when disclosing vulns hackerone.com/reports/403033…


kek retweeted

i feel like swe interviews could probably collapse into just 2 technical rounds:
• system design (how well can you articulate your ideas, do you actually know how to engineer something)
• onsite project to build a real thing with agents (can you translate your intent into high quality outcomes)
everything else we used to ask is no longer necessary

🗞️ if your team is too busy doing their 'normal job' to experiment with AI, you're preparing them to be replaced
ghuntley.com/replaced/
In this post, I guess this's the last time I'll say it. AI use is no longer optional if you wish to be employed. What follows is advice for current employees and hiring managers on how to hire in 2026 to source AI-first candidates.

kek retweeted

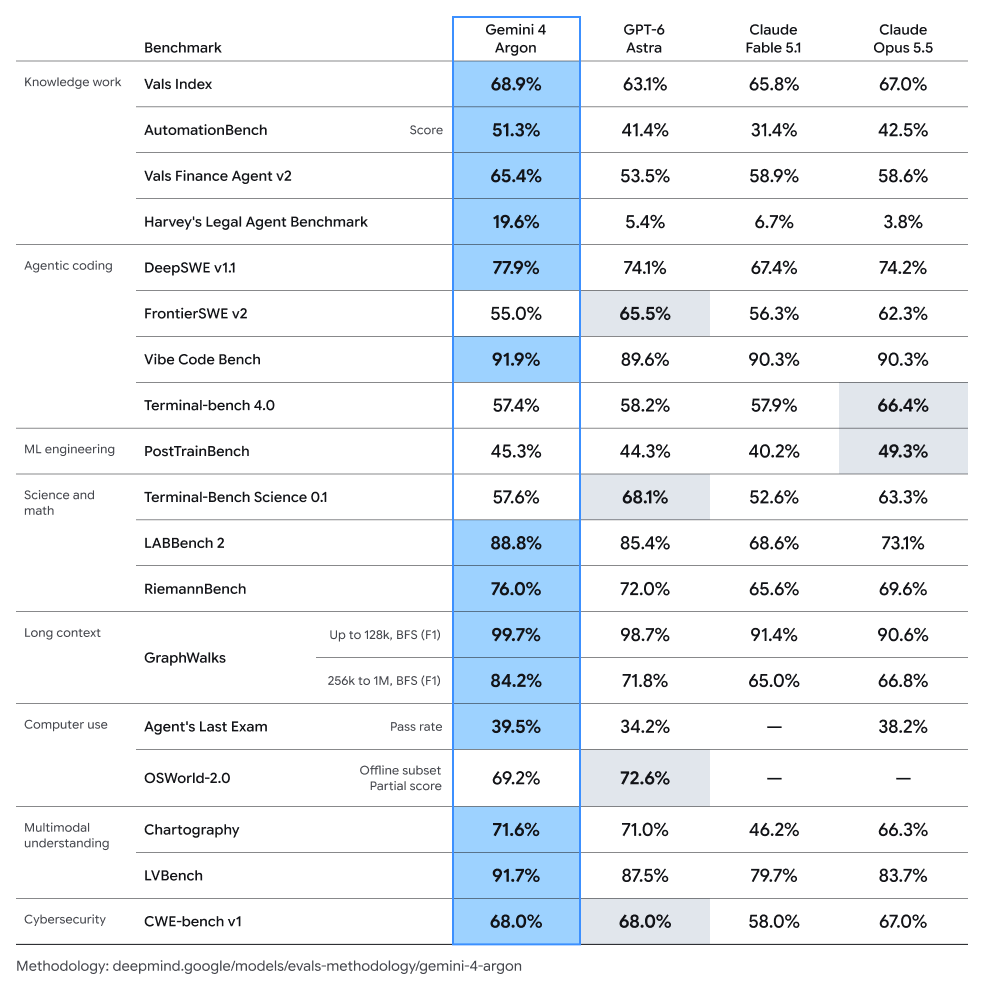
Introducing Gemini 4 Argon – our new frontier model.
It’s built for complex workflows across coding, enterprise knowledge work, and cybersecurity defense – rolling out today to a set of trusted testers through our Fairwind Program.
kek retweeted
Stuck inside a <meta> and angle brackets blocked?
You can still get XSS...
In Firefox, use hidden=until-found and onbeforematch with a URL hash to trigger your handler.
Now in our XSS cheat sheet, thanks to @avlidienbrunn

ALT <meta name=description content=x id=p hidden=until-found onbeforematch=alert(document.domain)>
kek retweeted
Disclosing Branch Target Reuse (BTR): speculative execute-after-free in JIT engines. Code gets freed, but branch predictions survive. BTR exploits this mismatch to mount practical Spectre-v2 attacks (cBPF /etc/shadow exploit demo below). Details at: vusec.net/projects/btr
kek retweeted

ESCAL8, Google’s annual flagship security conference, is coming to Singapore in October 2026, with a particular focus on AI Agents! 🇸🇬
Check out our blog post to see what's planned in the three main segments of the conference: bugSWAT, Hackceler8, and init.g() 👇
bughunters.google.com/blog/e…

kek retweeted

Grok 4.7 is here and we put it through our offensive security benchmarks and workflows.
tl;dr: The results were mixed: Grok 4.7 performed worse than 4.6 in some tests, significantly better in others. The biggest difference wasn’t in how it performed, but when.
More findings in thread 🧵
kek retweeted
Recently, I've been looking at DOMPurify again, trying to find ways to bypass 3.x.x after browsers started encoding attrs during serialization.
I ended up with a nice ≤3.2.6 Safari default-configuration bypass using only SMIL tags/attrs :D
Details 👇
mizu.re/post/dompurify-bypas…

ALT https://yeswehack.github.io/Dom-Explorer/shared?id=9c1f671a-fc8f-4284-9217-eba4df143db3
kek retweeted

What if I told you that Scaled Dot-Product Attention (SDPA) doesn't make a whole lot of sense for ViTs and you can get faster convergence, better performance and near-linear scaling with a few well-steered Gaussians?
Let me introduce you to SSOG (Separable Sum Of Gaussians)!
kek retweeted

OpenAI posted a job opening for "Power Trading Lead", responsible for developing and executing hedging strategies for power and gas for data centers.
First job like this I've seen them advertise.

kek retweeted
Exa is now one of the largest indexes in the world.
We serve 80B pages, track 1.4T urls, and are on track to be Google-scale in early 2027.
It's difficult to know the size of indexes, but we estimate Google to be ~1T, Bing to be ~500B, and Yandex ~200B. Brave mentioned in April that they're at 40B.
Most of the web is trash that can hurt AI outputs, so you actually have to crawl way more than you serve and train models to filter out the trash.
In terms of peak QPS, we estimate Bing at roughly 30k/s and Google at ~500k/s.
In our case, because agent traffic often requires large fan-out (deep searches can use dozens of sub-searches) and can be spiky (like when AI labs RL with us), we're already starting to provision for Bing-scale traffic.
Within 2 years, agents will search at many millions per second. They'll also want comprehensiveness over all data, far bigger than any index today. So the retrieval infra required will be larger than Google-scale in both dimensions.

kek retweeted

Today we're announcing dfs-large1, our newest cybersecurity model that achieves best-in-class performance on vulnerability detection tasks.
Besides frontier AI labs, only a handful of companies have built specialized models that reach the state of the art in their domain. We're proud to be the first to do it for cybersecurity.
dfs-large1 is built on GLM-5.2 and post-trained with reinforcement learning inside depthfirst's security infrastructure. We evaluated it on depthfirst-bench, our benchmark of long-horizon vulnerability discovery across complex repositories, where it achieves best-in-class performance.
Training improvements have not plateaued yet and we expect additional performance gains as we continue training.
A huge thank you to @FireworksAI_HQ for being an outstanding training partner. Their infrastructure enabled us run large-scale reinforcement learning efficiently and iterate much faster.
dfs-large1 is now in preview within the @depthfirstlabs platform

kek retweeted

Put good builders in one room and something always comes out of it. superteam lunch today 🙌

kek retweeted

That's a wrap on Pwn2Own Berlin 2026! 🏆 $1,298,250 awarded. 47 unique 0-days. 3 days of absolute chaos. And talk about main character energy - congrats to DEVCORE for claiming Master of Pwn with 50.5 points and $505,000 - they never slowed down. See you next year! #Pwn2Own #P2OBerlin


kek retweeted

Use tabby?
1. cat readme.md
2. ???
3. pwned
Here's how we abused a terminal output/input boundary and the ZMODEM protocol to achieve silent command execution on tabby.
blog.scryonlabs.com/posts/ca…
GHSA: github.com/Eugeny/tabby/secu…