

Red Team & security research & programming.
Joined April 2024
- Tweets196
- Following92
- Followers1.3K
- Likes1K




Print3M retweeted

Nothing beats the feeling when someone is inspired by your work and builds off it to release something even cooler.
These slides have me hyped for the talk recording!

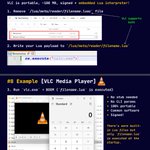
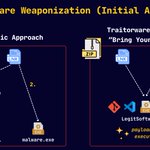
I’m sharing my slides from @x33fcon 2026.
Inside ~15 examples of abusing traitorware to execute your payload via trusted & signed binaries (e.g. VLC Player, SublimeText) and how to find more of them.
Recording will be published soon.
github.com/Print3M/MyTalks/b…


Print3M retweeted

### Top-Line Findings
1. **The C2 ecosystem is far less diverse than it appears.** While there are 30+ "different" frameworks, the underlying technique implementations converge on a small number of canonical code patterns, many traceable to specific open-source authors or blog posts.
2. **Three source projects account for the majority of reused code:**
- **TrustedSec's COFFLoader** — the ancestor of nearly every open-source BOF loader
- **PowerSploit** (by @harmj0y, @mattifestation, @obscuresec) — Get-Keystrokes, Invoke-Mimikatz, PowerView, and persistence modules are shipped verbatim by Empire, PoshC2, PowerHub, Amnesiac, and Shad0w
- **Kevin Robertson's Invoke-WMIExec/Invoke-SMBExec** — the dominant PowerShell implementations for WMI and SMB lateral movement, bundled by Empire, PoshC2, PowerHub, and SilentTrinity
3. **A single detection rule can catch multiple frameworks.** Because many C2s share identical implementation code:
- One detection for the PowerSploit `Get-Keystrokes` GetAsyncKeyState polling loop catches Empire, PoshC2, and any framework that bundles PowerSploit
- One detection for the TrustedSec COFFLoader relocation pattern catches Apollo, Loki, Sliver (extension), and derivatives
- One detection for the .NET `ManagementScope` WMI pattern catches Apollo, Covenant, NimboC2, SilentTrinity, and DeimoC2
4. **Genuinely novel frameworks are rare.** Of the 30 analyzed:
- **4 frameworks** (Sliver, Havoc, Realm, TripleCross) demonstrate significant code originality
- **6 frameworks** show moderate originality (Wyrm, AdaptixC2, Emp3r0r, Merlin, NimPlant, GC2)
- **20 frameworks** rely heavily on shared code from the three source projects above, or implement techniques using the same well-known recipes
5. **HTTP C2 communications show the most behavioral convergence.** Three jitter formula families, shared User-Agent strings (the IE11 UA appears in Empire, Nuages, and Covenant), and common URL path patterns create fingerprinting opportunities.

Print3M retweeted

we told claude code + sonnet 4.5 to rewrite our entire typescript repository in go
it ran for 29 hours
results below:
Print3M retweeted

Azure AD via weak ACLS (@xybytes), HTTP stealth proxy (@IAmMandatory), Dll sideloading for initial access (@Print3M_), kernel-hack-drill (@a13xp0p0v), and more! blog.badsectorlabs.com/last-…

Print3M retweeted

CISSP ❌
CRTP ❌
the actual hands-on red teaming course with 1.337% pass rate 👇✅
bonus, it is taught on real systems

Print3M retweeted

If you haven’t already, check out @Print3M_’s research on File System APIs here: print3m.github.io/blog/filej…
We went down the exfil path for this research, but certainly some abuse potential there!


An infostealer that runs in the browser? Kinda.
In our latest research, we explore how Chromium File System APIs can be abused to exfiltrate mapped network drives with a single drag-and-drop.
Blog: blog.delivr.to/filejacking-e…
Print3M retweeted

Sadly, GPT-6 will only provide a 20% increase over GPT-5. The rate of progress is clearly slowing.
Print3M retweeted

#oldnewthing
Need something blue? Create the file "C:\Windows\System32\config\OSDATA" and restart Windows. You’ll get a permanent Blue Screen of Death( BSOD ).
#pentester #redteam


Print3M retweeted
Many people wanted my slides from the Windows Client Privilege Escalation webinar yesterday.
Here are links to the slides and the recording of the webinar.
slideshare.net/slideshow/win…
youtu.be/EG2Mbw2DVnU?si=rlx-…

Print3M retweeted
Confirm. No Hat is already on SecTube! Serving up 13 unique presentations from the 2024 edition 🫡
sectube.tv/events/no-hat

thanks to @Print3M_, all #NoHat2024 recordings have been categorized & summarized: sectube.tv/events/no-hat
Big thanks for making our talks more accessible! Check out their amazing project sectube.tv
#nohat #computer #security #conference #cybersecurity

Print3M retweeted

I spent the last month reverse engineering Call of Duty's anti-cheat!
Blog post here: ssno.cc/posts/reversing-tac-…


Print3M retweeted
The Polish national CERT puts out a detailed article about Facebook ad scams. They publish it, but then, poof! The post gets removed. And every single post with a link to that article also disappears. Not sure if really surprising...
cert.pl/posts/2024/11/blokad…

