
Sh0ckFR retweeted

Do you want to trigger shellcode only when:
- Certain DNS resolution happens?
- Certain servers are reached out to?
- When you get a 112 byte long response?
...etc
Meet InternetSetStatusCallback() for fine tuning execution (or if you are just bored):
gist.github.com/whokilleddb/…

Sh0ckFR retweeted

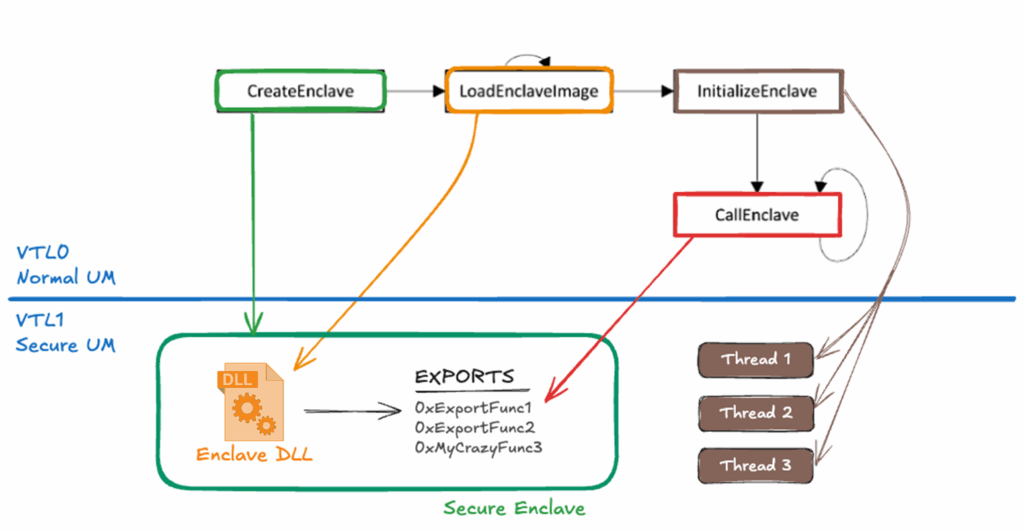
Secure enclaves in post-exploitation world.
A strategy to exploit vulnerable enclave DLLs and transform ROP-based execution to hide implant memory during sleep.
Fantastic post by Cedric Van Bockhaven (@c3c) of Outflank Team (@OutflankNL)!
Source: outflank.nl/blog/2025/06/16/…
#redteam #blueteam #maldev #malwaredevelopment

Sh0ckFR retweeted

Hosts running the WebClient service are prime targets for NTLM relay attacks, and it may be possible to start the service remotely as a low-privileged user.
@0xthirteen breaks down the service startup mechanics, plus the protocols and technologies. ghst.ly/41QT7GW
Sh0ckFR retweeted

"The Hacker's Renaissance: A Manifesto Reborn" 🔥
phrack.org/issues/72/19#arti…
Sh0ckFR retweeted

For anyone using BRC4. My colleage @dis0rder_0x00 ported several BOFs to COFF format and we made a pull request to the official repo: 🔥🔥
github.com/paranoidninja/BRC…
Including:
AAD PRT
Get Azure Token
Multi RDP
PetitPotam
Session Enum
SelfDelete
Cookie Monster
SSPI UAC Bypass

Sh0ckFR retweeted

Today, together with Jonathan Elkabas, we're releasing EntraGoat - A Deliberately Vulnerable Entra ID Environment.
Your own hands-on Entra lab for identity attack simulation.
Built for red teams, blue teams and identity nerds.
Check it out here👉github.com/semperis/entragoa…

Sh0ckFR retweeted

🔥 A hacker gang planted a 4G Raspberry Pi inside a bank’s ATM network—bypassing firewalls to install a rootkit called CAKETAP.
It spoofed PIN checks, hid processes, and aimed to trigger fraudulent withdrawals.
Details you should know ↓ thehackernews.com/2025/07/un…

Sh0ckFR retweeted

Happy Friday! We're ending the week by publishing our analysis of Fortinet's FortiWeb CVE-2025-25257....
labs.watchtowr.com/pre-auth-…

Sh0ckFR retweeted

CVE-2025-5777 Citrix NetScaler Memory Leak
Severity: CRITICAL ⚠️
PoC: github.com/win3zz/CVE-2025-5…

Sh0ckFR retweeted

Shellcode injection using MessageBox ghostline.neocities.org/Mess…

Sh0ckFR retweeted

Locate dll base addresses without PEB Walk:
github.com/Teach2Breach/moon…

Sh0ckFR retweeted

Session keys and passwords aplenty, here’s our deep-dive for CVE-2025-5777, aka CitrixBleed 2. Apart from the normal root-cause analysis, we’ve doubled down on actionable steps to investigate Indicators of Compromise.
horizon3.ai/attack-research/…

Sh0ckFR retweeted

PowerShell's Test-NetConnection is too slow, so I wrote a simple function to check if specific TCP ports are opened quickly without ping.
Would be helpful TCP port sweeping.
gist.github.com/daem0nc0re/1…

Sh0ckFR retweeted

ProxyBlob is alive ! We’ve open-sourced our stealthy reverse SOCKS proxy over Azure Blob Storage that can help you operate in restricted environments 🔒
🌐 github.com/quarkslab/proxybl…
Blog post for more details right below ⬇️


Look at those cute little blobs in your internal network. They look harmless, but how about the one carrying SOCKS? It's ProxyBlob, a reverse proxy over Azure.
Check out @_atsika's article on how it came to exist after an assumed breach mission ⤵️
👉 blog.quarkslab.com/proxyblob…

ALT Proxybloby is the red teamer's mascot. Be careful, if left alone in you network it will byte your SOCKS
Sh0ckFR retweeted

With some guidance from @DebugPrivilege I've found a way to easily dump clear text implants even while they sleep. Bad day for sleep obfuscation 💤
blog.felixm.pw/rude_awakenin…

Sh0ckFR retweeted
I'm reposting my IBM blog dealing with Lazarus and "Direct kernel object manipulation (DKOM) attacks on ETW providers" on knifecoat 🔪🧥
knifecoat.com/Posts/Direct+K…

Sh0ckFR retweeted

Easter drop 🐣: Chrome App-Bound Encryption Decryption (CreateRemoteThread + LoadLibrary Injection)
• No more admin rights
• No path constraints - run anywhere
• Chrome / Brave / Edge
• No Alert on Defender 4.18.24030.5
github.com/xaitax/Chrome-App…

Sh0ckFR retweeted
Exploiting the Nespresso smart cards for fun and profit coffee
pollevanhoof.be/nuggets/smar…


Sh0ckFR retweeted
InlineWhispers3: Tool for working with Indirect System Calls in Cobalt Strike's Beacon Object Files (BOF) using SysWhispers3 for EDR evasion github.com/tdeerenberg/Inlin…
