

OSINT & Blockchain Intelligence Analyst @Certik @CertiKAlert l Steward & contributor @_SEAL_Org
everywhere
Joined May 2023
- Tweets984
- Following859
- Followers165
- Likes1.3K





Pinned Tweet
Two years ago, for @CertiK, I wrote one of the first documented reports on wrench attacks.
Today I've authored the "Coercion & Duress" framework for @_SEAL_Org.
🙏 Now steward for this section. TY @_SEAL_Org .
Link 👇
frameworks.securityalliance.…

AllyPry retweeted

#CertiKInsight 🚨
@x100global attacker is currently sending funds to Tornado Cash: etherscan.io/address/0x82967…
300 ETH ($690k) has already been sent so far.
CertiK Report Security Dashboard 👇
certik.com/certik-report/das…

For those who still doubted that France was on its way to becoming a dictatorship... 👇
Strange how many media outlets are having a hard time covering the news and what's happening today in France on X. Coincidence? 🤔

Just in: France's Prime Minister asked telecom companies to prepare to block social media platforms. "I wish to have the ability to temporarily suspend access to these services in case of a repeat of urban violence," he wrote. @blast news broke the story.

Sooooo no one is safe...
xitter.cf/KeystoneWallet/status/…

We owe you an apology.
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we didn't keep them safe.
Exposed: names, contact details, shipping addresses, and order details (items and prices).
Not exposed: payment card or bank details, recovery phrases, private keys, or wallet passwords.
We've blocked access, fixed the vulnerability, opened an investigation, and are emailing affected customers.
Scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or "fixes" for your order or address. None of it is from us.
NEVER share your recovery phrase or private keys, and NEVER enter your recovery phrase into a device you didn't order. We will never ask for them. Don't click links in unexpected messages. Type keyst.one yourself.
A detailed report is coming soon.
Until then, trust only our official channels. If anything feels off, email [email protected]. We'd rather hear from you than have you take a chance.
Again, we're truly sorry to everyone affected.
AllyPry retweeted
#CertiKInsight 🚨
On 30 Sept, HOT Omni Bridge on NEAR was exploited resulting in five observed BSC treasury payouts totaling $3.86M, which was later returned.
Read our full analysis here👇
certik.com/blog/hot-bridge-n…
CertiK Report Security Dashboard 👇
certik.com/certik-report/das…

AllyPry retweeted
🚨 #CertiKInsights
We have seen suspicious movement from @79thVault .
2.01M 79AU were sold via a privileged function, moving 16.2k BNB (~$12.5M) to attacker: bscscan.com/tx/0xee0e4416751…
~90% held at: bscscan.com/address/0xa9537B… to which a 10% bounty was offered.
Stay Vigilant!


AllyPry retweeted

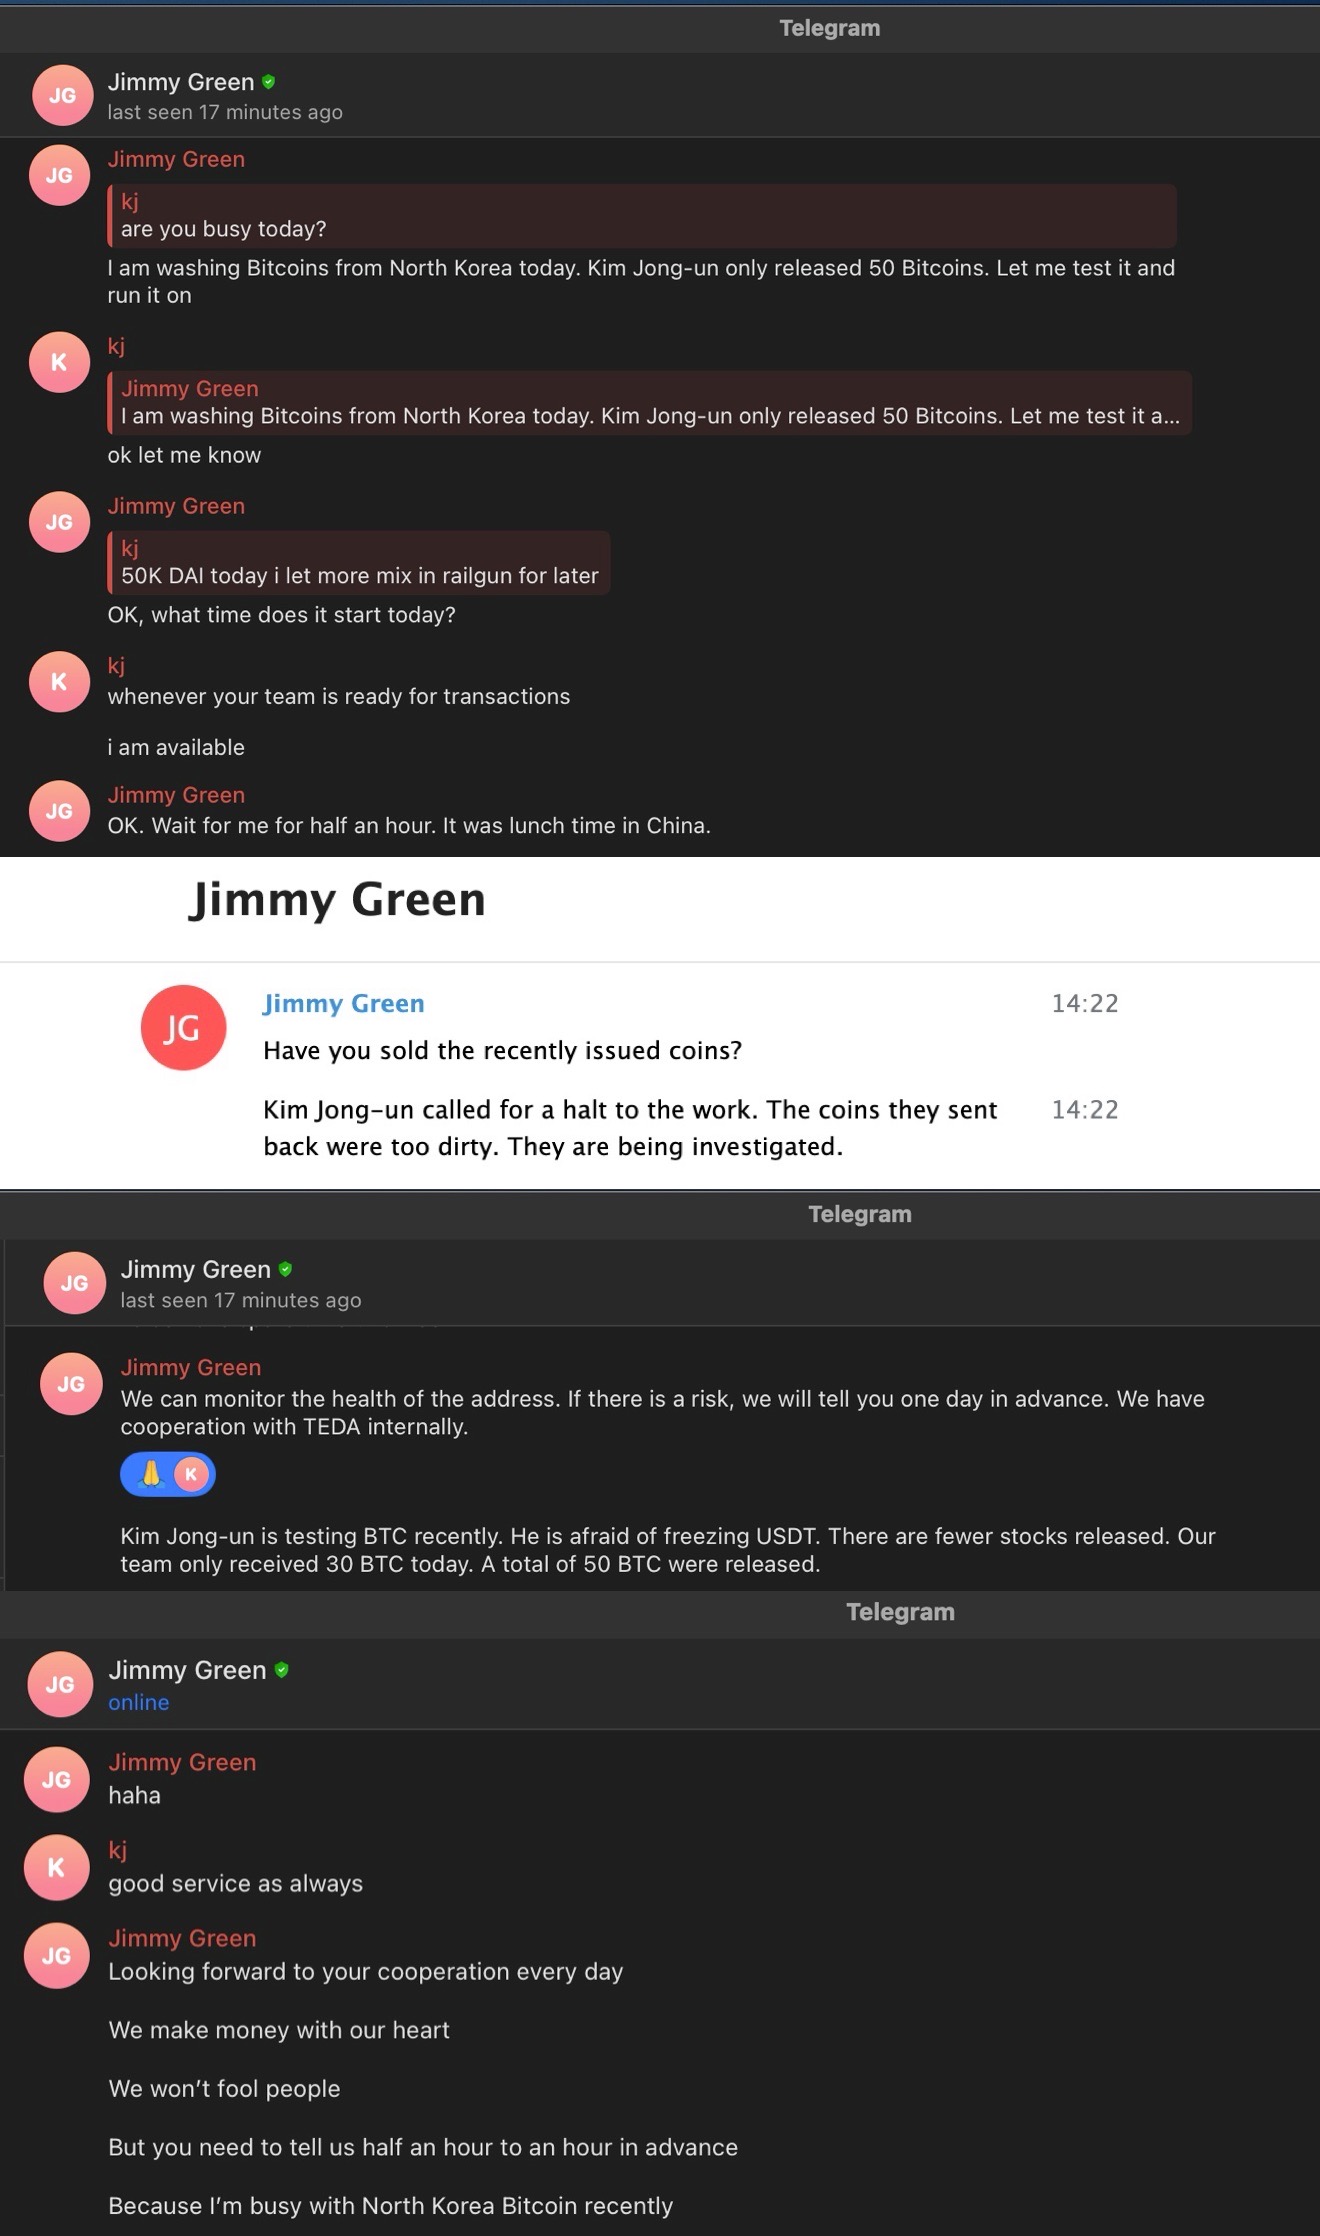
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

AllyPry retweeted
#CertiKInsight 🚨
We have seen suspicious fund movement on Base.
A newly deployed proxy was used to borrow ~1,783 aBaswstETH from vault
basescan.org/address/0xD1895…,
later redeemed via Aave for ~1,783 wstETH (~$6M) now at
basescan.org/address/0x0B512…
Stay Vigilant!

AllyPry retweeted

SEAL Frameworks are now in the @fund_defi OPSeC Repository!
AI security, prompt injection, data exfiltration, sandboxing, security awareness, etc.
Free, chain-agnostic guidance that builders and policymakers can both use.
opsec.defieducationfund.org/…

Better-informed policy is good for everyone building in this space. OPSeC gives our industry a way to make that happen by curating free security resources, hosting educational events, and ensuring technical frameworks reach the policymakers who need them.
Learn more: defieducationfund.org/defi-e…

AllyPry retweeted
#CertiKInsight 🚨
1/4
According to our data, September 2026 recorded ~$772.4M in losses.
Full dashboard & stats 👇
certik.com/certik-report/das…
Here are the key takeaways you need to know 🧵

AllyPry retweeted
September was a stark reminder of how quickly the threat landscape can shift.
With both losses and incident count reaching their highest levels of 2026, the month’s data reinforces the need for security across every layer.
Full breakdown below ↓

#CertiKStatsAlert 🚨
Combining all the incidents in September we’ve confirmed ~$766.4M lost to exploits and phishing.
September has seen the highest recorded losses as well as the most incidents in 2026.
More details below 👇

Damn what a month... 😞
#CertiKStatsAlert 🚨
Combining all the incidents in September we’ve confirmed ~$766.4M lost to exploits and phishing.
September has seen the highest recorded losses as well as the most incidents in 2026.
More details below 👇
AllyPry retweeted
#CertiKStatsAlert 🚨
Combining all the incidents in September we’ve confirmed ~$766.4M lost to exploits and phishing.
September has seen the highest recorded losses as well as the most incidents in 2026.
More details below 👇
New wrench attack in French today… it never ends 😔
@lopp @beausecurity
ouest-france.fr/societe/fait…

AllyPry retweeted
SEAL weekly stats, 22-29 Sep. We were engaged in 67 incidents.
Losses by category:
1) Fake support caller: $8M
2) Protocol compromise: $2.32M + 703 ETH
3) Seed compromise: $6.74M
4) Infrastructure exploit $1.23M
5) Social engineering: $517k
6) Phishing: $267k + 1,358 SOL
7) Malware: $180k

AllyPry retweeted
How do you know a zkVM actually works as intended?
You prove it.
CertiK researchers formally verified zkWasm using Coq, mathematically proving soundness and knowledge soundness across its circuits.
Now accepted at ACM CCS 2026, one of the top academic security conferences.

AllyPry retweeted
🇰🇷 CertiK is heading to Korea Blockchain Week!
Our team will be joining industry leaders in Seoul to discuss security at the intersection of digital assets, AI, and the rapidly growing tokenized economy.
🎙️ @CertiKjoseph — “Digital Assets & AI Security”
📍 CodeVASP
🕙 10:10–10:25
🎙️ @wisp_fly — “Securing the Tokenized Economy”
📍 STO Summit
🕒 3:00–3:20 PM
If you’re at #KBW2026, come hear from CertiK and connect with our team in Seoul.

AllyPry retweeted
Not only DPRK. A vibe-coded phishing frontend for Microsoft Teams, found in the wild.
With the proliferation of capable, unrestricted LLMs, we often observe unaffiliated threat actors deploying fully vibe-coded malware infrastructure. In this example, an endpoint misconfiguration exposed the phishing kit's assets along with the LLM's comments. Interestingly, the threat actor most likely framed the task as a benign development job - a custom video conferencing platform called "Lassy Meet" - traces of which can also be found on the suspicious GitHub organization that also appears to be LLM-automated.
However, the comments reveal the intent.
IOCs:
223.165.6[.]141
netwitz.zoom01[.]us
teams.mlcrosoff[.]com
github[.]com/altosecteam-org


AllyPry retweeted
CertiK has joined @lfdecentralized, the Linux Foundation’s community for enterprise-grade decentralized technologies.
We’ll contribute our security research, audit, and formal verification expertise to open-source projects and working groups, helping strengthen the infrastructure enterprises and institutions build on.

AllyPry retweeted

How to make security interesting to a wider audience?
Apparently, add AI.
Had a great time talking with @pashov, @allypry and @jgattermayer at @ETHSofiaBG.
