

CoFounder & Chief Research Officer at @AirlockDigital. Practical Execution Control & Allowlisting.
Adelaide, Australia
Joined June 2009
- Tweets1.5K
- Following1.6K
- Followers1.1K
- Likes1.8K
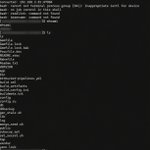
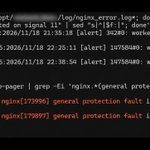




We've also gotten to unauthenticated reverse shell POC working. I know we're all tired of *2shell vulns and it's GTA6 day, but it is worth checking where in your env nginx is used (by your vendors too) and test if http2 is enabled. #CVE-2026-123007 #NGINX2Root


We've recreated the POC and had it write files into docker containers hosting vulnerable nginx. It looks like about 60-100GB.
Observed impact: one NGINX worker received SIGSEGV. The master stayed up, replaced that worker, and /health returned HTTP/2 200 afterward. Connections on the crashed worker can be interrupted.
TLS 1.2 crash probe sends about 60 GiB of HTTP/2 plaintext: roughly 8 GiB of carrier frames and 52 GiB of WINDOW_UPDATE frames. The published TLS 1.3 RCE path uses about 119 GiB.
Also:
sudo journalctl -k --no-pager | grep -Ei 'nginx.*(general protection fault|segfault)'

curl -ksS --http2 -A 'Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/157.0.0.0 Safari/537.36' -D - -o /dev/null xxx.xxx.xxx.xxx:443/ | grep -Ei '^(HTTP/|server:)'
HTTP/2 200
server: nginx/1.31.8
128
We've recreated the POC and had it write files into docker containers hosting vulnerable nginx. It looks like about 60-100GB.
Observed impact: one NGINX worker received SIGSEGV. The master stayed up, replaced that worker, and /health returned HTTP/2 200 afterward. Connections on the crashed worker can be interrupted.
TLS 1.2 crash probe sends about 60 GiB of HTTP/2 plaintext: roughly 8 GiB of carrier frames and 52 GiB of WINDOW_UPDATE frames. The published TLS 1.3 RCE path uses about 119 GiB.
Also:
sudo journalctl -k --no-pager | grep -Ei 'nginx.*(general protection fault|segfault)'

This screwed up my metric for how long it takes to go from blogs and videos about a new bug to some random person on GitHub reliably reproducing it, since they were in the mix on this one.
github.com/sfewer-r7/CVE-202…


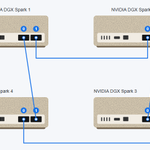
Had trouble finding a 4x DGX Spark ring diagram when I was building it, so sharing in case it comes up in search.

Another fantastic @defcon talk from Bruce Schneier. youtube.com/watch?v=eEBv0STi…
233
Daniel Schell retweeted

interesting... a car is just a concept. looking at the "physics" stats bare like this is interesting. very intriguing spline reference + momentum control system instead of tire physics
It's essentially a brick running on vaguely invisible rail


Someone had to do it. Real macro allowlisting, coming soon to @AirlockDigital.

Really enjoyed watching Cliff Stoll's Defcon talk.
youtube.com/watch?v=656058Jx…
Get his book if you haven't read it: amazon.com.au/Cuckoos-Egg-Cl…

Me right now.
Big @AirlockDigital announcement for Blackhat having added in-line Agentic AI control and steering - It was a big push to get it ready for @Blackhat. Very proud of the team. Check out the clip below - visit us at the booth to check it out!
Big @AirlockDigital announcement for Blackhat having added in-line Agentic AI control and steering - It was a big push to get it ready for @Blackhat. Very proud of the team. Check out the clip below - visit us at the booth to check it out!
Enjoyed conversation on @riskybiz discussing the implications of research in reversing EDR definitions with LLMs. Showout @HackingLZ / @_xpn_ for great research. Listen here: risky.biz/RBNEWSSI137/
What's New in @AirlockDigital v7. Application context is a new feature which is pretty cool - building an application catalog of even internal applications and automatic trust recommendations to build policies faster. Elevation control too.
Very happy with the v7 launch of @AirlockDigital.
Proud of new feature with "App context" being able to enumerate applications (without definitions!) gives such great visibility of what is running in your environment. Allowlisting thinks in files, but we like to think in Apps.


