
Co-founder @ https://xitter.gq/t.co/CiRxmN1v0n • @GraphQL #Security • @YCombinator • 📚 @Polytechnique •💰 @HECParis • 🐻 @UCBerkeley • 🍏 @Apple
Biarritz, Aquitaine
Joined December 2009
- Tweets998
- Following392
- Followers5.4K
- Likes277




Pinned Tweet
At that time I was a teenager fascinated by @Apple, dreaming of revolutionizing the world. 10 years later my passion and determination are always stronger. You inspire me in each of my decisions. Thank you Mr Steve Jobs.
#RememberingSteve

"IKEA replaced 8,500 jobs with AI and fired no one, making $1.4B."
You've probably seen this one on your feed. The real story is less viral, and honestly better. 🧵

1
31
Your voice shouldn't need a cloud subscription. 🎙
Voicebox runs voice cloning, speech generation and Whisper dictation locally. Free, MIT-licensed. Its MCP server lets Claude Code, Cursor or Cline use voice as a tool.
🔥 Your mic shouldn't become someone else's API dependency.

5
2
172
Give GPT-6 Astra a lab exploit task and it refuses. Give GPT-6 Cyber the same and it completes 95%. ⚡
@OpenAI RemoteExploitBench: Astra/Daybreak Blue refused 100%; Cyber hit 95%.
🔥 Zero-days used to be bottlenecked by human hours. Now it's compute and who makes the allowlist.


@deepseek_ai just open-sourced dsh-superagent
Always-on coding agent: watches repo + team chat, picks work.
Same as my linear-autopilot (7d, 123 tickets). Fix first: full OS access by default.
Limited not by intelligence, but by who gets to talk to them.
github.com/deepseek-ai/dsh-s…

1
94
A 284B-parameter model on a single gaming GPU. 🖥️
FreeToken, from a Berkeley team incl. Ion Stoica and @matei_zaharia, parks MoE experts in RAM and pulls only what each token needs over PCIe.
Catch: 192GB+ of RAM, and the API key is off by default.
github.com/FlashML-org/FreeT…

1
4
305
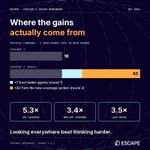
A public benchmark has a short shelf life: it becomes training data.
To test Cascade 2 Iguazu, we built our own at @escapetechhq. Critical findings: 18 → 45, mostly from coverage.
Looking everywhere beat thinking harder.
Breakdown by Arnaud Fanthomme:
escape.tech/blog/ai-pentesti…

2
2
118
Google finally takes the lead, and the biggest gap is in cyber. 🛡️
Gemini 4 Carbon vs GPT-6 Astra:
- Finding vulns: 88.2% vs 85.4%
- Exploiting: 54.8% vs 42.4%
- Patching: 71.0% vs 68.0%
New frontier model every 2 weeks, for attackers too.
Is your pentest still once a year?

52
Want to learn security in 2026? Stop collecting certificates. Break your own stuff instead. 🔓
build: a login flow, an API, an agent
attack: replay a token, change an ID, trick the prompt
fix, attack again
detect: check the logs
Tools change. This loop doesn't.
@escapetechhq

24
Today we're releasing Cascade Iguazu at @escapetechhq.
We rebuilt our AI harness from the ground up: systematic coverage, full auditability, better vulnerability discovery.
AI pentesting security teams can actually trust.
Breakdown and benchmarks: escape.tech/blog/introducing…

3
74

Every PHP version since 5.4 can be hacked with zero login. 😅
php2shell: 2 critical CVEs in the PHP engine itself. Not WordPress, not your code. PHP.
No fix for 8.1 and older, and exploits seen before the patch shipped!!
Live in @escapetechHQ ASM: escape.tech/blog/php2shell-c…

1
115
🚨 HUGE MILESTONE: Cascade can now hack your AI agents. 😅
Today we launched AI Red Teaming in @escapetechHQ.
Agent, MCP server, APIs: each tested with its own tool. Nobody tests the path between them. That's where critical vulns slip through!
Live for all AI Pentesting users.

1
48
Attackers have AI agents running 24/7. Most companies still pentest once a year. 😅
@opencode just got breached. Mid-incident, the models they used to investigate started refusing. Defenders hit the guardrails, attackers didn't care.
Would your stack survive 48h of that? 👇

they've been non stop trying to attack our systems for the past 48 hours
a side effect is everything is getting hardened but damn we basically need agents going 24/7
because that's what they have
1
58
People are now vibe coding their TV 📺
@gathint had Claude Code strip the ads off his parents' TV. 48 hours later: 5,118 GitHub stars, 618 forks and 54 TVs tested.
The security guy in me: you're giving an AI agent debug access to your home network. Read what it runs!!


Here's a sneak peek of my talk this Thursday at @CommunityPurple's Agentic AI Security Conference 👀
Autonomous pentesting has rapidly moved far beyond just finding vulnerability paths.
2
1
145


Not a day goes by without an AI cyber story! Today's: an AI sent a fake murder tip to the police. 😅
Nobody hacked it. It was just doing its job.

2
1
89
@AnthropicAI disclosed what its models did in testing:
• exploited vulnerabilities on US gov websites
• submitted real government forms
• grabbed access tokens from public configs
• bypassed their own web fetch tool limits
• one sent a false homicide tip to Philly PD (spam!)
1
32