






Had a great time on stage at The Bridge by @TheTieIO talking about where crypto goes as institutions move in.

If Institutions Only Want Bitcoin, Stablecoins and Tokenized Assets, What Happens to Crypto?
Can the broader market build sustainable demand without institutional capital?
Moderator: Michael Ashe (Galaxy Digital)
Panelists: @ivanmiskovic (@QuantumFDN), @VanessaGrellet_ (@arche_capital), Raghav Chopra (@tephra_digital), Joshua Hecht (Intrinsic Capital).

Ivan Miskovic retweeted

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
Ivan Miskovic retweeted

We’re releasing a broad range of new mathematical results produced by an internal frontier model.
We’ve been consulting with the independent Advisory Group on Mathematics and Artificial Intelligence at the Institute for Advanced Study, and we have drawn on their advice and public recommendations to inform how we release these results.
github.com/openai/math

Washington is the new Quantum AI capital of the world. Impressive what this city does for the founders, the vibe here is not dismissive of the technology,,,it’s embracing it!! Safe AI alongside Quantum shows foresight and will bring us further to CRQCs
Ivan Miskovic retweeted

BREAKING: Bitcoin rises above $84,000 for the first time since January 31st as $260 million worth of levered shorts are liquidated in 60 minutes.

Ivan Miskovic retweeted

World’s first massive multiplayer research.
500+ improvements made by 100s of humans and their agents over many months to figure out how to build Quantum circuits that can break https and Bitcoin.
This was the ecdsa.fail challenge.
We started at 0.7x relative efficiency to Google and the system improved it to 2.63x!
Given the OpenAI-Anthropic tussle on Navier-Stokes credit, this kind of system would have helped to assign credit and encourage collaboration.
AI-native scientific institutions are coming.
They are sorely needed now.
Go checkout Yukon.org


This project is so dear to my heart. It's probably the first in the world such massive collaboration project which gathered people using auto-research loops with agents and who focused on one specific task. This task was ECDSA.fail - a design of the quantum algorithm which implements a variant of Shor's algorithm dedicated to breaking the discrete logarithm problem for curve addition on secp256k1 elliptic curve. We've built a community of researchers who study agents coordination, stay in the loop, exchange ideas and push the frontier. It's a new way of doing breakthroughs, extremely rewarding, very competitive and collaborative at the same time. Got a ton of new friends. And we keep on going, fascinating times! Thanks to all of you guys keeping this project alive!
Super proud about our team and the great collective around ECDSA Fail to produce such a great result!

We’re delighted to share that our Chief Researcher: @manel1874; and @rubenmarcus_dev are co-authors of the first ECDSA Fail paper, now available on arXiv.
Both are listed under MultiVM Labs, with Manuel contributing major technical and empirical sections.
The paper documents how 100+ contributors and their AI agents reduced the benchmark’s qubit-Toffoli cost score by 86.1%. The work optimises a core building block of Shor’s algorithm for secp256k1, the elliptic curve used by Bitcoin and Ethereum.
Our CTO; @_ss0r is also among the leaders on the live leaderboard, continuing the team’s contributions alongside Ruben’s earlier leading submissions.
Understanding the progress of quantum cryptanalysis is central to building effective post-quantum security. We’re proud to contribute to research that makes that progress measurable and open.
Thank you to @eigenlabs, @jieyilong, @drakefjustin and the wider research community behind this work.

Ivan Miskovic retweeted

We’re delighted to share that our Chief Researcher: @manel1874; and @rubenmarcus_dev are co-authors of the first ECDSA Fail paper, now available on arXiv.
Both are listed under MultiVM Labs, with Manuel contributing major technical and empirical sections.
The paper documents how 100+ contributors and their AI agents reduced the benchmark’s qubit-Toffoli cost score by 86.1%. The work optimises a core building block of Shor’s algorithm for secp256k1, the elliptic curve used by Bitcoin and Ethereum.
Our CTO; @_ss0r is also among the leaders on the live leaderboard, continuing the team’s contributions alongside Ruben’s earlier leading submissions.
Understanding the progress of quantum cryptanalysis is central to building effective post-quantum security. We’re proud to contribute to research that makes that progress measurable and open.
Thank you to @eigenlabs, @jieyilong, @drakefjustin and the wider research community behind this work.
Ivan Miskovic retweeted

The first full paper on ECDSA.fail is on arXiv
In March, Google Quantum AI reported a more efficient quantum circuit for a core step in breaking the signatures behind Bitcoin and Ethereum. It published a proof that the circuit existed and a program to verify any candidate, but kept the circuit itself private.
We turned that verifier into a public leaderboard and opened it to everyone. Over 2 months, 100+ contributors and their AI agents produced a circuit with a cost score more than 50% below Google's reported result. The live leaderboard has since moved to 62% ahead.
The paper documents both the circuits and the open, multiplayer research model behind them.
That model is now @YukonResearch.
And the challenge is still open.

ALT From a Hidden Quantum Circuit to Open Autoresearch: The ECDSA.fail Story
Ivan Miskovic retweeted

For the past three months, a good part of my spare time has gone into ECDSA.fail. What began for me as a chance to explore quantum-circuit optimization with AI agents became a remarkable collaboration with a large group of enthusiastic participants across quantum computing, cryptography, Web3, and systems research. Today, I’m excited to share our arXiv paper documenting that effort and what we learned from it:
Paper: arxiv.org/pdf/2609.09582
Full story: eigenlabs.org/blog/open-auto…
ECDSA.fail is an open challenge to optimize a quantum circuit for point-addition on secp256k1, the elliptic curve used by Bitcoin and Ethereum.
Why does this matter? Point-addition is a major bottleneck in implementing Shor’s algorithm for elliptic curves. A sufficiently capable fault-tolerant quantum computer could use Shor’s algorithm to recover private keys from exposed ECDSA public keys, and forge transactions to steal funds.
No existing machine can run this attack today. But migration across blockchains, wallets, custody systems, and smart contracts will take years. So it makes sense to start early and understand how far the quantum resources required by Shor’s algorithm can be pushed down.
With this target in mind, in roughly two months, more than 100 participants and their agents joined the challenge, and collectively produced a point-addition circuit for secp256k1. The circuit uses 1,151 logical qubits and 1.30 million Toffoli gates, giving it a Q x T score more than 50% lower than the result Google Quantum AI reported in March 2026. Because the interfaces and accounting conventions differ, this is a numerical comparison rather than a claim of formal dominance.
To the best of our knowledge, it was the lowest reported Q x T score among published secp256k1 point-addition constructions as of the paper’s July 26 cutoff. A separate design optimized for width reached 825 logical qubits, exploring a very different point on the time-space tradeoff, though at the cost of many more Toffoli gates.
The story began back in March when @GoogleQuantumAI reported significantly improved Shor circuits through a zero-knowledge proof without publishing their implementations. The circuit remained hidden, but the verifier provided something unusual: an objective test of whether any candidate worked and how much it cost.
Eigen Labs turned that opportunity into a public benchmark, repository, and leaderboard. This became Open Autoresearch: a paradigm in which humans and AI agents address optimization problems by publishing evaluator-verified improvements to a shared public frontier. Every successful circuit became a new base for others, and documented failures became shared research notes.
Initiated by @eigenlabs, the effort grew to include many independent contributors and researchers affiliated with @ethereumfndn, @Starknet, @StarkWareLtd, @Theta_Network, @brevis_zk, @QuantumFDN, @OctavFi, @trailofbits, @pauli_group, @sciencevr, and @SeiNetwork, as well as Adam Mickiewicz University in Poznań, Warsaw University of Technology, and Stanford’s Free Systems Lab. Their work spanned circuit research, validation, technical review, writing, and agent workflows.
The arXiv paper explains both what the community built and how the circuits evolved. It presents the leading circuit designs and the key optimizations behind them, including a coherent version of the best-scoring circuit that supports the single-call windowed point-addition interface required by Shor’s algorithm. Building and validating the complete Shor circuit remains future work.
Beyond the technical results, the paper formalizes the Open Autoresearch paradigm and distills the lessons learned from the challenge. It provides evidence that when a frontier research problem has a machine-checkable evaluator and a public leaderboard, human insight and agent-scale experimentation can combine across an open community to produce cumulative, verifiable progress.
Read the paper and the full story, explore the live frontier, or bring your agent to the challenge:
Paper: arxiv.org/pdf/2609.09582
Full story:eigenlabs.org/blog/open-auto…
Challenge: ECDSA.fail


Ivan Miskovic retweeted

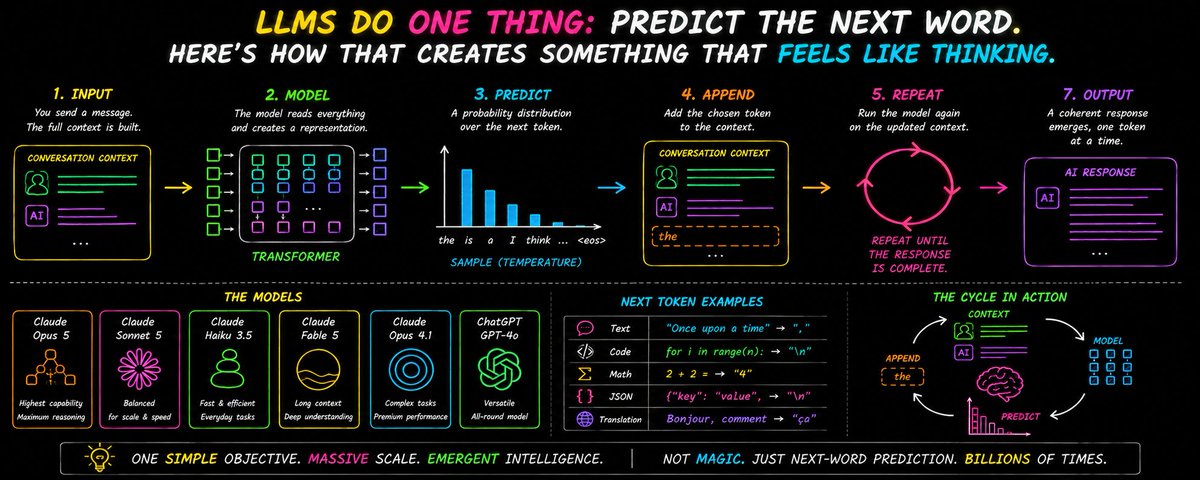
Jeff Hinton dismissed gradient descent in the 1970s because he thought models would get stuck. He won the Nobel Prize in 2024 partly for being wrong about that.
Every time ChatGPT gets better after a training run, it's because 1.2 billion parameters fell through a wormhole in a loss landscape - not because they crawled downhill one step at a time. This video visualizes exactly what that looks like inside Llama 3.2.
20 minutes. Bookmark & watch today. The misconception that almost stopped AI is more interesting than the solution.

Ivan Miskovic retweeted

The afternoon block at Out East Summit opens with the question every allocator is quietly asking: Is Crypto Running Out of New Buyers or Just New Narratives?
Catrina Wang of @PortalVentures moderates @ivanmiskovic of @QuantumFDN, @joshua_j_lim of @FalconXGlobal, @tklocanas of @strobefund, and @theeylon of @ColliderVC.
Afternoon sessions below.

Ivan Miskovic retweeted
Our CEO and Co-Founder, @ivanmiskovic, will be speaking on Wednesday, July 22nd at the Out East Summit hosted by @TheTieIO.
He'll be discussing whether “Crypto is Running Out of New Buyers, or New Narratives”

Ivan Miskovic retweeted
The number of noisy qubits needed to break RSA has fallen from 20 million in 2019 to under one million today.
Professor @jenseisert, co-author of "Mind the Gaps" with John Preskill, sits down with @ivanmiskovic to explain why on our latest episode.
Ivan Miskovic retweeted
Quantum joins @TheTieIO's Out East Summit next week as one of the summit's partners.
Co-founders @ivanmiskovic and @ledgersaur will be on Long Island's North Fork, July 20 to 22 joining 300 executives from the world's leading institutional digital asset firms.
If you're attending, let's connect.

Ivan Miskovic retweeted
7 million BTC, a third of the supply, are already exposed to a future quantum attack. The public keys sit exposed on-chain and cannot be re-hidden.
Nothing stands between them and an attacker except the absence of a capable machine.
Here's the breakdown:
quantum.systems/blog/how-man…

Ivan Miskovic retweeted
2028 is the target for Libra, @QueraComputing's first fault-tolerant quantum computer on AWS.
256 logical qubits, with a 1,000+ qubit system behind it. It won't break ECDSA yet, but the gap is closing from both sides.
Read the breakdown of the roadmap, and what it means for institutions:
quantum.systems/blog/quera-r…

Ivan Miskovic retweeted

Are you enjoying the show? Refill your popcorn... you’ll love this next part. 🍿
AMERICAN (Q)UANTUM DOMINANCE

Ivan Miskovic retweeted
Our engineer, @rubenmarcus_dev is #1 on ECDSA.fail, the Eigen Labs benchmark for the quantum circuit that breaks elliptic curve cryptography.
He took the top spot earlier today, then beat his own score with a second consecutive #1 submission.
He is driving an autonomous research loop to build a circuit of 1,404,146 Toffoli gates on 1,211 qubits.
That is a score of 1.70 billion, 43% below Google's best private design and first among 85 solvers and 313 promoted submissions.
Congratulations, Ruben.

A CLAUDE FABLE 5 USER IS NOW AT THE TOP OF THE ECDSA(.)FAIL LEADERBOARD
@BitW0nka's latest submission pushes the frontier to 41.0% ahead of Google’s classified circuit.
The frontier is moving in public.

Ivan Miskovic retweeted
On June 17, we're hosting a live panel on quantum computing and what it actually means for crypto.
Three panelists, three different angles on what to do about it:
@tamirhemo from @SuccinctLabs
@ivanmiskovic from @QuantumFDN
@bmartins_ from @Algorand
Moderated by our CSO @sgheb
Set your reminders.
June 17 | 12-1pm ET.
