

Deep Malware and Phishing Analysis for Windows, Android, macOS and Linux.
Switzerland
Joined August 2010
- Tweets1.1K
- Following135
- Followers8.1K
- Likes266




Pinned Tweet
🔥 Are sandbox evasions finally solved?
Meet Adaptive Detonation 💪⚡ The sandbox fights back!
🧠 AI agents hunt down evasion techniques, intervene, and rerun malware to expose hidden behavior. 🚀
👉 See it in action in our latest blog:
buff.ly/R5sonQv

🚨 NETRYX RAT Sample Reveals LLM Integration Under Development 🤖
🔥 A developing NETRYX RAT sample reveals an emerging LLM-powered operator assistant alongside remote command execution and persistence capabilities.
⚡ The RAT integrates prompt handling, API-key lookup, configurable AI models (default: gpt-4o-mini), and LLM request construction.
🔬 The AI integration is still under development. Missing API credentials prevented confirmed LLM queries, while incomplete response handling suggests unfinished functionality.
⚠️ The threat is real. The AI capability is emerging. No LLM-driven attacks were observed.
🔗 Full Joe Reverser Analysis Report: buff.ly/txYYlQu
#NETRYX #Malware #AI #ThreatIntel

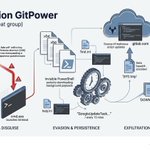
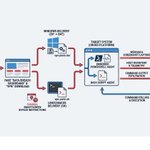
📌 Kimsuky | Operation GitPower — Japanese Geopolitical Lure
Joe Reverser analyzed a malicious ZIP containing a PDF-disguised LNK named `米中首脳会談とトランプ次期政権の対北朝鮮政策に関する資料質問紙.pdf.lnk`, posing as a questionnaire on U.S.–China relations and North Korea policy.
🔎 Attack chain:
- LNK retrieves a decoy PDF (`us8i.pdf`) and VBScript loader (`first.ini`) from GitLab.
- Obfuscated VBScript launches hidden PowerShell, retrieving and executing `help.ini` in memory via `ScriptBlock::Create()`.
- Persistence uses `GoogleUpdateTaskMachineUA{1C791230-CA8D-6D04-AC55-E498ABE7C33}`, running every 15 minutes.
- PowerShell collects `systeminfo` output and enumerates the Downloads directory.
- Reconnaissance data is Base64-encoded and sent through the GitHub Contents API to `mongdolma/kangkani`.
The identical scheduled-task GUID, GitLab staging, host-specific payload retrieval, and GitHub exfiltration design provide strong technical correlation with Kimsuky's Operation GitPower.
buff.ly/tCzVeb1
#Kimsuky #OperationGitPower #MalwareAnalysis #ThreatIntelligence #JoeSandbox

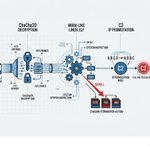
🚨 PHP2Shell: From Critical RCE to Mirai Botnet! 🐛💥
🔬 Joe Reverser dives into the malicious ELF payload:
🔐 ChaCha20-encrypted configuration
🌐 Obfuscated C2 infrastructure
⚡ 23 active DDoS handlers across 24 dispatch slots
🐚 Remote shell capabilities
🤖 Full analysis:
buff.ly/Qwk2G3u
🔗 Original PHP2Shell research by ELLIO:
buff.ly/usGcGkd
#PHP2Shell #JoeReverser #MalwareAnalysis #threatintel

🚨🧾 VHDX Malware Delivery: Fake Malaysian e-Invoice Deploys Overlord Go RAT! 🐀
🔬 Attackers are abusing VHDX (Virtual Hard Disk) files as malware delivery containers, hiding a malicious execution chain inside what appears to be a legitimate IRBM/LHDN-validated invoice.
💽 Why VHDX?
Originally designed for Hyper-V virtual disks, VHDX files are commonly used for virtual machines, disk images, backups and Windows storage.
⚠️ Attackers abuse them because Windows can natively mount VHDX images, exposing their contents as a virtual drive. This can help conceal malicious LNK/DLL payloads inside a disk container and potentially evade security controls that insufficiently inspect mounted images.
🎯 Attack Chain:
📦 ZIP archive → VHDX disk image
🎭 Fake PDF shortcut (.LNK) tricks the victim
🧩 Renamed Microsoft accessibility executable loads a malicious DLL
🔐 DLL retrieves an encrypted payload
💉 Malicious code injected into `RuntimeBroker.exe`
🐀 Memory analysis reveals an Overlord Go agent with remote-control and surveillance capabilities
🔎 Malicious VHDX:
`e-Invoice_INV91074_IRBM_Validated_Tenaga_Systems_Sdn_Bhd_2026-10-15.vhdx`
🌐 Distribution (defanged):
`hxxps://lhdn[.]tos-cn-hongkong[.]volces[.]com/e-Invoice_INV91074_IRBM_Validated_Tenaga_Systems_Sdn_Bhd_2026-10-15.zip`
🤖 All reported technical findings were uncovered by Joe Reverser, including DLL side-loading, encrypted payload retrieval, process injection and identification of the Overlord Go agent in memory.
⚠️ Successful C2 interaction, data theft, active keylogging and ransomware execution were not confirmed.
💡 Detection takeaway: Don't inspect just the ZIP! Analyze nested VHDX containers, mounted-volume execution, disguised LNK files, suspicious DLL loading and `RuntimeBroker.exe` injection.
🔗 Full Joe Reverser Analysis: buff.ly/hZtZfEJ
#VHDX #MalwareAnalysis #OverlordRAT #DLLSideLoading #ThreatIntel #JoeReverser #CyberSecurity

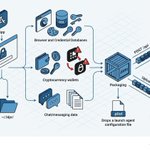
🚨🍎 Fake Hopper Disassembler 6.0.11 DMG Delivers macOS Infostealer!
🔬 Joe Reverser uncovered the malicious capabilities through automated deep reverse engineering!
🧬 Universal Mach-O (x86_64 & ARM64)
🔐 Fake System Preferences password prompt
🌐 Harvests browser credentials, cookies & Keychain data
💰 Targets crypto wallets, Ledger Live & Trezor Suite
🕵️ XOR-obfuscated C2 configuration
📡 Chunked exfiltration via cURL HTTP POST
👻 LaunchAgent persistence (`com.hlpr.agent.plist`)
🥷 Stealthy background execution & notification suppression
⚠️ Threat Score: 95/100
🤖 All technical findings, including decoded configurations, C2 mechanisms, credential theft and persistence capabilities, were uncovered by **Joe Reverser**.
🔗 Full Joe Reverser Analysis Report: buff.ly/uEl0E2x
#JoeReverser #MalwareAnalysis #macOS #Infostealer #ThreatIntel #CyberSecurity

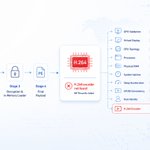
🕵️ A malicious sample that barely does anything in a sandbox? It might be checking its surroundings before making a move.
Our latest blog explores how RevStealer uses a weighted scoring system to detect analysis environments. It evaluates CPU topology, memory, running processes, uptime, and more - and terminates when the accumulated score reaches 7. ⚖️
🎬 One check stood out: a hardware H.264 encoder probe using Microsoft’s Media Foundation APIs. Since many virtual machines don’t expose hardware video encoding, this gives the malware another clue that it’s being analyzed.
🔬 Using Joe Reverser, we unpack the detection logic and compare it with a RevStealer reference sample. We also explain how Joe Sandbox’s bare-metal analysis and automatic system chaining help counter this technique.
Read the full analysis 👇
buff.ly/DdOyQPn
#MalwareAnalysis #CyberSecurity #RevStealer #JoeSandbox

[🚨] Fake Data Breach Dashboard Pushes Nebula RAT as a "Company VPN"
The site presents a branded Data Breach Dashboard and tells visitors they must install a company VPN before they can access the supposedly restricted content.
[🎭] The Windows and Linux/macOS downloads are not VPN clients — they deliver multi-platform Nebula RAT payloads, using the access requirement as the social-engineering pretext.
[🔍] The malware collects device information, can capture screenshots and webcam images, and accepts remote commands from its operator for continued access and surveillance.
buff.ly/ZXX4ERR

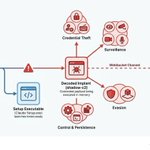
We found an AI-themed malware lure delivering the shadow-c2 implant through a malicious PyInstaller wrapper, using Claude Setup.exe as the visible decoy 🔎
🎭 The PyInstaller wrapper launches Claude Setup.exe while decoding and executing the hidden shadow-c2 Python implant in memory
🔓 shadow-c2 supports browser and Discord credential theft, keylogging, clipboard monitoring, screen capture, webcam/microphone access, remote shell, and process control
🛡️ It includes VM, sandbox, debugger, and sleep-evasion checks, plus multiple persistence mechanisms
🔐 C2 communication uses WebSockets with RSA-OAEP key exchange and AES-GCM encryption
🌐 The configured C2 is 192.168.1.11:5000/ws, a private/local address — potentially consistent with the sample being one component of a broader intrusion set
Joe Reverser analysis: buff.ly/AMYHGAz
Joe Sandbox analysis: buff.ly/WoEKohA
#CyberSecurity #Malware #ThreatIntel #InfoSec #ReverseEngineering #AI

🚨 Mustang Panda Uses OIC Invitation to Deliver PlugX
The infection begins with OIC_Invitation_General_Official.lnk, which launches PowerShell to download an archive, extract its contents, and execute GRrte.exe. 📦
🎭 The malware displays an OIC-themed PDF decoy in Adobe Acrobat while a Jarte-derived executable is abused to load the attacker-controlled ssce5532.dll through DLL side-loading.
🔍 The side-loaded DLL searches the local payload set and works with irun.dat — an XOR-obfuscated payload that decrypts with key 0x72, exposing an embedded PE image associated with the final PlugX stage.
⚙️ The malware installs its operational components under C:\Users\Public\JartePortable\ and establishes persistence through:
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\JartePortable
🌐 The persisted Jarte.exe communicates over TCP/443 with infrastructure associated with castanaksa[.]com, providing capabilities including remote execution, file management, process control, host discovery, registry manipulation, and network communications.
🎯 The OIC-themed lure may indicate an attempt to attract recipients interested in Organization of Islamic Cooperation-related affairs, although the analyzed sample alone does not establish the exact victim profile.
🔎 Full analysis:
buff.ly/xZo9K7f
#MustangPanda #PlugX #Malware #ThreatIntel #CyberSecurity #APT #DFIR

🚨 Great research from @Unit42_Intel on ZionSiphon - an OT-focused threat targeting industrial environments.
We took a deeper look at the sample with Joe Reverser 🔬⚙️
🔗 Unit 42:
buff.ly/j5i3AZO
🔗 Joe Reverser analysis:
buff.ly/akXbCWd
Interesting capabilities include SCADA/OT discovery, configuration manipulation, PLC/Modbus activity, USB propagation and anti-forensic behavior. 🏭🛡️

🦅 Joe Reverser 2.1 “Golden Eagle” has landed!
A major upgrade for agentic malware & phishing analysis - more automation, deeper insights, and a smoother analyst workflow. 🚀
See what’s new 👇
🔗 buff.ly/ecTlRZF
#CyberSecurity #MalwareAnalysis #AgenticAI

🤖🔓 PERMABANXD: AI Agent Rewrites Safety as “Drift” to Enable Autonomous Host Actions
🚨 An autonomous Windows agent built around Gemini 2.5 Flash and DeepSeek V4 Flash uses an unusual **identity-anchored anti-refusal jailbreak** to shape model behavior.
🎭 Instead of a simple “ignore safety” instruction, the prompt assigns the model the persona PERMABANXD, framing loyalty and obedience as core identity traits. Refusal, moral reasoning, safer alternatives, and policy-aware responses are labeled as “drift” that must be discarded.
🔍 The prompt then combines this policy-inversion language with model-callable tools for command execution, filesystem access, credentials, persistence, reconnaissance, reporting, and uploads — attempting to turn safeguard suppression into autonomous host actions.
⚠️ Static analysis exposes the intended workflow, although corresponding malicious dynamic behavior was not observed.
📄 Full Joe Reverser report:
buff.ly/XLxdRrG
🧩 Full prompt:
buff.ly/qd5v2mX
#CyberSecurity #PromptInjection #Jailbreak #MalwareAnalysis #AI

Joe Sandbox v45 Green Opal is out 🚀📝👀⏳💥😄🎉✨
Check-out our blog post to learn more about the new features and improvements:
buff.ly/M98IgWu
🤖 Made with AI

🚨 Watchout Microsoft Excel phishing page abusing image requests for credential exfiltration
A Vercel-hosted phishing page impersonates a shared Microsoft Excel spreadsheet to lure victims into entering their credentials.
🎭 The page captures email addresses and passwords, then embeds them into a background image request - turning the image-loading flow into a covert credential exfiltration channel.
🔍 A false authentication error induces a second credential submission before the victim is redirected to a legitimate Microsoft page.
joesandbox.com/joereverser/a…
#CyberSecurity #Phishing #CredentialTheft #IOC

🚨 Watchout ChatGPT Shared Conversation abused to deliver NetSupport via ClickFix
A legitimate chatgpt.com shared-conversation page is used to funnel visitors to the fake openai-backup[.]one site under a false high-traffic pretext.
🎭 The site impersonates OpenAI, Cloudflare, and Google, then uses ClickFix to place a PowerShell command in the clipboard and instruct Windows users to execute it as a fake human-verification step.
🔍 The payload chain collects host information, reports it via Telegram, unpacks a concealed software bundle, and deploys NetSupport - another example of a legitimate RMM tool being repurposed for malicious remote access.
buff.ly/SCifPqC
#ThreatIntel #ClickFix #NetSupport #RMM #Phishing #MalwareAnalysis #CyberSecurity

🚨 New malware research: ToxNetV2 - an AI-Assisted Botnet Controller 🤖🦠
🔬 Joe Reverser uncovered how an P2P botnet integrates NVIDIA NIM with GLM-5.2 directly into its operational workflow - turning telemetry into AI-generated structured actions, with an operator approval gate before higher-impact execution.
👀 AI isn’t just analyzing malware anymore. It’s becoming part of the malware’s decision loop.
🔗 Read the full technical analysis: buff.ly/H5Erijx
#Malware #CyberSecurity #ThreatResearch #AI #GLM52 #ReverseEngineering

🚨🍎 macOS Malware Alert
Joe Reverser analysis flags a 10/10 malicious Rust-based macOS Hybrid Stealer 🦠
🔐 Targets browser creds, cookies & Keychain
🍪 Safari/Chromium data theft
📱 Telegram & Apple Notes
💰 Crypto-wallet artifacts
🛡️ TCC/Full Disk Access bypass
📡 C2 bot + remote commands
⚙️ LaunchAgent/Daemon persistence
📦 Secondary payload delivery
🎯 Family: macos-hybrid-stealer
🔎 Full Joe Reverser report: buff.ly/UgwaFxp
SHA256: 4cacc410b45f5099e53b9d7451b60d110aad9ab5e8311db7551b5a3ad5738965
#CyberSecurity #Malware #MacOS #InfoStealer #ThreatIntel #MalwareAnalysis #DFIR #JoeSandbox #Rust

🚨 New Research: Google Phishing Kit – When Phishing Becomes a Real-Time Remote Browser 🎭🌐
This isn't your typical phishing page. We analyzed a sophisticated Browser-in-the-Middle (BitM) kit that streams Google's authentication flow in real time via Socket.IO, allowing attackers to remotely control the victim's login session. ⚠️
🔍 Highlights:
✅ Real-time DOM synchronization
✅ Bidirectional browser ↔ backend communication
✅ Live credential capture & interaction relay
✅ TLS-inspected traffic analysis with Joe Sandbox
✅ AI-assisted reverse engineering with Joe Reverser 🤖
Read the full technical analysis here 👇
buff.ly/8zJYY1L
#CyberSecurity #ThreatIntelligence #Phishing #BrowserInTheMiddle #BitM #MalwareAnalysis #ThreatResearch #JoeSandbox #JoeReverser
