

Deep Malware and Phishing Analysis for Windows, Android, macOS and Linux.
Switzerland
Joined August 2010
- Tweets1.1K
- Following135
- Followers8.1K
- Likes266




Joe Security retweeted

Honestly people underestimate just how on the ball Joe Sandbox is as a sandbox solution. I have had so many arguments with people who think Random sandbox X us better cause their owned by some big name vendor.
But Joe sandbox out here being the industry leader for the last half a decade. 🫡
Joe Security retweeted

Nice automated post from our InQuest Labs "Special Operations". Embedded IOC was extracted via Deep File Inspection. Referencing document was automatically retrieved, analyzed, and labeled malicious via ML. @joe4security detonation of the EXE payload:
joesandbox.com/analysis/6285…


🤖 Potentially malicious Office document found hosted at:
http///ajoa.org/home/error/tmp/favicon[.]dotm
SHA256: 2008668fb16aa47ed52aace07ea7a82f5ed67bad2220159007160b1420c06fda
IOC extracted from sample: labs.inquest.net/dfi/hash/9e…
(Automated Tweet, maybe a FP)
Joe Security retweeted

Thanks to @JCyberSec_ we know that they reply back with a link to an encrypted zip > exe = #GuLoader > #Remcos probable C2s /top.nobullshyt1.xyz /sub.nobullshyt2.xyz 64.42.179.67
Very evasive, only @joe4security physical machine got it to run 💪 joesandbox.com/analysis/5687…


Pretty interesting double barrel #phishing campaign. Curios where this will lead.
Reply-to: [email protected]

Joe Security retweeted
A walkthrough of the analysis of a #Remcos RAT #maldoc
Always wondering if the folks at @Chase, @BankofAmerica, and other financial institutions are tracking the misuse of their branding?
inquest.net/blog/2022/01/24/…
#malware #threatintel


Joe Security retweeted
Why you need #EmailSecurity! .msg targeting @eastmarineasia with a weaponized .ppam pushing #lokibot. Email chain has some spoofed branding from the @sporeMOH
InQuest Labs: labs.inquest.net/dfi/sha256/…
@JoeSandbox: joesandbox.com/analysis/8814…
@RedBeardIOCs
@pr0xylife
@James_inthe_box


Joe Security retweeted

#MalwareChallenge
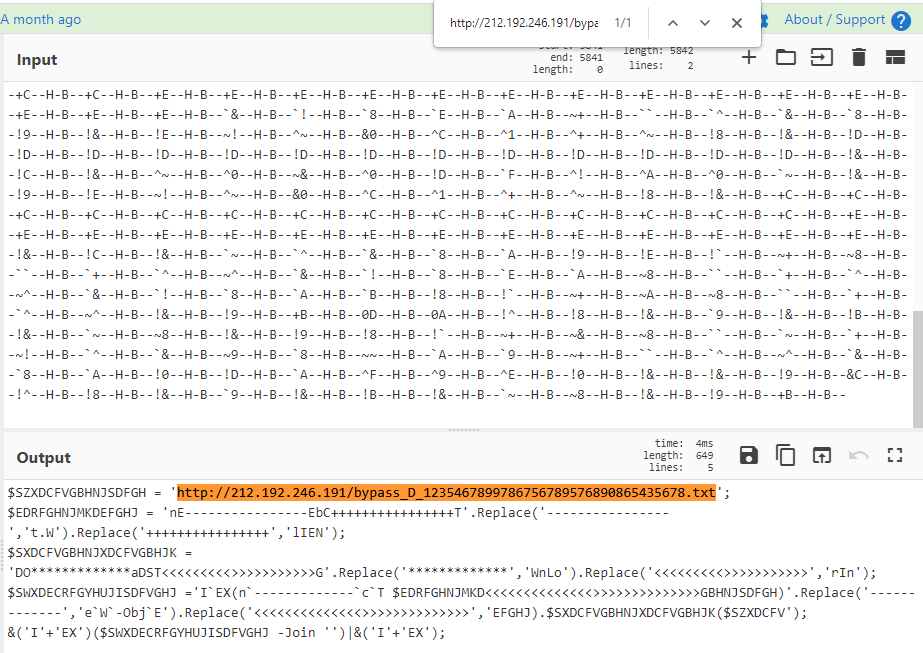
Fairly interesting infection chain for this #Remcos #malware
@joe4security report:
➡️joesandbox.com/analysis/4985…
@abuse_ch Bazaar sample:
➡️bazaar.abuse.ch/sample/b9c5a…
➡️C2: Officialsw.chickenkiller[.]com (+2)
Just started researching, maybe continue thread later...



Joe Security retweeted

Geofenced German malspam #squirrelwaffle (DATOP loader) downloading and running the dll via regsvr, injecting into explorer and adding itself to MS exclude path.
Finally leading to CobaltStrike C2 /tuxsecuritybiness.com
Latin malzip URL has 1/89 VT
bazaar.abuse.ch/sample/29155…

Joe Security retweeted
Payload is 104 MB so it is understandable some AVs will skip this for performance . Never the less any bitwise xor at runtime (-bxor) switch via PowerShell should be treated with some suspicion.
joesandbox.com/analysis/4834…
cc @joe4security thanks for sandboxing these big files..


A new version of Jupyter infostealer #malware is being distributed via MSI installer 'to become more efficient and evasive.'
Read details: thehackernews.com/2021/09/a-…
#infosec #cybersecurity #hacking
Joe Security retweeted

Another #IOC-Based free #Sigma which included this behavior. @RedDrip7 nice find! this also tracked by @joe4security sandbox.
➡️tdm.socprime.com/tdm/info/vz…
+ one more #ThreatHunting rule available by tag: ➡️tdm.socprime.com/?tagsCustom…
#vulnerabilities #APT #CVE-2021-40444 #Microsoft


Maybe it is the latest #CVE-2021-40444 attack sample, which only requires one click to run.
And our researchers have reproduced the exploit.


Joe Security retweeted
Wow, this #Remcos #malware sample is really sneaky -- it's trying so hard to hide what it is 😂😂
joesandbox.com/analysis/4764…


Joe Security retweeted

thanks to @joe4security i managed to identify the behaviour of this guloader
joesandbox.com/analysis/4485…
enjoy
@James_inthe_box
sample mega.nz/file/0i530IDS#t1qQZY…
pass:infected


Joe Security retweeted

All the #KaseyaVSA fun... Ripped out all the domains from the config at joesandbox.com/analysis/4437… (pastebin.com/3yHNbbkh) and keeping fingers crossed. #ransomware #infosec #malware
Joe Security retweeted

A Turla Javascript backdoor? Hellllo! Hit VT 2 hours ago. @joe4security sandbox: joesandbox.com/analysis/3335…
Source: ghostbin.com/paste/p86wd


Joe Security retweeted

We would like to thank our Virtual Booth Sponsors @ArcticSecurity @FarsightSecInc @joe4security for supporting #FIRSTCON20 November 16-18!
first.org/conference/2020/sp…
Joe Security retweeted
Watch @joe4security tear up this 2/57 Excel doc with hidden 4.0 macros.
JoeSandbox Report: jbxcloud.joesecurity.org/ana…
View the macro at InQuest Labs:
labs.inquest.net/dfi/sha256/…
IOC: hxxps://jawadsarwary[.]com/wp-keys.php
#maldoc #ThreatIntel

Joe Security retweeted
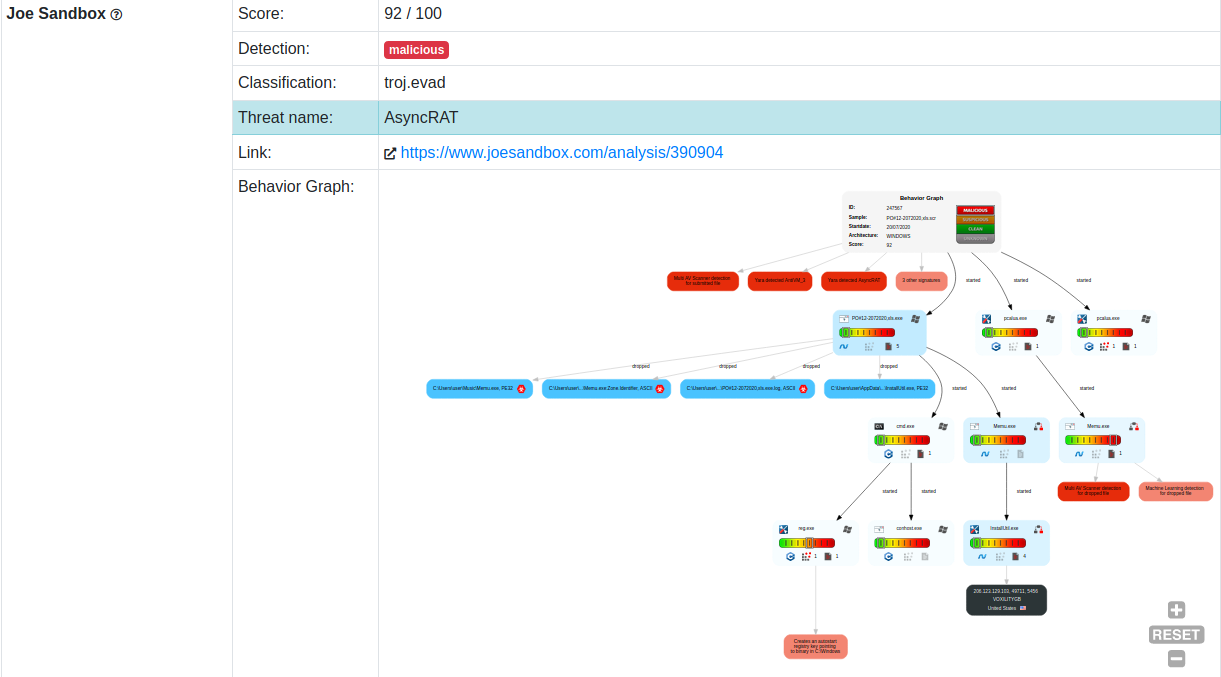
I've promised more awesome features for #MalwareBazaar, and there you go:
MalwareBazaar now integrates Joe Sandbox - including its zoomable behaviour graph! 😱 Special thanks to @joe4security for making the integration possible 👏❤️💪
Sample report:
bazaar.abuse.ch/sample/f801a…
Joe Security retweeted
Today, the community service is brought to you thanks to our corporate sponsors. I'm happy to announce that Joe Security is our newest sponsor. Joe Security offer an in-depth malware analysis sandbox, either on-prem or in the cloud. Check them out: joesecurity.org/

Joe Security retweeted

Once again a beautiful presentation slide deck by @cyb3rops at #EUATTACKworkshop
@MITREattack web.tresorit.com/l/lN841#uqb… also congrats to @joe4security for integrating #sigma #threatintel

Joe Security retweeted
Excited to announce that @InQuest has formed an exclusive partnership with @joe4security to deliver Joe Sandbox to the US Public Sector!
Unleash the power of deep malware analysis to your CERT, CIRT, SOC or IR team!
businesswire.com/news/home/2…
#malware #threathunting
