

Documentation is lies. Source is an abstraction. Assembly is the truth. Also at https://xitter.cf/t.co/VYFZ0HHnQn and nostr npub10mx0gx3r2lszrrut8kvr5mt2m8r9ffhn
Joined May 2010
- Tweets8.1K
- Following1.7K
- Followers6.9K
- Likes82.5K
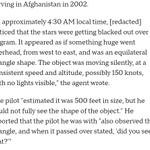





That, sir, is not an equilateral triangle. Though it might be isosceles, I dare say it is even a right triangle. Aliens or not, we will have radial symmetry in our art!


Or trail of bits 😥🌎🌳🐿️♥️💚
xitter.cf/sickcodes/status/21139…

Found an Updater.exe attempting to connect to a domain that wasn’t registered anymore. 3.8 million unique client IDs.
"All we needed to do was supply a link to an executable and the program would download it and then execute it with high privileges"
labs.eye.security/operation-…
scriptjunkie (Matt) retweeted

Update: Our PHP exploit is now production-grade.
* stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load
* ARM64 + x86-64 targets
* MediaWiki, WordPress, phpBB, Laravel
* Apache/mod_php and nginx/php-fpm -> root
xitter.cf/dguido/status/21131291…

Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
eliastaylor.com/noexploit/

scriptjunkie (Matt) retweeted

Good morning
045fa83b7c7a42dba1acb2c19794c1bf1091c448eb9c483503e8f8e110fcec42
github.com/kubernetes/kubern…


I am outraged, I tell you
xitter.cf/_0xKiwi/status/2113309…


UK 1815-1914: Peak British empire influence
1920: Peak territory, covering 1/4 of earth
1947-1997: Decolonization and empire decline
2026: "Ahem: But we just passed a law declaring ourselves ruler of the world so now we own all of it."
xitter.cf/AlecMuffett/status/211…

#Ofcom chief:
"We do not believe that the [Online Safety] Act gives us that extraterritorial jurisdiction. I am not quite sure how you can carry that out."
Absolute deceptive bullshit.
They have flatly, overtly and flagrantly been harassing foreign websites on those grounds:

scriptjunkie (Matt) retweeted
The E.U. wants to punish people for their speech—without even a trial.
buff.ly/pFNYEhJ

scriptjunkie (Matt) retweeted

‼️ Palo Alto firewall VMs and Citrix NetScaler run without ASLR, a basic memory defence, Kevin Beaumont says.
He warns that makes the PHP2Shell flaws trivial to exploit through internet-facing management interfaces.
Neither has a patch out. Citrix promises one on 27 October.


scriptjunkie (Matt) retweeted

A schoolteacher responds to Parliament's Online Safety Act Inquiry. He writes that it has made "literally no difference" to safety, censored the Internet for adults, "terrible" for user privacy, and is easily circumvented - by children - with no effort.
committees.parliament.uk/wri…


scriptjunkie (Matt) retweeted
The actual prompt for this was "let's look for pre-auth RCEs in PHP". I'm sharing this so people know this stuff is real and to take agent-assisted scanning seriously.
I kicked if off using Claude Mythos 5.1 (in stock Claude Code) but it uses a skill to drive a harness we built over the last few months.
I don't know if the harness is amazing, but it certainly has a scary track record so far. It's setup to do an agent guided tree search across a codebase, and runs in microvm sandboxes that all have the full source code for the target, as well as the source for any transitive dependencies.
When I built the harness I basically just fed Claude a bunch of Project Zero blog posts describing how they did research and had it build a harness that ran like that, but on our tech stack.
The first phase is just setup and can run with any model, it just does that fetching and assembles the kit environment, and gets a target up and running alongside the source code.
Then we just do some basic suspend/resume stuff over to the hunt phase, where one agent supervises the tree, and the first node kicks off.
Each node is context-aware and aware of the work of all the others. I think I ran this with parallelism 4? So 4 running at any one time. The supervisor can shape the tree and boost nodes or prune. Any node can add more below it with targeted instructions.
A typical run looks like the first node doing a codebase review or building and running a fuzzer or something, all depending on the target. Then based on whatever it finds, it'll queue 4-5 children that go look into those areas. The main system guidance is to validate everything 3 times in clean VMs, and we typically require full exploit chains/POCs.
Here's what this run looked like.
We're doing this with a bunch of other open source projects now and companies. We're doing a lot of this for free, even with private companies, across critical infrastructure. We're directly partnered with Anthropic, and can do this even if you don't have direct access to a frontier model yourself.


scriptjunkie (Matt) retweeted

lol
Expert For News Orgs Suing OpenAI Warned ‘Always Verify’ AI, Then Didn’t Verify His AI-Made Charts In His Expert Report

scriptjunkie (Matt) retweeted

You've gotta patch your dependencies super fast because they're full of vulns (PHP, Node, eMudhra, etc), but not _too_ fast because they're full of backdoors (LiteLLM). Good luck!
scriptjunkie (Matt) retweeted

GitLab is having a bad day as well:
thehackernews.com/2026/10/cr…


LinkedIn is going to go INSANE on Thanksgiving when the leading researchers posting there find out about PHP
xitter.cf/ZackKorman/status/2112…

scriptjunkie (Matt) retweeted
Just use memory safe Fil-C compiled PHP. It's not going to be fast, but PHP never was.
xitter.cf/meekaale/status/211290…

memory safe PHP 8.4.25 built with Fil-C as Docker images (compatible with official php images) and as a single relocatable directory for Linux that doesn’t depend on any system libraries
github.com/mbrock/filnix/rel…
