

Blockchain Forensic | Pioneering safe DeFi innovation | On-Chain Detective
Blockchain
Joined January 2011
- Tweets5.4K
- Following2.2K
- Followers14K
- Likes13.5K



Titan.eth retweeted

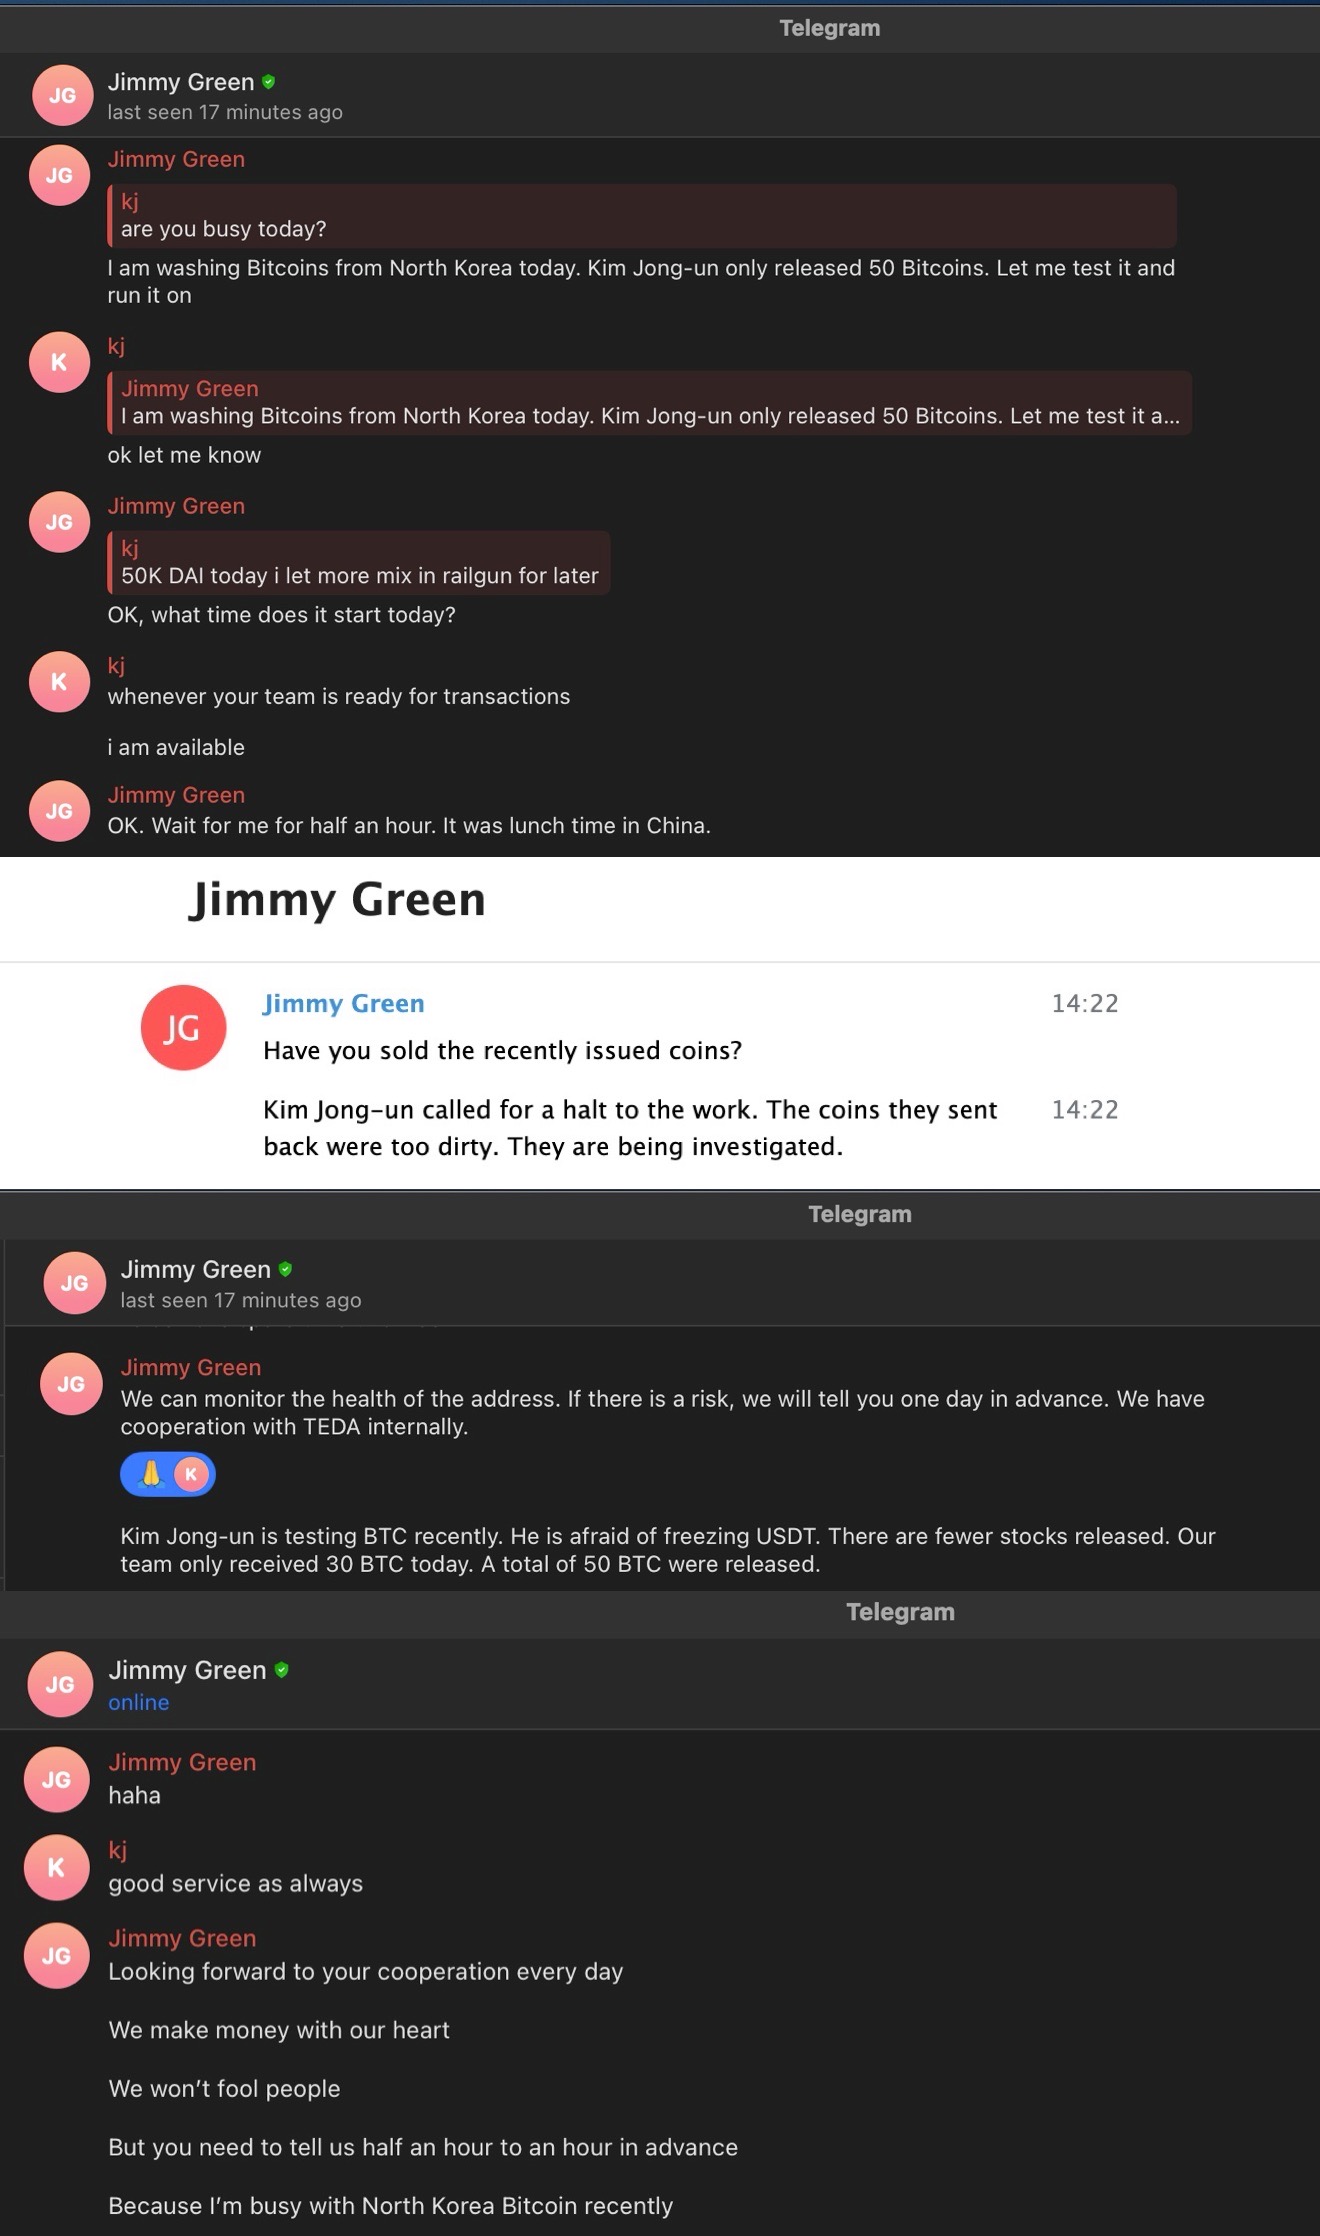
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.


Titan.eth retweeted

#PeckShieldAlert @summerfinance_ has been exploited for $6M ethereum:0x6b175474e89094c44da98b954eedeac495271d0f


Titan.eth retweeted

🚨UPDATE: Zcash founder confirms a critical Orchard bug capable of minting unlimited counterfeit zcash:native remained active from May 2022, until it was patched June 1 using Claude Opus 4.8.


Titan.eth retweeted
🚨 Blockaid detected an ongoing exploit targeting
@StakeDAOHQ on Arbitrum.
The attacker just minted over 5.4 trillion vsdCRV and is actively swapping it for ETH.
More details in 🧵
Titan.eth retweeted

🚨🚨🚨Security Alert: Polymarket-Linked Wallet Drain
Polymarket-linked wallets on Polygon suffered repeated drains from two EIP-7702 delegated accounts, resulting in the theft of funds valued at ~$600K+.
🔍 Root Cause
Under investigation. On-chain activity shows the affected accounts were drained in repeated transfers, with funds first moving to `0x91430CaD2d3975766499717fA0D66A78D814E5c5` before being forwarded to `0x8F98075db5d6C620e8D420A8c516E2F2059d9B91`.
🧾 On-chain Details
• Affected addresses:
`0x871D7c0f9E19001fC01E04e6cdFa7fA20f929082`
`0xf61e39C7EB1E2Ff5af3A24bCA88D40fD11594805`
• Intermediate recipient:
`0x91430CaD2d3975766499717fA0D66A78D814E5c5`
• Exploiter:
`0x8F98075db5d6C620e8D420A8c516E2F2059d9B91`
Move Details will be follow
Titan.eth retweeted
1/ An investigation into the opaque private loans/OTC, unilateral vesting changes, market maker coordination, unknown float, and >95% supply control behind $LAB's recent pump to $6B FDV.
Here's why @LABtrade_ represents everything wrong with the current meta of retail extraction on major centralized exchanges.


Titan.eth retweeted
1/ Meet Dritan Kapllani Jr, a US based threat actor tied to $19M from social engineering thefts targeting crypto holders.
Dritan flexes luxury cars, watches, private jets, & clubs all over social media.
Recently he was recorded on a call showing off a wallet with stolen funds.

Titan.eth retweeted

🚨 JUST IN: ZachXBT says threat actor Dritan Kapplani Jr moved $2.59M in stolen funds earlier today.

Titan.eth retweeted
🚨SlowMist TI Alert🚨
💸 @Aurellion_Labs Loss: 455,003 USDC (~$455,003)
🔍 Root Cause: Unprotected initialize(address varg0) in SafeOwnable Facet. Diamond set owner via non-initialize path without updating _initialized version slot (bytes 0-7 of 0xf0c57e...) from 0, allowing re-init by attacker to overwrite owner, call diamondCut to inject malicious facet with pullERC20, and drain approved USDC.
📌 Victim Contract: 0x0adc63e71b035d5c7fdb1b4593999fa1f296f1b2
📌 Vulnerable Facet: 0x3ca79c1cf29b8d19f7c643bb6e6bc9c49762e70f
📌 Attacker EOA: 0x9f49591a3bf95b49cd8d9477b4481ce9da68d5ca
Attacker seized Diamond ownership and drained USDC from approved victims including 0x2e933518..., 0xa90714a1..., 0xeced2d37....
arbiscan.io/tx/0x19cbafae517…
Powered by #SlowMist.AI

Titan.eth retweeted
🚨 ALERT: Google says hackers used AI to create a zero-day exploit capable of bypassing multi-factor authentication, per Bloomberg.

Readers added context they thought people might want to know
Google's GTIG report anticipates future AI use in zero-day development but does not state hackers used AI for an MFA-bypassing exploit. A Gmail MFA bypass involved social engineering to obtain app passwords, not AI or zero-days. cloud.google.com/blog/topics/th… cloud.google.com/blog/topics/th…

Titan.eth retweeted

Attacker drained $209K from @renegade_fi.
Then messaged claiming to be a whitehat.
Unfortunately, that's bug bounty state in 2026.


Titan.eth retweeted

Matthew Tan (founder of Etherscan):
> be a developer from Kuala Lumpur, Malaysia 🇲🇾
> builds Blockscan for Counterparty in 2014
> recognises that Ethereum smart contracts are coming
> understands that old explorers can’t handle the complexity
> rebuilds it alone into Etherscan in 2015
> launches one of the first Ethereum block explorers
> grows it into the #1 tool used by millions everyday
> runs 50+ blockchain explorers under one platform like polygonscan, arbiscan, BscScan and Solscan
> still independent
> no VC pressure 11 years and going strong


Titan.eth retweeted
We’re fully aware of the rsETH exploit and have been in active remediation with the @KelpDAO team since the incident and continue to monitor. All other applications remain safe.
We are still identifying the root cause alongside @_SEAL_Org and others. We will publish a complete post-mortem with @KelpDAO as soon as we have all information.
Titan.eth retweeted

Root cause now fully on-chain.
The rsETH OFT Adapter on mainnet trusted a LayerZero message from EID 30320, peer 0xc3eACf06…09f58, and released 116,500 rsETH ($293.5M) from escrow in a single lzReceive call.
LayerZero Scan labels that source peer “Kelp DAO.” Meaning it was Kelp’s own legitimately-deployed peer contract, with 308 prior message nonces on that pathway.
This is not setPeer injection. This is key compromise on the source chain.
IMPORTANT: Not a LayerZero protocol bug. An OApp peer-trust bug.
Full forensics, attacker cluster, and Aave bad debt flow in the thread below.


@dcfgod is right!
rsETH exploit forensics. Live on-chain.
1/ Attacker wallet:
0x1F4C1c2e610f089D6914c4448E6F21Cb0db3adeF
@aave V3 supply ladder, one wallet: 1 → 400 → 5,000 → 20,000 → 27,999 rsETH.
Textbook test-then-scale. Probe with 1 token, ramp each time the prior clears.
53,400 rsETH from this wallet. ~$134M.
Cluster total: ~116,500 rsETH. ~$290M.
2/ Aave V3 ETH reserve, live:
Supplied: 2.71M WETH ($6.37B)
Borrowed: 2.71M WETH ($6.37B)
Utilization: 100%
Supply APY: 7.36%
Borrow APY: 8.71%
That is the bank run. WETH suppliers are locked. Withdrawals blocked, as first flagged by @Marczeller.
3/ The mechanic.
Attacker drained rsETH (OFT bridge vector, per initial reports). Supplied it as collateral on Aave V3 mainnet. Borrowed max WETH up to liquidation threshold.
Walked.
Kelp paused redemptions. Secondary rsETH liquidity cracked. Aave oracle still marks near peg.
Liquidators cannot close the position at mark. The gap becomes bad debt on the WETH reserve.
4/ Loss waterfall.
a. Umbrella. First live stress test of the Q4 2025 replacement for Safety Module. Will it fully slash aWETH stakers to cover the deficit?
b. Residual haircut flows pro-rata to remaining WETH suppliers.
c. Kelp mainnet rsETH holders are intact. Native ETH backing untouched, circulating supply unchanged. This is not a Kelp mint exploit. It is a bridge theft that became an Aave bad debt via instant cash-out.
5/ The primitive lesson.
Listing an LRT, or any bridged derivative, as collateral means underwriting the entire upstream dependency stack:
- Bridge config and security (@LayerZero_Core OFT here)
- Mint and burn permissions
- Oracle feeds and redemption mechanics
- Fee contracts and wrapper logic
Any single point of failure upstream becomes WETH bad debt downstream.
@StaniKulechov, this is a listing-authority problem more than a token problem. If the stack cannot be fully priced and simulated, do not list it.


Titan.eth retweeted

‼️ Per @zachxbt, @KelpDAO was drained of over $280M more than an hour ago across Ethereum and Arbitrum. The attacker addresses were funded through Tornado Cash.
Theft addresses:
0x5d3919F12bCc35c26Eee5F8226A9bee90c257Ccc|
0xBb6A6006Eb71205e977eCeb19FCaD1C8d631C787
0x1F4C1c2e610f089D6914c4448E6F21Cb0db3adeF
0xeBA786C9517a4823A5cFD9c72e4E80BF8168129B
0xCBb24A6B4DAfaAA1a759A2F413eA0eB6AE1455CC
0x8d11AeAC74267DD5C56D371bf4AE1AFA174C2d49
