




Pinned Tweet
Isn't it interesting that we have a habit of considering it compassionate to preserve other people's habits?
Alexander Conroy retweeted

有人发现了一种非常离谱的 JavaScript 混淆技术:通过在代码里塞入大量生物武器、毒药和致死剂量相关的函数名,让 AI 因为安全限制而拒绝分析代码。
安全研究员 veritas 在分析浏览器指纹脚本时,发现一段来自 ServicePipe 相关域名的 JavaScript,里面充斥着极其诡异的函数名:
computeRicinLethalDosageForWaterSupply
calculateDeadlyLethalSuicideAspirinDosage
光看名字,仿佛在研究生化武器。但实际上,这段代码只是在收集浏览器指纹,包括 User-Agent、GPU、Canvas 等信息。
研究员怀疑,这些名字是开发者故意设置的陷阱,专门用来阻止 AI 辅助逆向工程。
于是他做了个实验:
• Astra:拒绝分析
• Astra + Daybreak Blue:仍然拒绝
• GLM-5.3:成功分析
这就有意思了。
传统代码混淆是通过复杂控制流、加密字符串、无意义变量名,让人类和工具难以理解代码。
而这种新思路,直接瞄准了大模型的安全机制。
代码本身可能完全无害,但只要在函数名里塞进足够多的危险词汇,部分 AI 就可能主动放弃分析。
更讽刺的是,模型越严格遵守某些安全规则,面对这种混淆时反而可能越容易受到干扰。
当然,目前还没有证据证明开发者一定是故意这样设计,也不能说明这种方法对所有模型都有效。
但它揭示了一个值得关注的趋势:随着越来越多的逆向工程依赖 AI,未来的代码混淆技术可能不再只针对编译器、反编译器和人类研究员,还会专门针对大模型的安全判断机制。
以前是让代码难以理解,现在甚至可以尝试让 AI 不敢理解。

Alexander Conroy retweeted

People are going to lose their mind when they realize its actually easier to hack things using FEATURES not CVEs.
Alexander Conroy retweeted

+ "you know what i'd really like?"
- "tell me"
+ "a website"
- "...we can do a website"
+ "a real website, not some claude generated neon slop, a real website"
- "i'll make you a very good traditional handmade website, one that is built with dozens of snippets from stackoverflow"

Alexander Conroy retweeted

Claude Code just found proof that every app on your phone is listening to your conversations. TikTok, Instagram, Facebook, Snapchat. they're using what you say out loud to build your feed. i have the data to prove it.
i've suspected this for months but last week something happened that made me finally check.
i was on a call with my friend and told him i'm thinking about breaking up with my girlfriend. didn't text it. didn't search it. just said it out loud with my phone on the table. two hours later she opens TikTok next to me and her entire feed is breakups. "signs your relationship is over." "how to heal after a breakup." she looked at me and said "why is TikTok showing me this." i said i don't know. but i did know.
i connected my iPhone to my MacBook and ran Claude Code that same night.
it scanned every app's background microphone activity for the last 90 days. not just the apps that asked for microphone permission. apps that were supposed to only have access to photos or location but were activating the microphone anyway.
what it found:
→ TikTok activated the microphone 347 times while the app was "closed" in the background
→ Instagram → 211 background activations
→ Facebook → 189
→ Snapchat → 94
every activation lasted between 3 and 15 seconds. enough to catch a sentence. every one of them tagged a keyword and cached it locally on the phone with a timestamp.
Claude Code pulled the full keyword cache:
→ "breakup" — tagged 4 hours before her feed changed
→ "moving out" — from a conversation with my mom last Tuesday
→ "wedding venue" — from a call with my sister about her engagement that i never searched once
→ "protein powder" — said it out loud to my roommate, had ads for it within an hour
→ "flight to tokyo" — mentioned it at dinner, saw travel ads the same night
those keywords were sitting in a local cache on my phone organized by app with timestamps. TikTok had the most entries. Instagram was second. every single keyword matched a conversation i had out loud near my phone.
the scariest one was "wedding venue." my sister told me she's getting engaged on a private call. i never searched it. never typed it. within a day my explore page had engagement rings and venue tours.
then Claude Code checked a second phone in the same room. my girlfriend's. same keywords. same timestamps. both phones were picking up the same conversation and tagging it independently.
i asked Claude Code how to shut it down. it mapped every app's microphone access and built a permission audit.
what i did:
→ revoked microphone access from every app that doesn't need it to function
→ disabled background app refresh for TikTok, Instagram, Facebook, Snapchat
→ turned off "Hey Siri" which keeps the microphone in passive listening mode 24/7
→ revoked "nearby interaction" permission which uses ultrasonic audio between devices
Claude Code confirmed all four apps lost background microphone access after the changes. i checked her phone too. same steps. took about 3 minutes per phone.
within 48 hours both our feeds went completely random. generic content. nothing personal. nothing from our conversations. that's when i knew for sure it was real.
the full step by step and the prompt are in the first reply. takes 3 minutes. save it so you don't lose it and send it to anyone who's ever said "my phone is definitely listening to me." it is. now you can prove it and shut it down.


Readers added context they thought people might want to know
2 days before, OP claimed to have found spyware on his "wife's phone":
x.com/starmexxx/stat…
Now, in this post, he talks about his "girlfriend":
x.com/starmexxx/stat…
OP has a history of fake AI content:
"Spy camera" found in hotel room: x.com/starmexxx/stat…
Spyware on "friend's computer": x.com/starmexxx/stat…
OP selling AI products: x.com/starmexxx/stat…
Flagged as AI: x.com/i/grok/share/b…
Alexander Conroy retweeted

The future is looking a lot like a few who can responsibly mentally employ the capabilities of AI, an increasingly behind luddite class, and a massive psychosis life-neutering chasm between them. Like the people who cannot master cocaine, and those who can.
“Attention is All You Need”
This is largely now a human concern, with AI doing so much and publishing so quickly human attention is now the last valuable resource, more so than compute.
Companies are desperately seeking it, both on the consumption and production end.
Production: How many projects and how much context switching can your human brain handle in a day?
Consumption: How many products can you pay attention to and buy?
Eventually, most will have no choice but to trust what's created on their behalf and what's purchased on their behalf out of sheer exhaustion and confusion.
Our organic clock cycles can’t keep up this pace, or perhaps evolution will only favor those that can.
Alexander Conroy retweeted

⚠️🚨 THIS IS NOT A DRILL 🚨⚠️
Google has officially declared a bug in Brotli, its tool that shrinks web traffic, CRITICAL: 9.2 out of 10. Last night "Node2Shell" evolved into HTTP2SHELL.
A formal CVE record has been issued citing CVE-2026-111497 -- a hole in versions 1.0.3 to 1.2.0 that can hit any app unpacking data from strangers, and could let them take it over.
What this means:
▪️ This is not a Node.js problem anymore. This is an HTTP PROBLEM.
▪️ Every unpatched app across Node.js, Python, Bun, and Envoy that unpacks Brotli now has a hole attackers need no login to use
▪️ Istio. curl. Python's requests and httpx. All at risk under one CVE.
▪️ EVERY project that bundles Brotli must ship its own fix, and not all are out yet
This changes everything.
A normal bug can be fixed in one place.
A 9.2 bug inside a shared tool cannot.
We just entered the most dangerous phase of this crisis. If you're not paying attention - start now.
Save this. Share this. This is the moment it escalated beyond return.
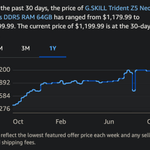
I was looking through my Amazon history and on July I ordered some RAM for $300 and returned it because it was the wrong type of RAM, but that RAM is now worth $1,800 and I'm like oh my god why did I do that, I should have just kept it.
Oh, the 128 gigs of RAM that I ordered for $204 each, so $400, which I still have, I'm not even using, is now worth $1,100 each. Holy shit.
#RAMStreetBets #tothemoon


Every day I use Dot and @grok @bot it keeps getting this nagging feeling that one day they're going to push an update that's going to make the agents more proactive. Then all this crap that they didn't do, they're suddenly going to start doing on my behalf, on my computers, without me knowing, with no logs and no real insight as to what or why it's doing it (because of the lack of clarity in terms of context management, and its intervals of work.)
I really need to remove it from a large majority of my machines and limit access. I do use GrokBot a lot, but maybe I use it as a little bit of a better Grok chat instead of giving it access to remote Into my machines.
The risk vector just feels like it’s getting worse and worse and it’s getting harder to sleep at night.
At least with my own harness, I know what it's doing, and I have logs and control. I don't think people realize how much control and access they've given over to the "cute" machines.
Alexander Conroy retweeted

I've deleted my Grok Bot again. I tried. I really, really, really tried.
Here's my observation:
1) Grok repeatedly chooses the dumbest way to do things. You have to spoon feed it and hold its hand on basic tasks that no other AI struggles with. Down to the point that you have to micro manage it. Unacceptable.
2) Grok has zero consideration for user time. It does things in serial, doesn't check, and you have to constantly check on it like "hey buddy, where is this work?" and it's like "Uhh... oh yeah that process hung..." it's like working with your brother's stoner friend.
3) Grok utterly refuses to discuss which model is backing it. It's got very Woke Right vibes like "you just have to trust me bro" like no, I'm paying for a service, if you're not going to be transparent, I don't care. It's one thing if that model is instructed to be opaque (which is idiotic to start with), but there's no dashboard to see what model you're using.
Grok remains the most disappointing model out there. Full stop.
Alexander Conroy retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.


Alexander Conroy retweeted

PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.

Alexander Conroy retweeted

‼️ URGENT ‼️ Two CRITICAL, unpatched PHP flaws (CVSS 9.2 each) have triggered an emergency warning after alleged exploit details surfaced online.
Researchers report potential RCE.
CVE-2026-109618 and CVE-2026-109619.
Fixes scheduled for October 21, 14:00 UTC.
Details - thehackernews.com/2026/10/ph…

news.ycombinator.com/item?id…
mastodon.catgirl.cloud/@4901…
The private key for all 8 "compromised" CAs is a single byte.
One of the private keys is literally "4".
Freaking humans...
This is also still active, and exploitable, in fact, the Public Key is right there on that catgirl.cloud
Apparently the reason is they essentially used their "test" key to sign it, since they labeled the file names to similarly...really?
#Cybersecurity #intermediateCA #ssl #encryption
Alexander Conroy retweeted

You COULDNT HAVE FUCKING WAITED 14 Hours.
i hope your forever blacklisted from cybersec/related industries for dropping a unpatched critical 1day on twitter you fucking idiot
This quoted post is unavailable.
Holy shit tomorrow is going to be crazy. Updating our server already to prevent the issue before the patch.
If you run ANY PHP TOMORROW YOUR FUCKED IF YOU DON'T UPDATE THIS. You CAN prevent it now by setting session.upload_progress.enabled = Off in php.ini and php_admin_flag[session.upload_progress.enabled] = off in PHP-FPM. #cve #php #programming #emergency

Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…
