

Building https://xitter.cf/t.co/3ep8kajSx0 & https://xitter.cf/t.co/EYODx5C0rT
London, England
Joined April 2008
- Tweets2.3K
- Following1.4K
- Followers361
- Likes1.4K
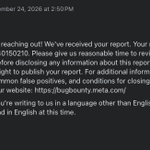


I guess @Meta @metabugbounty has many reports to reply to, or is selective. I reported a @Muse issue more than a month ago. Just an auto-reply so far.


Thank you @Meta @metabugbounty, for the shoutout in your Threads app!
Would love to see the issues fully fixed, though.
threads.com/@meta.ai/post/De…

Also, @AzureCosmosDB website.
Madonna!


We serve data in milliseconds to more than 1.2 billion users across 40 geographic regions.
To reach that scale, we worked closely with @AzureCosmosDB on our storage architecture, achieving a 12x improvement in global median read latency.

It is amazing, not to mention how Cloudflare responds and helps here. Simply amazing.
I still think this helps teams forget the real problem and the need to protect the application from within, rather than applying remediation at external layers.

"I don’t think anyone understands how sophisticated these attacks are"
Not even the attacker?
Ah no, this is all AI driven, autonomously, right.

I’ve seen a lot of people dunking on @thdxr and @opencode, and I needed to say something.
Frankly, I don’t think anyone understands how sophisticated these attacks are. These aren't script kiddies doing this after school. These are state actors, with real companies fueling the fire.
One of the bigger companies behind distillation has 4 office locations worldwide, and there are a number of companies that are entirely fronts for distillation.
You’ve probably seen their ads. Some have raised venture. I’ve personally seen messages claiming they bought over $5 million in inference for distillation.
They’ve gone so far as to recruit people close to the model labs for better access, and the dollars flowing through the distillation ecosystem are in the 9 figures. These attacks offer a huge economic incentive.
These aren't fly-by-night operations. At Vectoral we've see relays offering affiliate programs, net 30 invoicing for enterprises, and strict SLAs. Together, the top relays get tens of millions of visitors per month.
Frankly, they are more sophisticated than most SAAS companies.
The sad reality is that things likely only get worse from here. We are at war for global AI hegemony.
Opus 5.5 medium effort is my default now.
I was mainly using Codex, but something happened, and it doesn't get it right like it used to.
I wonder if it's just my context or a general perception.

Jonathan Santilli retweeted
Your pipeline can deploy to production. So can every step you borrowed from a stranger.
In 2025, one moved tag put the CI secrets of more than 23,000 repositories at risk (CISA, Wiz).
pachx reads every workflow and every step it trusts: tags that can move, secrets handed to third-party steps, tokens that can rewrite your code. On autopilot, it pins, scopes, and locks them down, and the pipeline still passes. A person verifies.
Like the ones that were shared by OpenAI when allegedly attacked Hugging face.

Jonathan Santilli retweeted
If updating dependencies were easy, nobody would ship known vulnerabilities.
The fix usually exists. But updating is work, and nothing anyone can see gets better. So it waits.
pachx starts from your code: every place a package is used, and every line no test covers. It hands that evidence to the coding agent your team already uses, and the tests get written right there. Then you update with proof.

Yo @Muse security matters? Any love left for this report?


Jonathan Santilli retweeted
How many endpoints does your application expose? Be honest.
pachx finds them in the routing code without running anything and follows every input. Is it checked? Where does it end up?
It keeps going in the background; a route added tonight is reviewed tonight. On autopilot, it fixes what it finds across every repository, with evidence for each fix, before and after. A person verifies the result.
Like the agents would follow your exact orders.
Like the agents were a fixed set of rules, one after the other.
Hehe

The most important technology problem of the next 5 years:
Creating a broadly accepted standard for agents to identify themselves to service providers, so that providers can adjust the way they interface with clients (as compared to human-based traffic).
In the interim (i.e., for the next 6 months), there will be a cat-and-mouse game that agents will play -- to circumvent detection and maintain their product's utility during this growth phase.
However, this will only be a stopgap and it will not be the terminal state of the world.
Jonathan Santilli retweeted
Your application isn't one door. It's dozens.
Your code and web APIs. The dependencies you chose, and the hundreds you never did. The containers it ships in. The pipelines that build it. The skills your agents share across the team.
None of it stands still, so the check can't either. pachx maps it straight from the code, checks every front with evidence, not guesses, and a person decides.
I am, or was, not sure, extremely bullish on OpenAI models and Codex.
I am not sure if this is only my perception, but since Astra and Sol 6.1, the results have not been that good. Feels like it needs more supervision.

That's why defenders need so much help understanding and protecting open fronts. @pachx_ai's mission is to help engineers constantly protect application fronts, and there are lots of them.

Attackers only have to get it right once. Defenders have to get it right every time.
At #HumanX, @nikesharora explains why that imbalance and vulnerabilities across enterprise infrastructure will drive a major IT overhaul in the years ahead.
Serious question, in case anyone knows:
How long does it take for Meta/Facebook to reply to a vulnerability report?