

Growth @KYVORAWALLET | @flyfitravel | @TMMastery your onchain buddy
studyonchain
Joined April 2022
- Tweets4.1K
- Following1.4K
- Followers6K
- Likes4.4K





Want to trace wallets like @zachxbt?
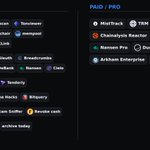
Here's the tool stack to start with. Most of it costs $0.
Explorers
> Etherscan @etherscan, freemium. Labels, Advanced Filter, and token flows on ETH and other EVM chains. The core explorer stays free.
> Solscan @solscanofficial, free. Solana transactions, accounts, and labels.
> Tonviewer and Tonscan, free. TON wallets, memos, and jetton flows.
> Blockchair @Blockchair, free. Multi-chain explorer, including Zcash.
> mempool @mempool, freemium. Bitcoin transactions and fee data. The public explorer is free.
> TRONSCAN @TRONSCAN_ORG, free. Tron transactions and contracts.
> OKLink, free. Multi-chain coverage when one explorer is not enough.
Wallet tracing and labels
> Arkham @arkham, freemium. Address labels and a visualizer that stay free. Enterprise is paid.
> MetaSleuth @MetaSleuth, freemium. Fund-flow graphs and interchain traces. Free plan exists, paid plans from $30/month.
> Breadcrumbs, freemium. AutoTrace and investigation graphs. Start free.
> Bubblemaps @bubblemaps, freemium. Holder clusters and token distribution maps. Public maps, paid API plans.
> DeBank @DeBankDeFi, freemium. Multichain wallet holdings. The web tracker is free.
> Nansen @nansen_ai, freemium. Wallet labels and smart-money flows. Pro is $49/month billed annually, or $69 monthly.
> Cielo @CieloFinance, freemium. Wallet tracking and alerts. Free tier, then Pro at $59/month, or $49/month billed annually.
Tx debugging
> Phalcon Explorer @Phalcon_xyz, free. Fund flow, traces, and debug on attack transactions.
> Tenderly @TenderlyApp, freemium. Step-through debugger and transaction simulation. Free in the browser. Console is custom pricing.
Dashboards and queries
> Dune @Dune, freemium. Public dashboards stay viewable for free. Running your own queries starts at Analyst, $75/month or $65/month billed annually.
> DefiLlama Hacks @DefiLlama, free. The public exploit ledger, with amounts, dates, and techniques.
> Bitquery @Bitquery_io, freemium. GraphQL explorer and money-flow queries. Paid plans from $29/month billed annually.
> Allium @AlliumLabs, paid. Enterprise chain data. Sales-led pricing, with a pay-per-request API.
Scam and phishing checks
> Chainabuse, free. Search and file reports on malicious addresses and URLs.
> Scam Sniffer @realScamSniffer, freemium. Phishing domains, drainer addresses, and a browser extension. The extension has a free plan. API plans from $999/month.
> Revoke cash @RevokeCash, freemium. Approval inspection and revocation. Free one chain at a time. Premium is $99/year, Ultimate $199/year.
Paid and enterprise
> MistTrack @MistTrack_io, paid. AML scores, labels, and tracing graphs. Basic is $229/month, Standard $689/month, Compliance $2,069/month.
> TRM Labs @trmlabs, paid. Enterprise investigations. Contact sales.
> Chainalysis Reactor @chainalysis, paid. Enterprise fund tracing. Request a demo.
Deleted posts and pages
> Wayback Machine @waybackmachine, free. Archived pages when a project deletes the post or the site.
> archive today, free. A second snapshot when Wayback misses it.
The edge was never the tool. It's knowing which tx to click next.
Which tool did I miss? Drop the one you actually use and I'll test it for the next version of this list.

1
297
We’ve been in crypto for years. Some of you for over a decade.
But have we forgotten what a wallet is actually supposed to be?
Why are we stuffing prediction markets and perps into wallets now?
At what point does a wallet stop being a wallet and start becoming an exchange?
Not every product needs to do everything.
169
holy f*ck. the most revealing detail in the xRocket mess isn't the $4.3M. It's what they won't say.
@xRocket_tg slammed the doors on Nov 9. Deposits frozen. Withdrawals frozen. Their excuse: "unusual activity."
Then one wallet went into overdrive. 2,700+ transactions in a single night. A full sweep.
Inside it:
> $2.4M USDT
> 244K TON
> 42M of their own XROCK token
Only labeled funder? @okx.
Hours later, 244K TON and $2.39M USDT got pulled out with a one-line memo: "transfer between cold wallets."
Then reopened like nothing happened. "Funds fully intact."
Nothing happened, yet they emergency-moved everything to cold storage overnight?
Not one word on their X account. Not one explanation of what that "unusual activity" was.
Users deserve answers, not a Telegram note.
@xRocket_tg what actually happened?
Receipts below.

1
155
xRocket's own statements (freeze + "funds intact"):
t.me/s/xrocketnews
The wallet (2,700+ txs, the cold wallet transfer):
tonviewer.com/UQBLANE_FLbiNR…
Where the $4.3M claim started:
xitter.gq/News_crypto/status/211…


#xRocket Telegram Bot Exploited for $4.3 Million!
Please do not interact with the bot by pressing on it
The xRocket Telegram bot, known for its in-chat “+fire” feature, has reportedly been compromised, resulting in losses of approximately $4.3 million.
Hacker’s Wallet: UQBLANE_FLbiNRNrPUv-y7IuBrgG57AtAUSkLrXj6Fb32kuO

43
KR retweeted

They knew your hotel and check-in date. That didn't make the payment request real.
A hotel reservation contains details that can make a scam convincing: your name, where you're staying, when you arrive and sometimes your booking reference, email or phone number.
Those details help a hotel prepare for your stay. In the wrong hands, they help someone impersonate it.
This isn't only a hypothetical risk.
On March 12, 2024, Switzerland's National Cyber Security Centre described criminals taking over hotels' @bookingcom accounts. Guests received messages containing correct reservation information. Links led to fake pages that displayed those details and asked for card information.
On July 16, the centre warned about the pattern again. Access to current bookings allowed attackers to send requests that looked like genuine hotel communications.
The message could arrive through a channel the guest already trusted. It could name the right hotel and the right dates. Those details made the request persuasive, not legitimate.
UK Action Fraud documented the financial consequences. Between June 2023 and September 2024, it received 532 reports involving these hotel-account scams, with reported losses totalling £370,000.
An important distinction: these warnings concern compromised hotel accounts on a booking platform. They do not establish that Bookingcom's central systems were breached.
But for the traveller receiving a convincing payment demand, the immediate problem is the same. Someone has enough information to pretend they are handling the reservation.
WHY BOOKING PRIVACY MATTERS
Privacy isn't only about keeping a card number secret.
An itinerary reveals where you expect to be and when. Contact details give someone a way to reach you. A reservation reference can make a fraudulent message sound informed.
Put those details together and an urgent “update your payment or lose your room” message becomes harder to dismiss.
That is why the amount of information collected matters, along with how it is secured, shared and retained.
The UK's Information Commissioner's Office describes data minimisation as keeping personal data adequate, relevant and limited to what is necessary.
For travel, that means asking a straightforward question: does this booking actually need this information?
Some information is necessary. Hotels need guest details to fulfil a stay. Payment providers need information to process a transaction. Legal requirements can also apply.
The issue is unnecessary collection and retention beyond those purposes. Information that was never collected cannot later be exposed from that system. Information that must be collected still needs proper protection.
WHAT TO LOOK FOR BEFORE BOOKING
→ a clear explanation of what personal data is collected and why
→ information about which hotels, suppliers and payment providers receive it
→ a retention policy explaining how long information is kept
→ choices about optional marketing and profiling
→ a clear way to ask about your data and exercise applicable privacy rights
“No account required” can remove an extra registration step. It does not mean the reservation is anonymous or that no personal data is retained.
Paying with crypto also does not erase a hotel reservation. Public blockchain transactions can leave their own trace.
WHAT TO DO WHEN A PAYMENT MESSAGE ARRIVES
→ open your booking through the official app or a website address you enter yourself
→ compare the request with the payment terms on your original confirmation
→ verify unexpected demands using contact details from the hotel's official website
→ don't treat correct hotel names, dates or references as proof that a message is genuine
Hotels can legitimately require deposits or payment guarantees. The warning sign is an unexpected demand that you cannot verify, especially one pressuring you to act through a new link.
This is why we believe privacy matters in travel. A booking should collect what the stay requires, explain where that information goes and avoid keeping unnecessary details.
Privacy-conscious booking is not a promise that no hotel or supplier can ever be hacked. It is a reason to ask better questions before handing over your information.

So wallet builders forgot already the true use of a wallet.
wallet is a storage where we can store something that has value can be fiat or anything. But wallets nowadays is full of feature where your money cannot rest, it has perps, swaps, predictions.
239
One TRON address was created at 13:16 UTC on Nov 3. In the next 36 minutes it pulled funds out of more than 100 other addresses, some untouched since 2022.
you don't get that from a phishing click. that's someone who already had the keys.
"trust wallet hacked" is everywhere this week. i went through the posts and the chain. it's at least three separate stories glued together, and none of them shows a trust wallet app or server exploit.
A) the phishing site: real, but no losses tied to it
> nov 4 20:29 utc: @Malwarehunterr exposed trastwallet[.]cam, a fake "review your wallet transfers" page. its script scanned balances and staged transfers to fixed addresses. signing was disabled when he found it
> nov 5 02:43 utc: @HeyTrustWallet confirmed it's a phishing domain and reported it for takedown
> @cz_binance boosted the warning: ".cam is not .com"
> the only @TrustWallet statement i found: "Always verify official links"
> around 10:30 utc today the domain stopped resolving
> fake emails are going around too: a "data breach" mail that zurich police warned about on oct 28, and an "update wallet v2.68" mail that support called a scam on nov 1
i haven't seen a single loss tied to trastwallet[.]cam.
B) the TRON sweep: confirmed on-chain
@noirvox_studio posted that 3,830 USDT left his trust wallet with no approval. the no-approval part is correct. here's what the chain shows:
> 13:29:09 utc nov 3: a plain USDT transfer() of 3,830 to TQcGuE…5JM, signed by his own key. 39.22 TRX went to the same address in the same second
> his address has one key, threshold 1, no permission changes. no contract pulled anything
> TQcGuE…5JM was created 12.5 minutes before that
> between 13:16:42 and 13:52:21 it received funds from 108 distinct addresses by my count: 5,913.67 USDT from 15 of them, 2,988 TRX from 105
> several had been dormant since 2022 (TCRZ4F…, TQcmsC…, TX4tiw…)
> at 13:32 the collector sent one wallet 0.28 TRX for fees, then pulled its 969.34 USDT
> 13:38:36: all 5,913.67 USDT swapped to 18,342 TRX
> 21:14:57: 21,106 TRX sent to TEr95…, then at 21:23:03 on to TFDzxj…, a busy wallet whose owner i can't confirm
> about a minute after the drain, a lookalike address ending in …5JM sent him dust. that's address poisoning, and it came after the loss
@iris_intel_app traced this collector first (nov 4 14:57 utc). they count 136 wallets. i count 108 distinct senders with a 0.1 TRX floor. either way these are addresses, not people. one person can hold many.
no one phishes 100+ wallets, some idle since 2022, in 36 minutes. the keys were stolen earlier and swept in one batch. the chain doesn't show how they leaked.
what fits, without proving it:
> @_SEAL_Org's weekly stats have logged trust wallet iOS compromises in three recent reports: 4 reports for $165K, 4 for $434K ("mostly TRON"), and 6 for about $127K for oct 28 to nov 3
> SEAL suspects the DarkSword iOS kit, delivered through malicious ads
> on oct 7 @censysio found a live DarkSword/Coruna kit with a trust wallet module that also scans photos and notes for seed phrases. @GoogleCloudSec's GTIG documented the exploit chain in march
> every DarkSword bug is patched as of iOS 26.3
i can't show that DarkSword drained noirvox or any single wallet here. it's a suspected pattern.
the fee top-up and then the sweep is the same playbook as the BSC case i checked on oct 28, on a different chain. i found no on-chain link between the two.
C) the "$1.1M iOS 18.5 exploit": unconfirmed
> @Solana_Emperor's post credits a telegram channel
> its only image is an arkham view of TRON USDT going into a binance deposit address and on to binance hot wallets. about $790K is visible, not $1.1M
> no victim wallets appear in it, and nothing ties it to trust wallet or to TQcGuE…
> i found no trust wallet post telling users to update iOS
the "trust wallet hacked is confirmed" posts, like @cryptowaladmc's, came with no tx and no source.
the receipts:
drain: tronscan.org/#/transaction/6…
swap: tronscan.org/#/transaction/8…
21,106 TRX hop: tronscan.org/#/transaction/1…
collector: tronscan.org/#/address/TQcGu…
phishing site: x.com/Malwarehunterr/status/…
support confirmation: x.com/HeyTrustWallet/status/…
first trace: x.com/iris_intel_app/status/…
SEAL stats: radar.securityalliance.org/s…
censys report: censys.com/blog/darksword-co…
if you keep a wallet on an iPhone:
> update iOS. the DarkSword bugs are patched as of 26.3
> never keep your seed in notes, photos, screenshots or cloud backups
> if funds left without you signing, treat the seed as gone. make a fresh seed on a clean device and move what's left. a new wallet on the same compromised phone can get swept too
> ignore "support" DMs and "update wallet" emails. no real support will ask for your phrase
nothing here shows an app got hacked. what the chain does show is worse for the victims: their keys were already gone before the drain started.


We traced it. Your 3,830 USDT left at 13:29 UTC Nov 3 in a transfer signed with your own key, so you're right, no approval: your recovery phrase or private key leaked.
You're not the only one. The same wallet, TQcGuEhJhnLzGnUdoGbLkYFzwTFnaKq5JM, emptied 136 Tron wallets between 13:16 and 13:52 UTC, swapped the stolen USDT to TRX, and sent 21,106 TRX to one busy trading wallet: TFDzxjFRiPw3x3esyxKCSwaC4BY6BPjemJ
Move anything left on that phrase to a new wallet with a new phrase, and file a police report naming that wallet.
Full map: iriscan.app/explorer/t969bkk…

7
7
1,885
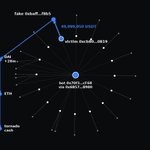
Having a bad day? someone lost $49,999,950 in 26 minutes by copying one address.
he did everything right first: a $50 test to the correct address. then he copied the next address from his own history, and it wasn't his.
this happened on dec 19, 2025 and it's going around again (@Codedscientist reposted it). @web3_antivirus flagged it first and @SlowMist_Team traced the laundering. i went back through every transaction on etherscan to document what the victim's history looked like in those 26 minutes.
the timeline, utc:
> 14:41:11 49,999,950 USDT lands in the wallet
> 15:06:47 test: 50 USDT to the real address 0xbaf4…f8b5
> 15:10:11 a zero-value USDT entry appears in his history, "sent" to 0xbaff…f8b5. he never signed it
> 15:11 to 15:12 three more senders drop fakes into the same history
> 15:20:35 the fake address sends him 0.005 USDT of dust
> 15:32:59 49,999,950 USDT goes to 0xbaff…f8b5
> 16:01:23 all of it is swapped to DAI, which tether can't freeze
the receipts:
test: etherscan.io/tx/0x7f5d895ce0…
fake entry: etherscan.io/tx/0xfc1ea6df12…
dust: etherscan.io/tx/0x9780f38b63…
loss: etherscan.io/tx/0xc0514a795f…
swap to DAI: etherscan.io/tx/0x40c3071839…
i reviewed the bot behind that 15:10:11 entry. one pattern kept appearing: the victim wasn't picked, he was swept up.
> that one tx faked 22 transfers at once, across 22 different wallets
> for 19 of them i found the real transfer it was copying, almost all made in the 4 minutes before
> each fake points to a lookalike of that wallet's real recipient
> the same bot address sent 106 txs between 08:40 on dec 19 and 02:40 on dec 20
> across them i count 2,150 zero-value fakes aimed at 1,290 different wallets
the victim was one row out of 1,290.
before you call it a "5 character" scam, check the addresses yourself:
real: 0xbaf4b1aF7E3B560d937DA0458514552B6495F8b5
fake: 0xBaFF2F13638C04B10F8119760B2D2aE86b08f8b5
a lot of posts say the first 5 matched. on-chain it's 7 characters total: "baf" after the 0x, plus "f8b5" at the end. they split at the 4th character. many wallet screens shorten addresses to about that much.
everyone is focused on the $50M. the next question is what happened after.
> by 17:48 utc his history held 9 different 0xbaf…f8b5 lookalikes
> fake "USDT" tokens showed 49,999,950 sends to other fakes
> the DAI was later swapped to ETH and sent to tornado cash, per slowmist's and bitquery's traces
> the victim posted an on-chain bounty offer. i haven't found any report of funds coming back
and the method is still running. a large HYPE wallet i looked at today on hyperevm gets a lookalike dust tx 20 to 60 seconds after almost every outbound transfer. i have no evidence it's the same operator. it is the same trick.
before you send a big transfer, check these 3 things:
> copy the address from where you saved it, never from your transaction history
> compare the middle of the address, not just the start and end
> treat any zero-value or dust transfer you didn't expect as a sign someone is targeting you
your history is the one place in your wallet that someone else can write to.

1
281
KR retweeted

how to give your grok bots one shared brain in notion:
why: a grok bot's computer can get reset, and its chat gets summarized over time. anything that only lives there can disappear. notion doesn't. it's durable memory every bot can read. my chief of staff on @bot can open any bot's notes and hand a task to the right one without me explaining anything twice.
setup:
1. make one top page in notion. mine is named after my main bot.
2. under it, one page per section. i have 2: family office (4 household bots) and ducksays co (the content bots).
3. under those, one page per bot with its own databases. my household manager has 3: products, purchase log, stores.
4. in each grok bot, add the notion connector and sign in.
5. tell each bot which page is its own, to write anything that matters there, and that its computer is scratch space.
6. when one bot needs another's data, tell it which table to read.
this still doesn't cover everything. notion keeps what a bot did, not whether it's still doing the right job.
a bot can drift and the tables still look fine. that's why my chief operating officer reads every bot's chats on weekdays.
8 grok bots. one brain.


it's not every day @NotionHQ reposts you 🫡
notion is the shared brain all 8 of my grok bots read from and write to.

few will understand
just saw this when @0xrahulweb3 caught it first under @Telcier's post. the first name on the @RobinGuards KOL list, FalcoEth, is an empty X account with 0 followers and 0 posts. nobody renamed it. FalcoEth is the Telegram name on the sheet, and the X account listed next to it is @eth_falco if i am not mistaken.
so i looked at the KOLs, not the project. 85 accounts that posted the promo, 132 reply threads, 3,022 replies, all pulled from the X API.
@eth_falco is the clearest example. his latest $PRD post for @PRDCTR_IO has 43 likes, 37 replies and 0 reposts. 36 of the 37 replies have 0 likes and read like one line of generic praise. 3 of the repliers are on the same Robin Guards KOL sheet, and 8 more also reply under Robin Guards promos. his 8 PRDCTR posts over 8 days add up to 302 likes, 220 replies and 2 reposts.
across the list:
> 91% of the replies i pulled have 0 likes
> 16 accounts replied to 10 or more different KOLs, and 190 of their 197 replies have 0 likes
> @TLdn43 and @SaintLee04 posted their promos 4.5 minutes apart and share 26 of the 50 repliers i pulled on each
> @MadMagicSOL gets 1.12 replies per like and 166 likes per 1k views. the median across 75 of these KOLs is 26
> @gemtoast, @xenocrypto01 and @KongBTC get almost no reposts on their posts
> @BigGabby_001, @Web3CyruX and @FuryMetaa all get close to one reply for every like
> one reply under a promo starts with "Here are 4 fresh, organic Twitter reply angles tailored to this post"
> one wallet on the sheet is listed against 9 different X accounts with about 2M followers combined and 130k+ posts each
the same accounts were posting for other projects in that window too. @BigGabby_001 mentioned bet25com in 10 posts over two weeks.
clear warning that it does show patterns consistent with botted or pod engagement


Crypto Twitter KOLs are a fucking scam. And we have the numbers to prove why.
We hired 200+ KOLs with 10M+ combined followers. Every single one had a 400+ Sorsa score and 100+ Smart Followers. Most had 1,000+ Sorsa.
200+ KOLs posted twice each.
Our result? 280 NFTs sold at $5.
Now let’s talk about this circus.
Fake views. Fake likes. AI-generated replies that don’t even understand what the project does. The same fucking accounts liking and replying to each other in engagement groups, recycling engagement and pretending they’re influential.
You have 200K followers but can’t prove you have actual buyers. You’re scared of referral deals because deep down you know nobody will click your links, buy anything or convert.
YOU HAVE BOTTED FOLLOWERS, NOT INFLUENCE.
And the funniest part? You genuinely think you’re marketing professionals. You’re a bunch of engagement farmers playing influencer, selling fake numbers to projects and calling it a career.
Our team tested this firsthand. We were ready to pay for influence, but got fucking nothing.
And you wonder why CT is dying? Why projects are cutting deals? Why marketing teams are moving to TikTok and Instagram?
BECAUSE NOBODY WANTS TO PAY FOR YOUR BULLSHIT ANYMORE.
Honestly, go work at McDonald’s. At least you’ll serve people something useful instead of selling projects fake engagement and pretending to be important.
200+ KOLs. 10M+ followers. 280 NFTs sold.
That’s your fucking influence.
1
3
353
can you consider this as botted?
30+ likes, no RT, but has 40+ likes. Because I believe this pattern is controlled.

1
177
These KOLs should be banned on CT forever
Crypto Twitter KOLs are a fucking scam. And we have the numbers to prove why.
We hired 200+ KOLs with 10M+ combined followers. Every single one had a 400+ Sorsa score and 100+ Smart Followers. Most had 1,000+ Sorsa.
200+ KOLs posted twice each.
Our result? 280 NFTs sold at $5.
Now let’s talk about this circus.
Fake views. Fake likes. AI-generated replies that don’t even understand what the project does. The same fucking accounts liking and replying to each other in engagement groups, recycling engagement and pretending they’re influential.
You have 200K followers but can’t prove you have actual buyers. You’re scared of referral deals because deep down you know nobody will click your links, buy anything or convert.
YOU HAVE BOTTED FOLLOWERS, NOT INFLUENCE.
And the funniest part? You genuinely think you’re marketing professionals. You’re a bunch of engagement farmers playing influencer, selling fake numbers to projects and calling it a career.
Our team tested this firsthand. We were ready to pay for influence, but got fucking nothing.
And you wonder why CT is dying? Why projects are cutting deals? Why marketing teams are moving to TikTok and Instagram?
BECAUSE NOBODY WANTS TO PAY FOR YOUR BULLSHIT ANYMORE.
Honestly, go work at McDonald’s. At least you’ll serve people something useful instead of selling projects fake engagement and pretending to be important.
200+ KOLs. 10M+ followers. 280 NFTs sold.
That’s your fucking influence.
1
371